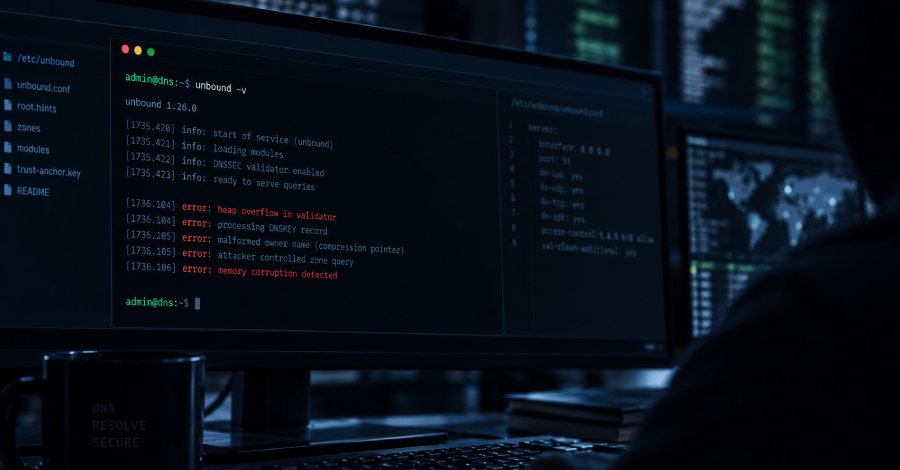

Each launch of the Unbound DNS resolver earlier than 1.26.1 has a important heap overflow in its DNSSEC validator, maintainer NLnet Labs mentioned in an advisory on Wednesday.
An attacker who controls a malicious zone and queries a weak resolver can set off it, enabling distant code execution.
Unbound 1.26.1, launched the identical day, fixes the bug, tracked as CVE-2026-81642, together with eight different flaws. One of many eight, CVE-2026-82717, is a heap corruption bug in CNAME synthesis reported by Ben Morris of Anthropic. It might additionally result in distant code execution “underneath sure techniques and compilation choices,” NLnet Labs mentioned.
NLnet Labs has not reported exploitation of both bug, and CISA’s entry for CVE-2026-81642 marked exploitation as “none” on Wednesday.
NLnet Labs charges the DNSKEY flaw Crucial, with a CVSS rating of 4.0 (9.1), and its scoring lists a community assault vector requiring no privileges or person interplay. NVD listed the CVE as “Awaiting Evaluation” on Wednesday, so the 9.1 is the maintainer’s personal rating.
The overflow occurs whereas the validator digests a DNSKEY report whose proprietor title is a compression pointer into the report’s personal information. The influence NLnet Labs lists is denial of service, with distant code execution attainable “by way of attacker managed information.”
Each model as much as and together with 1.26.0 is affected. That features 1.25.2, the safety launch from July, and 1.26.0, launched on August 4. The Crucial validator bug NLnet Labs fastened in Might, CVE-2026-33278, is a unique flaw, and the 1.25.1 replace that fastened it doesn’t repair this one.
NLnet Labs attaches no configuration situation to that vary, and it has not mentioned whether or not a resolver with DNSSEC validation switched off is reachable.
Improve or Patch
Unbound 1.26.1 is obtainable as supply, with checksums and a PGP signature, and as Home windows installers and binaries. Should you can’t improve, the advisory provides two methods to patch the supply tree:
- Apply the minimal patch or the full patch for CVE-2026-81642 alone with patch -p1, for instance patch -p1 < patch_CVE-2026-81642_with.diff, then run make set up.
- Apply the mixed patch for all 9 fixes as an alternative. A minimal model of it additionally exists.
NLnet Labs says the standalone patches for CVE-2026-81642 and CVE-2026-82717 have been examined and work on 1.26.0. Its safety coverage is to patch the newest launched model.
Debian’s safety tracker listed unbound 1.26.1-1 as fastened in unstable on Thursday, with the bookworm, trixie, and forky branches nonetheless listed as weak.
The 9 Fixes
The launch notes title 9 CVEs. The desk provides each’s affected vary and set off situation in NLnet Labs’ wording.
| CVE | Severity | Affected variations | Wants | Influence |
|---|---|---|---|---|
| CVE-2026-81642 | Crucial | As much as and together with 1.26.0 | An attacker who controls a malicious zone and queries the resolver | Denial of service, attainable distant code execution |
| CVE-2026-82717 | Excessive | As much as and together with 1.26.0 | CNAME synthesis throughout an upstream response. Code execution “underneath sure techniques and compilation choices” | Denial of service, attainable distant code execution |
| CVE-2026-81634 | Excessive | As much as and together with 1.26.0 | A 255-length question title with a big TCP response, from a malicious title server or a tampered response | Denial of service |
| CVE-2026-77955 | Medium | 1.13.2 as much as and together with 1.26.0 | Zones with zonemd-check: sure positioned under, however not at, a belief anchor | Denial of service, a window the place tampered zone information is served earlier than the ZONEMD examine |
| CVE-2026-78227 | Medium | 1.22.0 as much as and together with 1.26.0 | Constructed with –with-libngtcp2 and quic-port configured | Denial of service |
| CVE-2026-80225 | Medium | As much as and together with 1.26.0 | A sustained stream of distinct uncached names over one TCP or DoT connection | Degradation of service |
| CVE-2026-82720 | Medium | 1.12.0 as much as and together with 1.26.0 | Constructed with –with-libnghttp2 and https-port configured. NLnet Labs calls the influence restricted | Denial of service |
| CVE-2026-85501 | Medium | As much as and together with 1.26.0 | Malicious zones serving the ReTrap algorithmic complexity assaults (TagTrap, DelegationTrap, NsecTrap, AdditionalTrap) | Degradation of service |
| CVE-2026-77860 | Low | 1.20.0 as much as and together with 1.26.0 |
The serve-expired code path, bypassing a countermeasure added for DNSBomb |
Might participate in a pulsing DoS amplification assault |
The ReTrap repair additionally adjustments a default: val-clean-additional is now off, so Unbound not validates DNSSEC information within the extra part of a response by default.
The bug was reported to NLnet Labs on August 11 by Yuqi Qiu, who discovered it with Xiang Li at Nankai College’s AOSP Lab, in line with the timeline within the CVE report. NLnet Labs shared a patch the subsequent day and the reporter verified it on August 13. The repair shipped 5 weeks later within the 1.26.1 batch.
NLnet Labs’ safety coverage says that for points not but public it goals to launch fixes “within the order of weeks.”