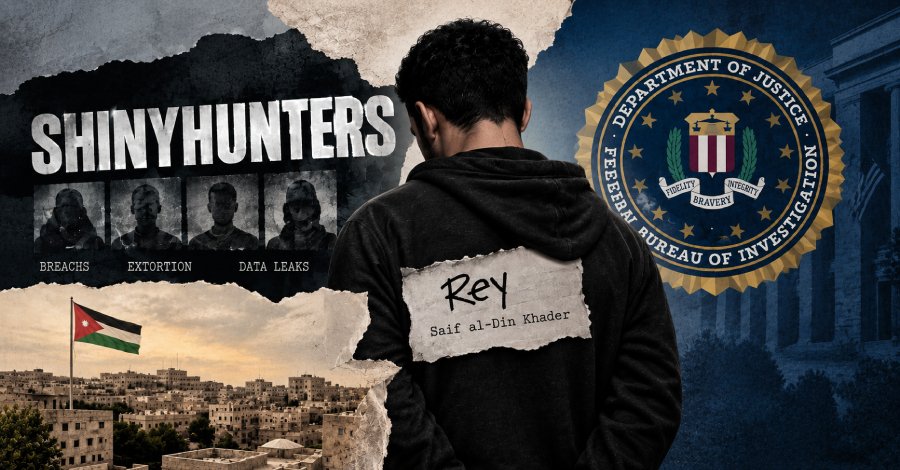

A suspected member of the ShinyHunters digital extortion group, who goes by the web alias “Rey,” has been allegedly detained by authorities in Jordan, Reuters reported, citing three individuals aware of the matter.
Rey, whose actual identify is Saif al-Din Khader, is alleged to have been introduced into custody on September 29, 2026, cooperating with the U.S. Federal Bureau of Investigation (FBI) and regulation enforcement to determine different members of the group.
“His cooperation is vital to ongoing efforts to arrest these hackers,” a supply instructed the information company.
Rey, who additionally glided by the web alias ReyXBF, isn’t an unknown face. In a report printed in November 2025, unbiased safety journalist Brian Krebs labeled him as one of many three directors of Scattered LAPSUS$ Hunters (SLH or SLSH), a gaggle that is assessed to be an amalgamation of Scattered Spider, LAPSUS$, and ShinyHunters.
“Beforehand, Rey was an administrator of the info leak web site for Hellcat, a ransomware group that surfaced in late 2024,” Krebs famous on the time. “Additionally in 2024, Rey would take over as administrator of the newest incarnation of BreachForums.” Khader additionally instructed Krebs that he had been cooperating with regulation enforcement since at the very least June 2025.
The event is the most recent motion within the ShinyHunters saga, which additionally noticed the arrest of a 24-year-old Amsterdam man final week for his or her involvement within the menace actor’s malicious cyber operations.
Though his identification has not been disclosed, unbiased reviews revealed that it was Pepijn van der Stap, a reformed hacker who has been employed as an offensive safety lead on the Dutch firm Neo Safety. A ShinyHunters spokesperson subsequently denied having any connections with van der Stap.
Following the arrest, FBI director Kash Patel mentioned, “FBI groups are actively working with companions to acquire and execute extra leads within the ongoing investigation primarily based on this arrest.” In a follow-up X put up, Patel mentioned, “FBI groups are working new leads RIGHT NOW. Extra arrests are on the desk.”
In latest weeks, the prolific hacking crew has come below the highlight for hijacking the darknet web site of a fellow cybercriminal outfit, Cl0p, by exploiting an unpatched flaw in Grav CMS and its hack of the FBI’s “apply.fbijobs[.]gov” portal, stealing round three terabytes of delicate information.
ShinyHunters insisted that it is not in search of a financial payoff within the FBI case, however relatively apply strain on the FBI to amend what it mentioned have been false allegations in regards to the group and problem claims made by the company about its connections with The Com, a loose-knit cybercrime collective infamous for social engineering, phishing, SIM swapping, extortion, sextortion, swatting, kidnapping, and bodily violence.
“Since final 12 months, this cybercriminal and his co-conspirators have allegedly breached greater than 140 organizations and brought at the very least $70 million in extortion funds,” Brett Leatherman, assistant director of the FBI’s cyber division, mentioned in a recorded assertion. “They usually goal third-party distributors in cloud-based platforms, stealing delicate information and extort victims with threats to publish it.”
Leatherman, who described van der Stap as an alleged chief of the group, additionally urged different members to talk out and mentioned that they’ll now not cover behind perceived worldwide anonymity and evade detection.
“Arrests have a method of adjusting who’s prepared to speak, and seized infrastructure has a method of displaying us who’s left. The longer you keep on this, the extra we study you,” Leatherman added. “You know the way to seek out us, and we all know easy methods to discover you. I recommend you attain out first whereas the selection continues to be yours.”
In a deep-dive report tracing ShinyHunters’ origins and their tactical evolution, cybersecurity corporations Sekoia and Beazley Safety mentioned its lineage goes again to 2 progenitor hacking teams, TheDarkOverlord and GnosticPlayers, that specialised in extortion and information leak operations. The ShinyHunters model emerged publicly round April or Could 2020.
“Six years on, ShinyHunters is much less a gaggle than a model and enterprise mannequin that has outlived its founders,” researchers Enzo Saez and Robert (Bobby) Venal mentioned. “What started in 2020 as a small crew buying and selling stolen databases on RaidForums has grow to be a persistent, self-renewing group that has absorbed indictments, arrests, and discussion board seizures with out ever going quiet for lengthy.”
“That resilience is the true story. It would not come from any single chief or cell, however from a division of labor that has grow to be virtually modular: preliminary entry from social engineers, amplification and recruitment from adjoining actors, and monetization below a shared, recognizable model.”