
Cybersecurity researchers have disclosed particulars of a “human-operated phishing platform” that impersonates promoting merchandise for synthetic intelligence (AI) chatbots like Google Gemini, Anthropic Claude, OpenAI ChatGPT, Perplexity, Meta Muse, and Manus.
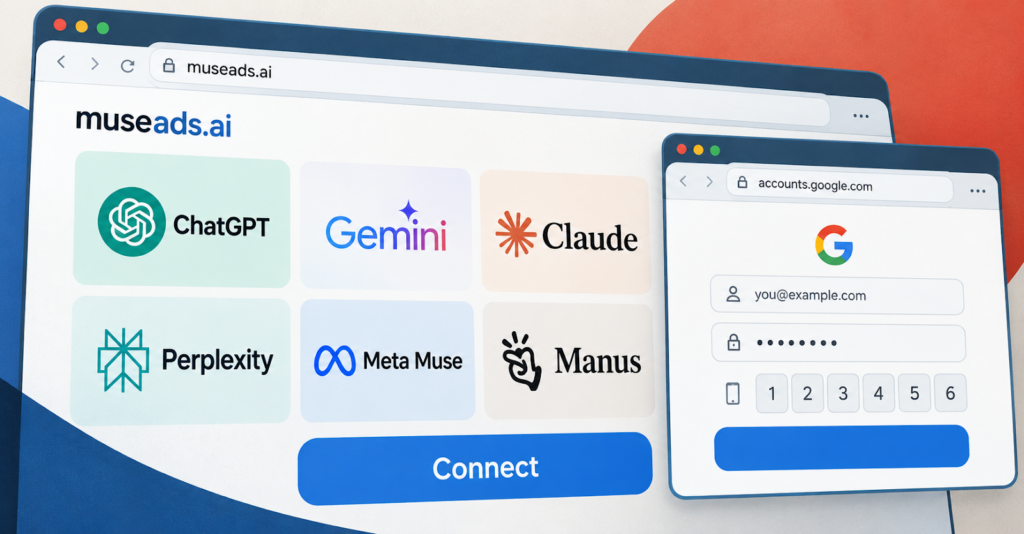
The merchandise, which declare to supply marketing campaign optimization, spend audits, and business-account connections, are designed with one purpose in thoughts: to seize credentials and multi-factor authentication (MFA) codes through spoofed login home windows utilizing the browser-in-the-browser (BitB) trick.
“Every product was constructed across the similar motion: Join,” Island researchers Oleg Zaytsev and Ofek Ronen stated in a report shared with The Hacker Information. “Clicking it opened a browser drawn inside the true browser. The pretend deal with bar displayed trusted origins resembling accounts.google.com or an Okta tenant, whereas the true browser remained on the phishing area.”
“Behind the interface, the platform saved each password try, fingerprinted the gadget, and let an operator decide which MFA problem the sufferer noticed subsequent.”
One of many web sites in query is “museads.ai,” which emerged on September 16, 2026, a bit over every week after Meta launched Muse, its AI agent designed for private workflows. Described as “Your AI adverts supervisor for paid media workflows,” the platform claimed to assist prospects attain consumers, join their advert accounts, and run sponsored placements.
Prominently positioned within the spoofed internet web page is a Immediate Field with a “Join” button, clicking which triggers a BitB assault to seize a customer’s account credentials for Google, Meta, TikTok, and Okta workflows. That is completed by drawing a pretend window displaying a bogus account sign-in type with the deal with bar pointing to a official area (e.g., accounts.google[.]com).
Within the background, the sufferer’s gadget is fingerprinted, and the data is transmitted to the attacker on the endpoint “/api/ship/ip” over Socket.IO, after which operator instructions and sufferer information are exchanged primarily based on the login workflow. Armed with the account credentials, the attacker makes an attempt to sign up to the account in real-time.
“Each model will get its personal pitch,” the researchers defined. “ChatGPT guarantees a Monday Google Adverts temporary. Gemini guarantees MCC (supervisor account) and linked-client help. Claude will get its personal promoting portal, Perplexity provides marketing campaign planning and spend audits, and Manus provides a non-public Meta integration.”

Customers are assessed to be directed to those touchdown pages through pretend invitation emails that impersonate these trusted manufacturers to lend the assaults a veneer of legitimacy.
“Every one on this marketing campaign poses as a plausible product, with its personal model, pitch, and sign-in move,” the researchers identified. “Additionally they transfer with the information.”
Island stated the AI adverts pages are a part of a broader phishing platform that helps a three-pronged operation, the 2 others being Google Adverts-themed refund claims and cost affirmation, in addition to recruitment-related websites for Tesla, Louis Vuitton, Nike, and Adecco.

All of the recognized web sites have been discovered to share the identical know-how stack comprising Subsequent.js and Socket.IO, and talk with the identical endpoints. What’s extra, the menace actors behind the operation have uncovered supply code for earlier variations of the platform by way of misconfigured public GitHub repositories.
The AI ads-focused marketing campaign is designed to focus on company employees, media consumers, and manager-account directors, probably with the top purpose of monetizing the adverts accounts to run their very own advert campaigns or promote them for revenue, particularly after they have a clear spend historical past.
Based on a report revealed by Mimecast in July 2026, malware households like VietCredCare, DuckTail, NodeStealer, and PXA Stealer have engendered advert account theft at scale, resulting in a “widespread commodity crime within the promoting ecosystem” the place unhealthy actors drain enterprise budgets and promote accounts with good popularity in underground markets.
“For the sufferer, the cardboard is the simple half: they’ll take away it inside hours. Getting the account again shouldn’t be,” Island stated. “Attackers usually add their very own directors and downgrade the official proprietor, and restoration can take weeks or months whereas the account retains serving adverts. For a supervisor account, the harm reaches the company’s purchasers.”
To mitigate the menace, organizations are beneficial to allow phishing-resistant authentication, evaluate promoting management adjustments, and scrutinize AI integrations earlier than connecting accounts.
The disclosure comes as Island revealed that menace actors are abusing Google-sponsored outcomes to route unsuspecting customers to customized GPTs or shared-AI chat content material, which then redirect them to a pretend Cloudflare verification web page serving ClickFix-style lures to ship NetSupport RAT.
“The marketing campaign didn’t require a vulnerability in ChatGPT or Google,” Island stated. “It abused trusted platforms, attacker-authored content material, paid search, and social engineering to maneuver individuals towards malware supply.”
“Throughout a three-month statement interval ending in August 2026, the broader supply cluster included about 850 paid-ad landings, 26 lookalike ChatGPT locations, and 71 Google Adverts marketing campaign IDs.”