Cybersecurity has by no means been simple. Threats evolve at breakneck velocity. Company assault surfaces proceed to increase with every new digital funding. Regulatory necessities add further stress on stretched groups. And behind all of it, the unpredictability of human nature means there isn’t any such factor as 100% safety. However the marketplace for safety options doesn’t make issues any simpler for SMBs.
Smaller organizations often have fewer assets and fewer experience to throw on the drawback than their bigger counterparts. However they completely perceive the necessity for superior safety. It’s simply that in addition they need it to really feel easy, guided and manageable. Options and companies that foreground such an method are in brief provide. However they do exist.
SMS perceive the significance of cybersecurity
“Adequate” safety is solely not ok at a time of persistent geopolitical uncertainty and fast technological change. ESET information reveals that three-quarters (75%) of SMBs are involved about international conflicts and cyber warfare. And practically half have skilled no less than one cyber incident up to now 12 months.
Whether or not it’s Iran-nexus menace actors focusing on British energy and US water vegetation, or, as proven by latest ESET analysis, Russia-aligned hackers hitting Polish vitality amenities, state-backed assaults are extra frequent and extra bold than they’ve ever been. SMBs are very a lot within the crosshairs, as suppliers of important infrastructure themselves or suppliers to corporations working in important infrastructure.
However that’s solely half the image. Financially motivated teams proceed to pose an outsized menace, often by way of ransomware or information theft extortion. Typically they function with impunity from hostile states, the place they elude the attain of Western regulation enforcement businesses. There’s rising proof to recommend they even collaborate with authorities hackers on some campaigns.
But the id of the adversary is arguably much less vital than the techniques they’re utilizing to focus on international SMBs. AI is empowering menace actors in every single place to upskill and scale assaults extra affordably than earlier than. They’re transferring by way of the assault chain at velocity, from reconnaissance to exfiltration, collapsing the vulnerability exploitation window, and constructing extremely convincing customized phishing messages.
A brand new wave of autonomous agent-powered assaults will come subsequent. We all know what they’re able to, as a result of they’ve already damaged freed from vendor testing environments to socially engineer victims, create pretend personas, exploit weak passwords, and deploy malicious code. If rogue brokers can do that, then intentionally manipulated agentic AI can too.
AI can also be the goal. As SMBs embrace coding brokers, chatbots and AI-assisted workflows, these instruments are creating a brand new assault floor. Have you learnt what you’re working in your group? Are you able to ensure it’s not being manipulated by malicious third events? And are your customers following coverage once they work together with the know-how? A 3rd (32%) of North American and much more (42%) European organizations admit to having no guidelines in place to limit using AI functions outdoors permitted processes or platforms.
Overwhelmed and overpriced
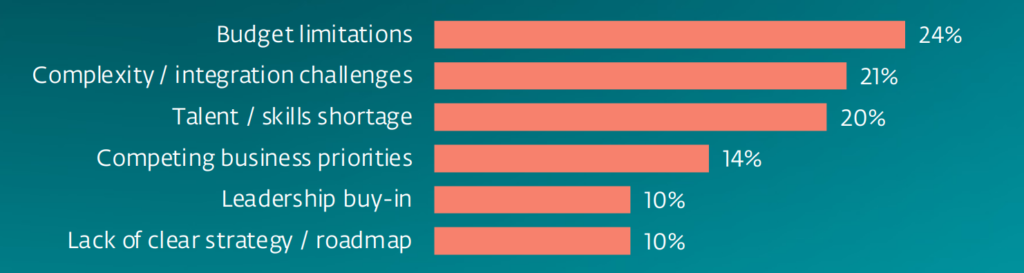
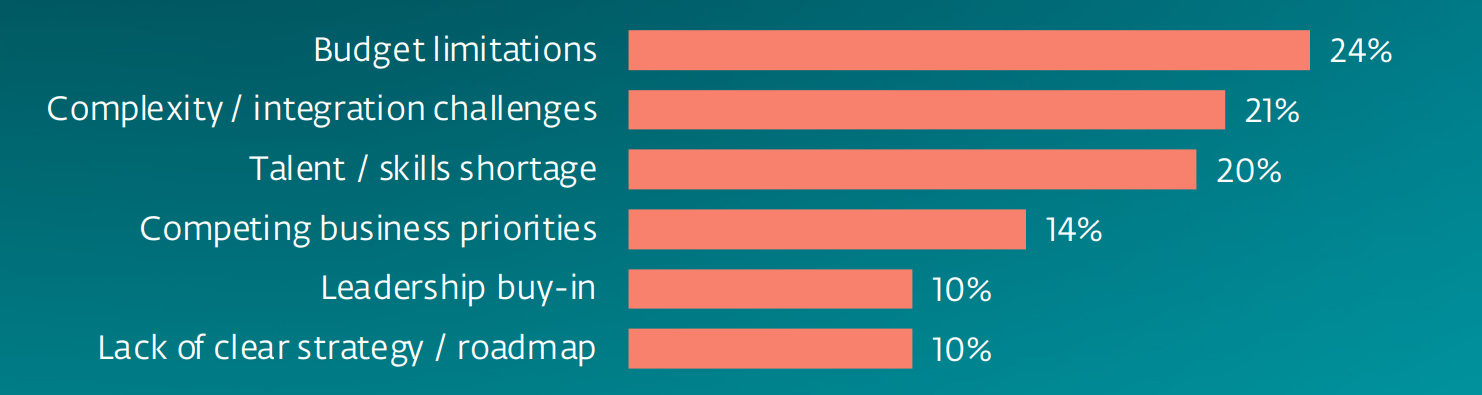
Towards this backdrop, it’s maybe not shocking that ESET finds that 58% of SMBs imagine they’re extra susceptible to cyber assaults than bigger enterprises. It’s not simply that they’re dealing with an unprecedented menace panorama. The stress is operational in addition to technical.
SMBs typically wrestle to make sense of a market full of business jargon, competing advertising claims, and level options which deal with solely slim issues. They purchase extra know-how, however the outcomes don’t enhance.
The common firm may use scores of siloed safety instruments, all pushing out alerts and impressive-looking dashboards. That does nothing however create extra operational overhead, alert fatigue, and coaching gaps. With out the time, abilities and confidence to handle all that know-how, SMBs can shortly develop into overwhelmed. Actual threats slip by way of the online whereas groups waste worthwhile time chasing false positives. Essential safety updates are left undeployed whereas groups patch non-essential programs. Essential instruments are misconfigured.
Decreasing the burden
Smaller organizations need higher safety, not one other safety puzzle to unravel. They want instruments and companies they perceive; which can be easy to function and ship plain-language steering and explanations on how they work and what they’re doing beneath the covers. They need 24/7/365 monitoring to make sure that any menace at any time will be caught and contained as quickly as potential, decreasing the influence on the group. And so they need knowledgeable assist to grasp what threats to prioritize when alerts are flying in and context is in brief provide.
For a lot of, it will imply outsourcing some elements of the safety operate to a trusted accomplice. They might not know the search time period. However for a lot of, the vacation spot needs to be managed detection and response (MDR) which reduces the burden on in-house groups whereas making certain no alert is missed. But traditionally, the SMB market has not essentially been nicely served by MDR suppliers.
Smaller organizations might have felt locked out of a market that usually expenses a premium for his or her capabilities. In spite of everything, in-house 24/7 monitoring and menace searching doesn’t come low cost, particularly throughout a time of abilities shortages.
Then there’s onboarding. Regardless of providing simplicity on the floor, many MDR choices don’t work out like that in follow. They require integration with a number of programs and information sources, the granting of the proper permissions to outsourced SOC employees, the fine-tuning of detection guidelines, incident response planning, and lots of different complicated, time-consuming duties.
What most SMBs need is steady monitoring, detection of suspicious exercise, clear steering on subsequent steps, and consultants available to assist with containment and remediation as required. However in actuality, it may be far more difficult.
For SMBs, that is about discovering worth for cash: safety that delivers the outcomes it guarantees. This issues greater than ever at a time of continued enterprise uncertainty, and the specter of cyber disruption which might have lasting penalties.
All organizations should assume that they’ll be breached in some unspecified time in the future sooner or later, irrespective of how efficient their preventative controls. The important thing to avoiding probably crippling monetary and reputational harm is to comprise and get well from any assault as shortly as potential. Which means discovering safety that helps them make higher choices, not safety that creates extra work.
What SMBs need
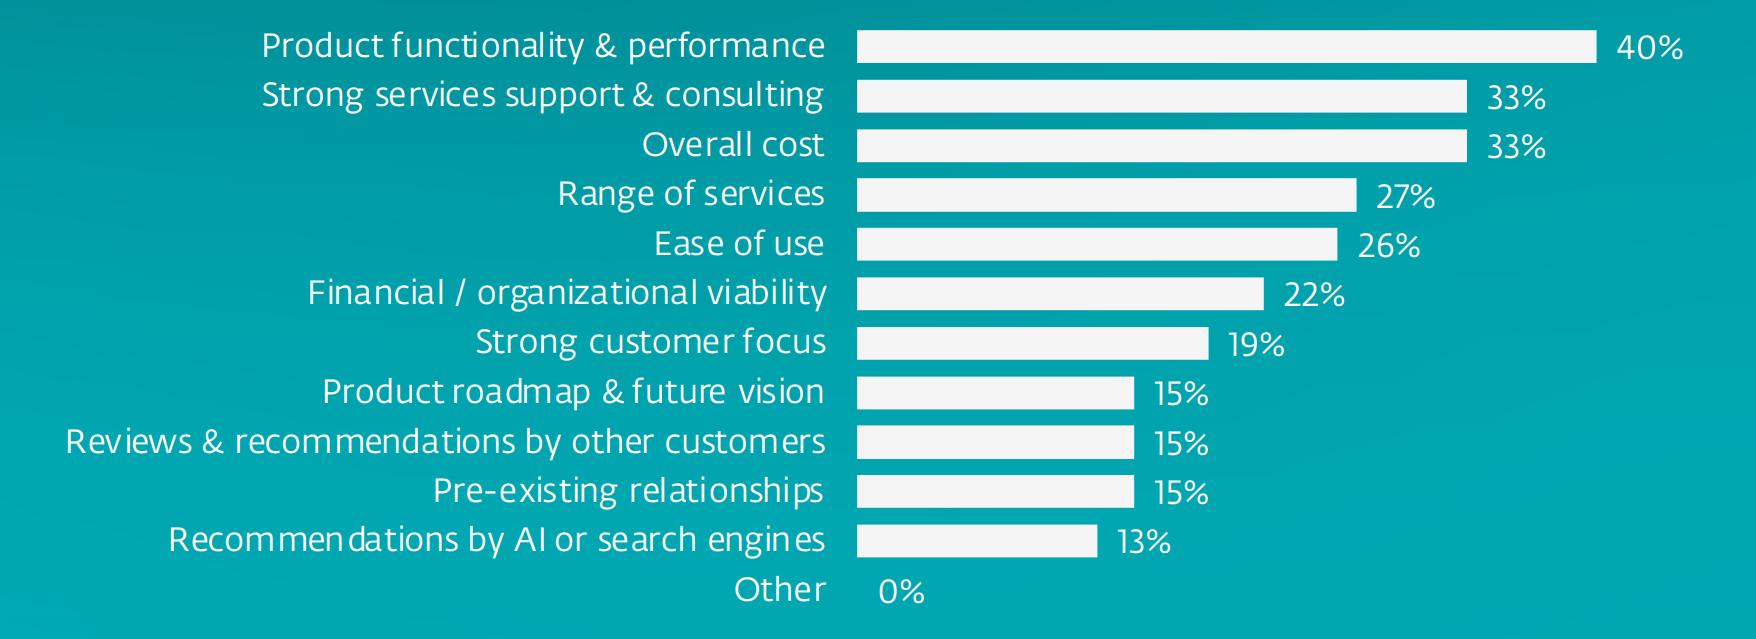
Towards this backdrop, SMBs are in search of a number of complementary capabilities from their safety companions. They need services and products that assist to:
- Decrease the operational burden by absorbing the day-to-day work that in-house groups are struggling to get by way of. A supplier may do that by automating routine processes corresponding to remediation of frequent points. By providing groups AI help to enhance productiveness. And by making certain there’s at all times knowledgeable assist for issues like onboarding and intervening when AI and automation don’t ship.
- Detect and comprise threats quicker to keep up resilience. This functionality should work around the clock, on condition that menace actors more and more look to strike at weekends and through holidays to maximise their efforts. By minimizing dwell time, organizations can scale back the prices related to an incident. IBM calculates that information breaches final 12 months which took beneath 200 days to determine and comprise incurred prices of $4.32 million, whereas these with a lifecycle exceeding 200 days had a mean value of $5.65 million.
- Encourage clearer understanding and higher determination making, by not bombarding the shopper with an excessive amount of technical info. They should know what occurred, how critical the incident is, what the service supplier has performed to remediate, and what else must be performed by their group. An excessive amount of info can cripple response efforts.
- Ship stronger operational continuity with a system which is able to assist resilience by stopping incidents the place potential, limiting the influence once they do happen, and making certain the corporate can preserve minimal viable operations whereas recovering swiftly. SMBs have a smaller margin of error than giant enterprises, making fast restoration key to preserving buyer belief and minimizing the monetary influence.
- Drive quicker time to worth by way of fast onboarding and deployment, making certain the SMB can begin benefitting from the service as quickly as potential. AI and automation may also help right here, and make sure the publicity window is stored as brief as potential.
- Encourage safer AI adoption by making certain that every one AI in use within the group is managed and ruled securely. Which means first understanding what’s in use within the group, what information is being fed into it, and (within the case of brokers) what it will possibly entry. Then understanding insurance policies and controls to reduce danger. A secondary layer of safety works to cut back leakage dangers and immediate injection or information poisoning in order that current programs can’t be hijacked by malicious third events.
- Enhance safety throughout the company assault floor, which might embrace id, collaboration instruments, distant entry, AI utilization, SaaS apps, cloud infrastructure and extra. A trusted supplier will assist to handle danger throughout this distributed and sophisticated IT surroundings, which might stretch from distant worker laptops to cloud servers. Menace actors are previous masters at discovering gaps in safety, so protection have to be complete.
- Ship the suitable method for every particular person group, as a result of no two SMBs are the identical. They’ve totally different danger profiles, assault surfaces, IT maturity ranges and budgets. For some, automated safety is enough. For others, a white-glove safety relationship with complete assist is a greater match. The secret is providing selection with out confusion, and companies aligned to the shopper’s danger urge for food.
The case for supervised safety
What this interprets into is friction-less, supervised safety for the AI period.
Friction-less as a result of it ought to scale back pointless friction when it comes to buying, deployment and use. And supply sturdy safety with out the necessity to interpret complicated technical alerts or combine disconnected level options. Supervised, as a result of it ought to supply a mix of AI, automation and devoted human oversight, making certain the shopper is within the driving seat however with an knowledgeable navigator by their aspect. And “safety for AI” as a result of it ought to leverage AI to boost prevention, detection, response, correlation, investigation, and effectivity. Nevertheless it also needs to have capabilities to cut back danger throughout the shopper’s AI assault floor.
AI is altering the sport for safety. Nevertheless it ought to by no means be handled as a characteristic, or a advertising message. It needs to be embedded into the material of what a trusted safety accomplice delivers. To not exchange human experience, however to boost it the place vital, making groups extra productive and catching threats which their eyes may miss.
Finally, SMBs need confidence that they’re higher protected, supported, and ready. That they’re doing the whole lot they will to reduce an intrusion. And that, if a breach does happen, that they will get well as shortly as potential. Past this, they should really feel this confidence with out the operational burden that’s hurting so many smaller organizations. As a result of safety ought to on the finish be a enterprise enabler. Not a burden on progress and innovation.
The market is evolving. A greater method is accessible for SMBs. You simply want to seek out the suitable safety companions; these which focus particularly on assembly the wants of the mid-market with easier options that ship supervised cybersecurity outcomes.