
Cybersecurity researchers have disclosed particulars of a beforehand unseen variant of the DarkSword iOS exploit equipment referred to as P7 DarkSword.
“In contrast with the variants we often observe, P7 reduces its on-device footprint, provides on-device keychain and crypto-wallet theft, and provides two means C2 communication with the attacker’s infrastructure,” iVerify stated in a brand new report revealed Thursday.
The identify “P7” is a nod to the menace actor’s use of the “p7_” variable prefix in modifications made to the unique DarkSword code.
DarkSword was first publicly documented earlier this March by Google Risk Intelligence Group (GTIG), iVerify, and Lookout, detailing its skill to focus on iPhones operating iOS variations between iOS 18.4 and 18.7. The equipment was detected within the wild in November 2025.
The toolkit is engineered to chain a number of iOS vulnerabilities to flee the browser sandbox, escalate to kernel privileges, and inject the principle payload into SpringBoard, the iOS course of that handles app launches and the house display screen. The exploit chain is assessed to be a business product that by some means landed in a second-hand market, from the place it was acquired by financially motivated operators and different menace actors since late 2025.
The exploit equipment has been put to make use of in assaults concentrating on Saudi Arabia, Turkey, Malaysia, and Ukraine by a number of menace actors, together with a Turkish business surveillance vendor named PARS Protection by way of a faux Snapchat-themed web site and a Russia-aligned menace actor referred to as Star Blizzard (aka COLDRIVER) utilizing faux invitation lures.
In August 2026, assault floor administration platform Censys detailed a marketing campaign mounted by an unknown Chinese language-speaking menace actor that concerned concentrating on Apple iOS gadgets with the exploit equipment, along with serving an Apple ID decoy sign-in web page.
As lately as final month, iVerify stated it noticed “a number of unsuccessful, possible LLM-assisted makes an attempt to replace the framework to help iOS 26.x,” fueled by the leak of the exploit equipment shortly after its public disclosure. These variants, the cellular safety firm added, are centered on stability, stealth, and high quality of stolen knowledge.
iVerify instructed The Hacker Information that it has additionally seen DarkSword and Coruna bundled collectively on uncommon events, calling the mixed deployment DarkCoruna.
“We consider these attackers obtained the supply for the Coruna exploit equipment and modified it,” iVerify stated. “There have been no indicators of binary patching concerned and huge code modifications had been finished and compiled into new binaries.”
“Many bundled variants we see are non-working AI slop makes an attempt. Non-sophisticated attackers are deploying damaged/non-working variations of patched Coruna and DarkSword from GitHub. Nonetheless, we won’t rule out the chance that attackers unable to acquire the Coruna supply code would possibly reverse-engineer and re-implement Coruna with the assistance of LLM fashions, we simply do not have proof of this occurring but.”
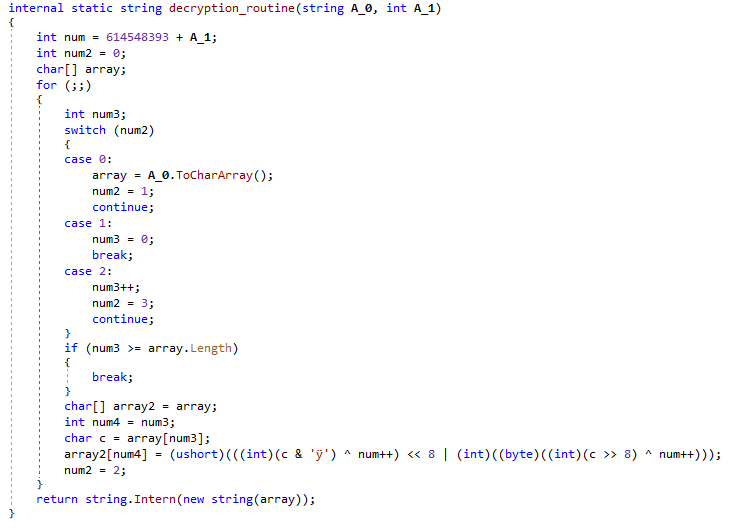
P7 DarkSword represents an evolution in these elements by eliminating debug logging over HTTP requests and syslog and utilizing browser localStorage to stop re-exploitation. Not like prior variants that copied and exfiltrated the keychain database to course of on the attacker’s infrastructure, the brand new model extracts keychain knowledge into JSON on the telephone previous to exfiltration.
“The implant is injected into the SpringBoard course of, which handles all communication with the attacker’s infrastructure,” iVerify stated.
The most recent iteration is supplied to ballot for instructions each 15 seconds, ship a “heartbeat” message, ship an inventory of put in functions, and transmit iCloud Keychain info and knowledge from functions like Apple Notes, Images, and cryptocurrency wallets.
The response to the periodic tasking ballot comprises instructions to be executed on the sufferer’s telephone. This contains –
- execute_command, to execute working system instructions like ls, dir, cat, mkdir, rm, echo, ps, memdump, ipconfig, netstat, and whoami, amongst others
- ls, to checklist listing contents
- obtain, to learn a file from the system and add it to the C2 server
- pictures, to add photograph information from “/var/cellular/Media/DCIM”
- apps, to enumerate app containers and extract bundle IDs
- exec, to execute arbitrary JavaScript straight contained in the implant runtime
- file_upload, to recursively scan a number of paths and add matching information
- basic_info, to ship system metadata to the C2 server
- disk_scan, to recursively scan the filesystem ranging from “/,” report metadata for information, directories, and symlinks, and add the knowledge within the type of a report
- ios_app_data, to seek out app sandbox and app-group containers for requested bundle IDs and add chosen app information
- wallet_scan, to scan for put in pockets apps
- wallet_extract, to extract wallet-related knowledge for imToken pockets app
- memo_scan, to add Apple Notes databases
- photo_scan, to add pictures from Apple Images
- sleep, to change the beacon polling interval
- exit, to halt the beacon loop and cease the implant
Apparently, the identical P7 DarkSword exploit has been noticed being distributed by way of a site related to a now-defunct Czech e-commerce analytics startup. In accordance with Report URI, unknown menace actors have re-registered the area (“ecomtrack[.]io”) on September 15, 2026, following its expiry, to contaminate websites nonetheless incorporating monitoring tags referencing the analytics product with malicious JavaScript that delivers the malware.
“With the tag nonetheless sitting on on-line shops, it now hijacks guests, sells them on to advert networks, and in a single case, it delivers a full iOS exploit chain and spy ware implant,” safety researcher Scott Helme stated.
The brand new JavaScript incorporates numerous evasive measures to detect crawlers, headless browsers, and bots, utilizing cloaking ways to feed them empty content material to cover its tracks. It additionally collects details about the system and browser and sends the main points to an exterior server, after which the customer is redirected to a rip-off website or a web-based on line casino.
One route results in a bogus cryptocurrency buying and selling platform (“chainmate[.]high”) that stealthily serves the DarkSword iOS exploit chain. The implant delivered by way of the DarkSword is designed to seize SMS, contacts, name historical past, voicemail, pictures, Apple Well being knowledge, location historical past, notifications, saved Wi-Fi passwords, and information belonging to greater than 25 pockets apps.
“The recovered code is configured to contact mertio.cc each 30 seconds and deal with instructions together with exec, obtain, pictures and spy,” Helme stated. “The construct we recovered seems to be newer (v24), and it stories to totally different infrastructure and targets way more crypto wallets.”
The disclosure comes as Censys stated it recognized open directories on 5 hosts carrying elements associated to DarkSword and Coruna, one other iOS exploit equipment uncovered this 12 months as weaponized in assaults geared toward iPhone fashions operating iOS variations between 13.0 and 17.2.1.
“Coruna is the companion payload equipment the identical ecosystem distributes,” Censys stated. “Its levels run contained in the sufferer’s browser session after DarkSword’s exploit levels land, and its wallet-harvesting modules steal crypto restoration phrases, balances, and keystore knowledge from iOS apps. Operators run DarkSword and Coruna collectively towards their very own C2 infrastructure.”

The 5 hosts are listed under –
- 43.134.165[.]205, which serves DS-Fusion v1.0 (aka DarkSword Fusion), a mixed bundle that features each DarkSword and Coruna in a single bundle
- 166.88.95[.]90, which operates as a C2 server of the implant and has recorded two actual Chinese language iOS gadgets (183.154.173[.]30 and 182.239.114[.]223) polling a beacon web page each three seconds for a number of hours on September 6, 2026
- 23.148.212[.]237, which serves as an evaluation workspace that exhibits the operator creating exploit chains for iOS 26 (akin to for CVE-2026-31001), which aren’t lined by DarkSword or Coruna.
- 47.102.192[.]23, which serves as a staging host for the Coruna equipment
- 156.239.230[.]120, which exposes the whole C2 platform and has been noticed polling a tool on September 15, 2026
An evaluation of the manufacturing server’s exploit registry has revealed that the DarkSword exploit equipment includes two CVE identifiers not beforehand documented –
- CVE-2025-24201, an out-of-bounds write vulnerability within the WebKit engine that would enable an attacker to interrupt out of the Net Content material sandbox (Mounted in iOS 18.3.2 and iPadOS 18.3.2)
- CVE-2025-31200, a reminiscence corruption vulnerability within the Core Audio framework that enables code execution when processing an audio stream in a maliciously crafted media file (Mounted in iOS 18.4.1 and iPadOS 18.4.1)
It is suspected that the open-directory cluster and the 156.239.230[.]120 platform are run by a Chinese language-speaking menace actor with an intention to conduct cryptocurrency pockets theft. That stated, precisely who’s behind is unknown.
“The platform runs a Chinese language-speaking exploitation-as-a-service operation,” Censys researcher Aidan Holland stated. “The admin panel exposes an agent/reseller mannequin, and a replica of the manufacturing server recovered 11 sufferer restoration phrases, 179 system loot directories, and a 75-account control-plane roster.”
Censys stated it additionally detected a separate China-based operator operating the identical equipment within the wild towards its personal C2 server at “66ds[.]lol,” whereas together with a brand new cryptocurrency pockets goal (BitKeep) not current within the open-directory set. The findings as soon as once more spotlight the proliferation of the equipment amongst financially motivated actors.
“The operator behind it sits on Tencent and Shenyang internet hosting, tied to the operator by means of a novel self-signed certificates authority,” Censys stated.
(The story was up to date after publication to incorporate extra insights from iVerify and Report URI.)