Govt abstract
This report analyzes exercise throughout which UAC‑0099 gained preliminary entry on July 16th, 2025 and handed it off to Sandworm, which then performed a data-wiping assault on September 17th, 2025. It notably focuses on the MythicRatatoskr backdoor, which is exclusive in its use of the Yggdrasil mesh community to speak with a C&C server hosted inside it.
We introduced our findings about MythicRatatoskr at LABScon on September 18th, 2026, and on the Virus Bulletin convention on October 16th, 2026.
Key factors of this blogpost:
- On July 16th, 2025, UAC-0099 gained preliminary entry to a grain logistics firm in Ukraine through a spearphishing e mail with a malicious attachment, resulting in the execution chain of the MATCHWOK backdoor.
- At some point later, the attackers deployed MythicRatatoskr, a beforehand undocumented backdoor that communicates with a C&C server hosted contained in the Yggdrasil mesh community. We’ve got not seen the backdoor used anyplace else, and we discovered indications {that a} Linux variant can also exist.
- Yggdrasil is a decentralized mesh community that implements an experimental routing scheme by which the IPv6 communication between the nodes is end-to-end protected.
- In the end, UAC-0099 handed off entry to Sandworm, which then carried out a data-wiping assault.
Cooperation amongst Russia-aligned actors
The handover documented on this report isn’t an remoted phenomenon. As famous above, Sandworm is attributed to GRU Unit 74455, and UAC-0099’s focusing on leads us to evaluate that it’s aligned with Russian pursuits.
Earlier in 2025, we uncovered that Russia-aligned Gamaredon collaborated with Turla, one other Russia-aligned menace actor; we documented our findings in our blogpost Gamaredon X Turla collab. Each teams are linked to the Federal Safety Service of the Russian Federation (FSB). This type of cooperation underscores the potential for coordinated cyberespionage campaigns amongst Russia-aligned teams, seemingly supposed to amplify their operational impression. Prior to now, Gamaredon collaborated with a menace actor that we found and named InvisiMole. Towards that backdrop, a UAC‑0099-to-Sandworm handoff is uncommon within the particular actors concerned, however not stunning as a sample.
Overview of the intrusion
In keeping with ESET telemetry, the occasions unfolded as follows: at 06:59 on July 16th, 2025, a scheduled job named pdfopentask was executed on one machine within the goal group. It executed a PowerShell payload from %temppercenttemporarydoc.txt.
A minute later, MATCHBOIL was deployed. MATCHBOIL is a downloader that deployed, on this case, the MATCHWOK backdoor (C&C: https://uztickets[.]com) from https://egyptanimals[.]com/animals/photoalbum. The next day, at 09:28, a brand new binary was delivered to the machine: the MythicRatatoskr backdoor. Because of the shut proximity of time, we consider with excessive confidence that the MATCHWOK execution chain led to the deployment of MythicRatatoskr. Our telemetry additional reveals that further MythicRatatoskr samples have been subsequently deployed to different machines inside the group, this time utilizing an OpenSSH SFTP server.
Later, ESET telemetry detected a SOCKS5 server on among the machines, with one pattern having been extracted from an unknown archive utilizing WinRAR. We consider that the SOCKS5 server was deployed utilizing MythicRatatoskr.
Roughly two months later, on September 17th, 2025, we detected data-wiping exercise on the compromised grain logistics firm. The information-wiping assault was executed by deploying the SDelete utility through Energetic Listing Group Coverage – customary Sandworm ways, strategies, and procedures (TTPs) that now we have noticed quite a few occasions in ESET telemetry.
Subsequently, we assess that UAC‑0099 can act as an preliminary entry group for Sandworm.
This blogpost focuses totally on the evaluation of the MythicRatatoskr backdoor, the Yggdrasil community that hosts its C&C server, and the accompanying SOCKS5 server. The primary variations of MATCHBOIL and MATCHWOK have already been analyzed by CERT‑UA in its advisory, with MATCHBOIL and its evolution additional lined in our blogpost MATCHBOIL: New tips, usual evil intentions. These instruments are subsequently omitted right here.
A squirrel on the earth tree
The phrase Yggdrasil originates in Norse mythology, the place it refers to a sacred tree connecting the varied realms of the cosmos. Inside that tree lives a squirrel named Ratatoskr that carries messages between its prime and its roots. Given the backdoor’s position as a messenger scurrying via the Yggdrasil community, we determined to call the backdoor MythicRatatoskr.
Extra technically, Yggdrasil is a decentralized mesh community that connects gadgets straight to one another and not using a central hub, constructing an encrypted IPv6 overlay on prime of the web in order that collaborating nodes can alternate end-to-end-protected visitors. Respectable customers undertake such meshes for resilient connectivity, analysis, and passion networking. As a result of no single server runs the mesh, the community is powerful and exhausting to disrupt – properties that additionally make it enticing to adversaries. Importantly, Yggdrasil isn’t designed to supply anonymity.
Attribution
The post-compromise execution chain relied on recognized malware already attributed to UAC‑0099 – specifically the MATCHBOIL downloader and the MATCHWOK backdoor – which leads us to attribute this stage of the assault to UAC‑0099 with excessive confidence. We attribute the data-wiping exercise noticed two months later to Sandworm, additionally with excessive confidence, based mostly on the TTPs concerned.
Furthermore, we assess with excessive confidence that UAC‑0099 handed off entry to Sandworm sooner or later through the intrusion, though now we have not but been in a position to decide whether or not the MythicRatatoskr backdoor was operated primarily by UAC‑0099 or by Sandworm.
UAC‑0099 profile
UAC‑0099 is a cyberespionage group focusing on governmental organizations, monetary establishments, and media, all in Ukraine. Primarily based on the focusing on, we consider with medium confidence that the group is aligned with Russian pursuits. UAC‑0099 can act as an preliminary entry dealer for Sandworm, a Russia-aligned group finest recognized for its harmful assaults in Ukraine.
The group has been energetic since at the least 2022 and was first reported by CERT‑UA in June 2023. Aside from MATCHBOIL, the group additionally sometimes deploys LONEPAGE, a PowerShell downloader named after the presence of the phrase web page in its C&C URLs.
Sandworm profile
Sandworm is a Russia-aligned menace group that performs harmful assaults. It’s principally recognized for assaults in opposition to Ukrainian power corporations in December 2015 and December 2016, which resulted in energy outages. In June 2017 Sandworm launched the NotPetya data-wiping assault that used a supply-chain vector by compromising the Ukrainian accounting software program M.E.Doc. In February 2018, Sandworm launched the Olympic Destroyer data-wiping assault in opposition to organizers of the 2018 Winter Olympics in Pyeongchang.
The Sandworm group makes use of such superior malware as Industroyer, which is ready to talk with gear at power corporations through industrial management protocols. In April 2022, CERT‑UA thwarted an assault in opposition to an power firm in Ukraine the place the Sandworm group tried to deploy a brand new variant of this malware, Industroyer2.
Since February 2022, Sandworm has been very energetic in Ukraine, by deploying knowledge wipers in opposition to strategic organizations.
In October 2020, the US Division of Justice printed an indictment in opposition to six Russian laptop hackers that it alleges ready and performed numerous Sandworm assaults. As we already talked about, the group is often attributed to GRU’s Unit 74455.
Compromise chain
Preliminary entry and execution
In keeping with ESET telemetry, preliminary entry was gained through a spearphishing e mail with a malicious attachment – a discovering that matches CERT‑UA blogpost. We assess that the MATCHWOK backdoor execution chain (already documented within the CERT‑UA blogpost) then led to the execution of MythicRatatoskr, a backdoor that communicates with its C&C server over the Yggdrasil community. Subsequently, the attackers in all probability used MythicRatatoskr to ship a SOCKS5 server.
Persistence
MATCHBOIL persists MATCHWOK by including the registry worth UpdateMonitor to the registry key HKCUSoftwareMicrosoftWindowsCurrentVersionRun, with knowledge pointing to the dropped MATCHWOK path.
MythicRatatoskr is began as a Home windows service with the identify ieupdate.
Assortment and exfiltration
Throughout check-in, MythicRatatoskr sends details about the present person, hostname, and native community settings to the C&C server. As well as, the operators can use MythicRatatoskr to exfiltrate information and screenshots to the C&C server by utilizing HTTPS routed via the Yggdrasil mesh community. The information isn’t staged previous to exfiltration.
Toolset
MythicRatatoskr
MythicRatatoskr is a backdoor written in Go that makes use of the Yggdrasil community (described within the Community protocol part) to succeed in its C&C server. As famous earlier, we named the backdoor after Ratatoskr, the squirrel from Norse mythology that scurries via Yggdrasil – the sacred tree connecting the realms of the cosmos – carrying messages between its prime and its roots. We felt this was a becoming parallel for a backdoor that ferries knowledge throughout the Yggdrasil community. There are indicators within the binaries suggesting that the event began someday between December 2024 and February 2025.
Operate names left within the binaries – following a mixture of combined caps (CheckInAgent) and snake case (agent_run) – recommend both code merged from one other undertaking or inconsistent naming by the authors. Key features deal with service registration and Yggdrasil community initialization (foremost, runService), check-in and beaconing (agent_run, init_agent, CheckInAgent), configuration dealing with (saveConfig, Encrypt, Decrypt), command polling and dispatch (getTasks, doTask), and the backdoor instructions themselves (add, obtain, screencat, shell, manageProxy, and many others.).
Some samples additionally embrace a 10-minute startup delay, prone to keep away from instantly connecting to the Yggdrasil community on execution, serving to to evade detection.
Host-based artifacts
Desk 1 presents MythicRatatoskr host-based artifacts that we noticed throughout our evaluation. Observe the filename collision for krbtman.exe: it’s MythicRatatoskr on some machines, and the SOCKS5 server on others.
Desk 1. Host-based artifacts related to MythicRatatoskr
| Title | Worth |
| Set up paths | C:windowssystem32updater.exe |
| C:Windowssystem32krbtman.exe | |
| C:windowssystem32windowsdefendersvc.exe | |
| %localappdatapercentMicrosoftOneDriveOneDriveLiveUpdater.exe | |
| c:program information (x86)microsoft.netadomd.net110applicationasphost.exe | |
| C:OFFICE2010UtilitiesAct64.exe | |
| %userprofilepercentDownloadsWindowsDefenderSvc.exe | |
| %userprofilepercentDownloadsieupdate.exe | |
| %userprofilepercentDownloadsie.exe | |
| %userprofilepercentAppDataLocalInternet Explorerieupdate.exe | |
| %userprofilepercentAppDataLocalieupdate.exe | |
| Configuration paths | C:WindowsTemp.updatecache |
| C:Windowssystem32.updatecache | |
| %LocalAppData%/Temp/.crond (Analyst word: ahead slashes are attackers’ typo) |
|
| Service names | ieupdate |
Persistence
In keeping with Home windows occasion logs obtained from the compromised machines, updater.exe and WindowsDefenderSvc.exe have been began, and thus seemingly endured, as Home windows providers.
Community protocol
To speak with the C&C server, MythicRatatoskr depends on the Yggdrasil community – a decentralized mesh community in an alpha state that implements an experimental routing scheme. Every node within the community generates its personal Ed25519 key pair, which permits protected end-to-end IPv6 communication between the friends. The IPv6 handle is derived from the general public key within the 200::/7 subnet vary, which was deprecated by IETF in 2004. Anonymity isn’t among the many targets of the undertaking. We discover this subject extra within the Community infrastructure part.
The yggdrasil-go repository already supplies the required sorts and strategies to affix the Yggdrasil community. There’s additionally one other undertaking, referred to as yggstack, that allows the Yggdrasil community to speak through a community stack within the person house. This has the advantage of not needing to create a tunnel interface, which may be a difficulty if the person doesn’t have the required privileges to create one, or if such an interface isn’t supported on the system. The MythicRatatoskr code relies on yggstack, making the malware transportable.
There’s a publicly obtainable community that one can be a part of by including at the least one public peer into the Yggdrasil configuration. MythicRatatoskr particularly incorporates an embedded base64-encoded blob that incorporates an inventory of public friends within the URI format. Most friends on the record are nonetheless operational. MythicRatatoskr randomly picks three friends from the hardcoded record, which is the advisable quantity, and connects to them with the intention to be a part of this public Yggdrasil community.
As soon as MythicRatatoskr is a part of the Yggdrasil community, it communicates with its C&C server, which can be a part of the community, through HTTPS on port 443.
Communication makes use of JSON-encoded HTTP POST requests containing a uuid (defined in Desk 4, within the MythicRatatoskr foremost configuration part), a message kind, and optionally available knowledge. 4 message sorts exist:
- checkin – register the backdoor and ship sufferer metadata akin to username, hostname, and native IPs; the server responds with a contemporary uuid and psk),
- tasking – ballot for brand spanking new instructions,
- outcome – return command output, base64-encoded when current,
- and getfile – retrieve file content material for the add command.
Though the C&C server is hosted within the Yggdrasil community – which can forestall community safety instruments from detecting outbound connections to it – blocking the general public peer addresses is a viable mitigation.
Configuration
We distinguish between two forms of configuration:
- a backdoor-specific configuration utilized by the malware itself; and
- an Yggdrasil configuration used to affix the mesh community.
MythicRatatoskr foremost configuration
The MythicRatatoskr configuration is saved in a file at a hardcoded path. The trail can differ in every pattern; we recognized the next paths:
- C:WindowsTemp.updatecache (in krbtman.exe, Act64.exe, ie.exe, ieupdate.exe, and windowsdefendersvc.exe)
- C:Windowssystem32.updatecache (in updater.exe, and windowsdefendersvc.exe)
- %LocalAppData%/Temp/.crond (solely in OneDriveLiveUpdater.exe)
The %LocalAppData%/Temp/.crond path is notable, since such a filename (.crond) together with ahead slashes is predicted for Unix-like methods. This means {that a} Linux variant (or macOS, FreeBSD, and many others., although much less seemingly) of MythicRatatoskr can also exist. Furthermore, OneDriveLiveUpdater.exe incorporates an unused configuration path /tmp/.test_config; the filename means that this configuration path might have been used throughout testing and by accident left in a Home windows deployment.
The entire configuration filenames begin with a dot. On Unix-like methods, packages used for itemizing information, akin to ls, sometimes exclude these entries by default, successfully hiding them. This isn’t the case on Home windows, the place these information will not be hidden. This additional suggests the existence of a Linux variant.
The backdoor-specific configuration saved on disk is a JSON file encrypted through AES‑256‑CFB utilizing a hardcoded key embedded within the binary, US3pM9KFxrZBSgc1pGl2wO4Kir1XjZP5Z9kBXBMYd2s=, which is decoded utilizing base64 earlier than getting used. The primary 16 bytes of the file signify the IV.
The configuration file isn’t required for the malware to begin. MythicRatatoskr incorporates an embedded default configuration, which it encrypts and writes to disk throughout initialization. This permits operators to deploy the malware and not using a separate configuration file and replace the configuration later through C&C instructions. Backdoor instructions are described later within the Capabilities part.
Desk 2 presents the embedded MythicRatatoskr configuration widespread for all samples.
Desk 2. Embedded MythicRatatoskr configuration
| Subject identify | Default worth | Description |
| url | https://[201:b479:2771:8d |
C&C server handle within the Yggdrasil community. |
| sleep | 5m | Delays between check-in makes an attempt and beaconing interval. |
| skew | 10 | Unused. Such values are sometimes used to differ sleep time, however MythicRatatoskr doesn’t use it. |
| uuid | 123 |
Distinctive identifier of the operating occasion. It’s a part of every message despatched to the C&C server besides when doing the check-in. The worth 123 is simply an unused placeholder worth that’s changed with the UUID returned by the C&C server through the check-in. A hardcoded UUID d71f1722-cf0b-4e27-9f8e-c95ec9b24a23 is used within the check-in message. |
| psk | US3pM9KFxrZBSgc1pGl2wO |
In all probability supposed to be the AES key for the configuration, because it matches the hardcoded key. Nevertheless, altering this worth has no impact on configuration encryption. |
| depend | 5 | In all probability the utmost variety of instructions the C&C server ought to return in a single HTTP request. |
Though not a part of the above configuration, MythicRatatoskr incorporates the next hardcoded C&C handle for the proxy command: 201:b479:2771:8df4:b5eb:d007:63b0[:]2838:8080. It isn’t potential to change the worth throughout runtime.
Yggdrasil configuration
Initially, when MythicRatatoskr begins, it generates a brand new Yggdrasil configuration, together with a brand new Ed25519 personal key. As a result of the Yggdrasil IPv6 handle is derived from the general public key, the sufferer machine’s Yggdrasil IPv6 handle modifications every time the malware runs.
MythicRatatoskr then makes use of empty NodeInfo knowledge and units the NodeInfoPrivacy flag. In consequence, different nodes within the Yggdrasil community received’t have the ability to get extra details about the node, such because the Yggdrasil model or the working system on which the node is operating.
The backdoor makes use of a publicly obtainable Yggdrasil community to succeed in the C&C server. To hitch the community, it wants to hook up with at the least one of many publicly obtainable friends. All MythicRatatoskr samples comprise the identical embedded record of 32 friends from which three are randomly picked. The peer record is base64 encoded within the binary and was seemingly compiled by the backdoor authors from publicly obtainable sources. We offer the full peer record on the finish of the blogpost.
Capabilities
MythicRatatoskr helps customary backdoor performance, together with command execution, file system navigation, file switch, screenshot seize, and proxying. Desk 3 incorporates all the backdoor instructions; the command IDs are strings which might be hardcoded within the code.
Desk 3. MythicRatatoskr instructions
| Command | Description |
| chtime | Change the sleep configuration worth (see Desk 2). |
| expose | Expose a neighborhood TCP port (i.e., ahead TCP connections from the Yggdrasil community to a neighborhood port). |
| add | Request a file from the C&C server, which is subsequently saved to disk. Particularly, the backdoor sends an HTTP POST request to the C&C server to obtain the file content material. |
| obtain | Ship a neighborhood file to the C&C server. |
| nodeinfo | Return details about the present Yggdrasil node, particularly its IPv6 handle, subnet (we count on this to be 200::/7, which is often used within the Yggdrasil community), and public key. |
| screenshot | Take screenshots of all energetic shows. The pictures will not be saved to disk; they’re included solely within the command outcome. |
| cd | Change the present working listing. |
| ls | Listing the contents of the present working listing. |
| pwd | Get the present working listing. |
| churl | Change the C&C server URL within the configuration. |
| proxy |
Handle a reverse SOCKS5 proxy connection over the Yggdrasil community. This command helps two subcommands: begin and cease. Because the naming implies, it’s used to begin or cease the proxy connection. It connects to the next hardcoded proxy server: It’s the similar handle because the C&C server, however a unique port. As soon as related, MythicRatatoskr sends the string take a look at. Many of the code was copied from current open-source tasks, akin to revsocks, as implied by the presence of debug strings like Accepting stream and Passing off to socks5, and the operate identify connectForSocks. |
| shell | Execute a shell command through cmd.exe. |
Not like the standalone SOCKS5 server described beneath, MythicRatatoskr’s proxy command is used to create a reverse SOCKS5 proxy connection. The standalone instrument creates a neighborhood SOCKS5 server as an alternative.
SOCKS5 server
The SOCKS5 server completely utilized by UAC‑0099 or Sandworm through the August 2025 exercise is an easy instrument written in Go that makes use of go-socks5 for managing proxy connections. The instrument is internally named bindProxy.
As a result of MythicRatatoskr already contains SOCKS5 proxy performance (see Desk 3), it’s unclear why the attackers deployed a separate SOCKS5 server. It’s potential that MythicRatatoskr’s proxy command didn’t work as anticipated, so the operators put in this extra instrument. However, collectively they help each ahead and reverse proxying.
Host-based artifacts
Desk 4 presents SOCKS5 server host-based artifacts that we noticed throughout our evaluation. Once more, word the filename collision for krbtman.exe: it’s MythicRatatoskr on some machines, and the SOCKS5 server on others.
Desk 4. Host-based artifacts related to the SOCKS5 server
Title
Worth
Set up paths
C:Windowssystem32krbtman.exe
%userprofilepercentDownloadskrbtman.exe
%localappdatapercentSMBCachenbtresolver.exe
Capabilities
The instrument makes use of go-socks5 to create a SOCKS5 proxy server that listens on 127.0.0.1, port 33690. The handle is particularly used to permit solely the native machine to entry the service. To make the proxy server reachable from exterior the sufferer’s community, the attackers might have used MythicRatatoskr’s expose command to reveal it via the Yggdrasil community. Alternatively, they might have used one other current tunnel to entry the machine.
Community infrastructure
As acknowledged in its FAQ, Yggdrasil isn’t nameless, so it’s potential to find nodes within the Yggdrasil community. First, we tried to seek out the C&C server 201:b479:2771:8df4:b5eb:d007:63b0[:]2838, which we extracted from the MythicRatatoskr configuration, within the publicly obtainable map of the Yggdrasil community at http://51.15.204.214/ to no avail as a result of the map was final up to date on August 8th, 2024, practically a 12 months earlier than the intrusion befell.
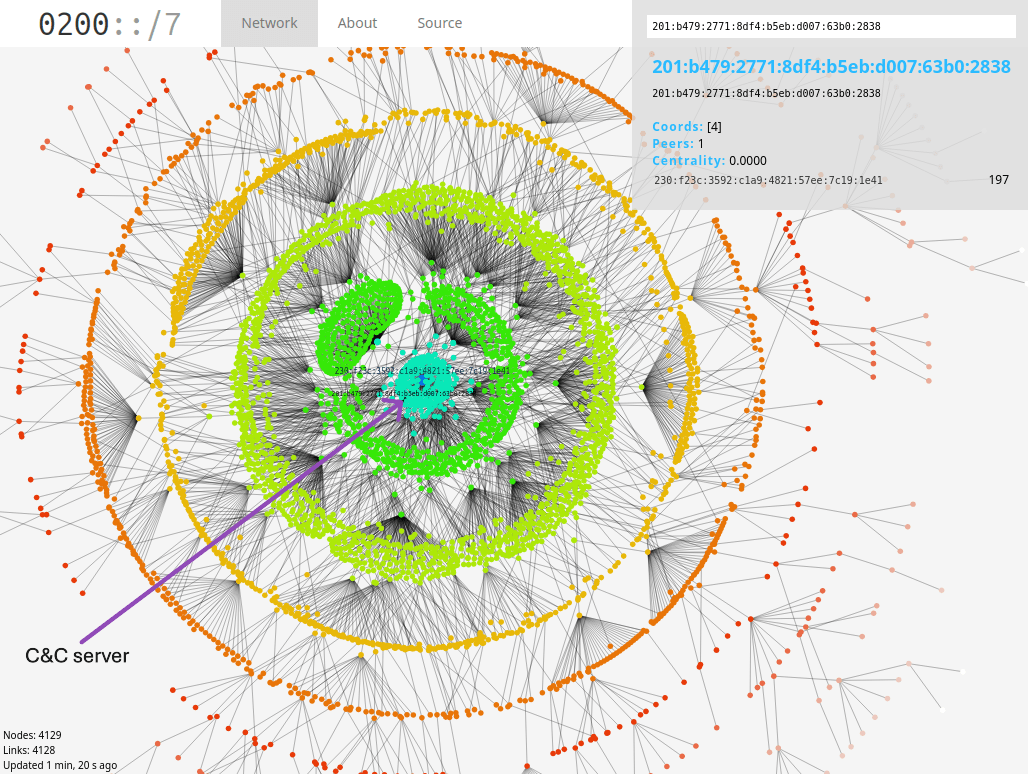
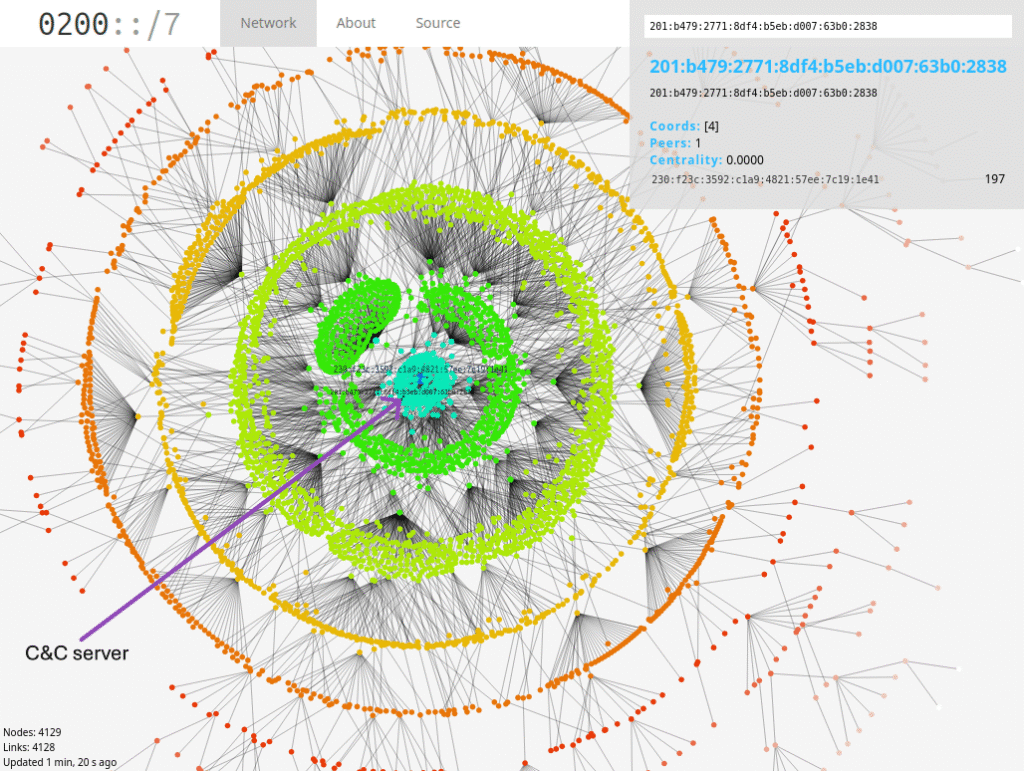
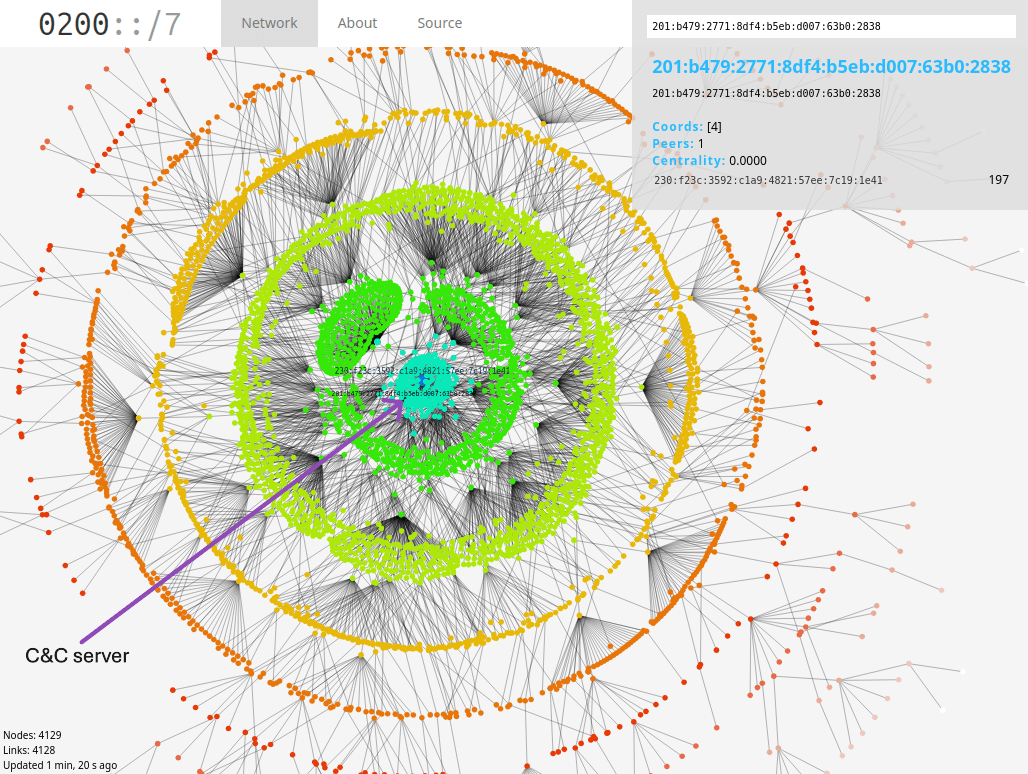
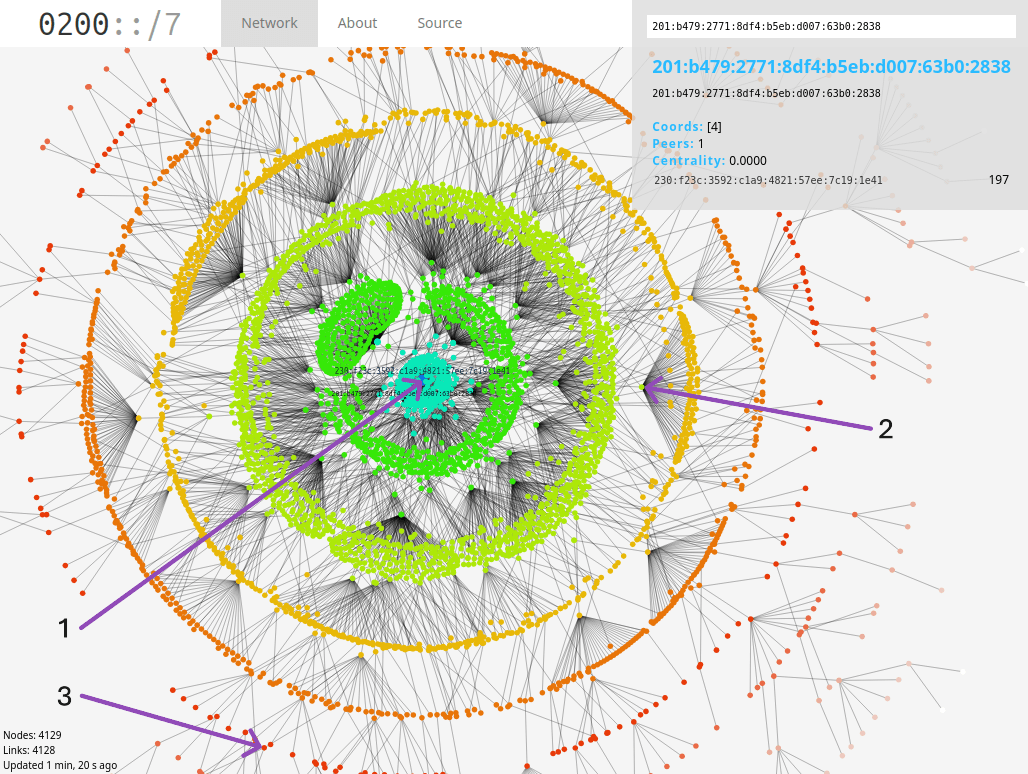
We subsequently generated our personal map of the community’s spanning tree, which does embrace the C&C server, as proven in Determine 1. The C&C server is located close to the middle of the tree, making it simply reachable from different friends. The colours of every node point out how far the node is from the C&C server. For instance, as indicated by the crimson colour, the connection from/to the nodes on the edge will be unreliable. The coordinates (Coords) for the C&C are fairly easy: the server is reachable through the node with ID 4, which is the basis of the spanning tree.
Utilizing Yggdrasil’s command line utility yggdrasilctl, we recognized that the C&C server is configured with three public friends, proven in Determine 2.
The C&C server’s port 443 makes use of TLS certificates which might be rotated repeatedly. This sample is attribute of certificates generated by revsocks, on which the server code might be based mostly.
Conclusion
On this marketing campaign, we noticed cooperation, or at the least operational handoff, between two Russia-aligned menace teams with totally different roles. UAC‑0099 seems to have gained preliminary entry to a Ukrainian logistics firm utilizing its recognized tooling. That entry was later utilized in exercise culminating in a harmful Sandworm operation.
As well as, we recognized a brand new backdoor, MythicRatatoskr, which is attributed to both UAC‑0099 or Sandworm. The C&C server for this backdoor is hosted inside the Yggdrasil mesh community, and using such infrastructure made figuring out the server’s bodily location notably difficult. The backdoor was in all probability used to deploy the SOCKS5 server to route connections via the compromised community.
To our data, that is the primary documented case of Yggdrasil being abused on this approach by a state-aligned menace actor, and it could sign a broader pattern of adversaries adopting experimental peer-to-peer networks to extend the resilience and stealth of their infrastructure.
In the end, Sandworm carried out a data-wiping assault by deploying the SDelete utility through Energetic Listing Group Coverage, a way per earlier Sandworm harmful operations.
For any inquiries about our analysis printed on WeLiveSecurity, please contact us at threatintel@eset.com.ESET Analysis presents personal APT intelligence stories and knowledge feeds. For any inquiries about this service, go to the ESET Menace Intelligence web page.
IoCs
A complete record of indicators of compromise (IoCs) and samples will be present in our GitHub repository.
Recordsdata
| SHA‑1 | Filename | Detection | Description |
| D5F9288DAEBF87AE4579 |
Act64.exe | WinGo/Agent.ZO | MythicRatatoskr backdoor. |
| B69EF0E45B401440C0FD |
ie.exe | WinGo/Agent.ZO | MythicRatatoskr backdoor. |
| 4E3E6577866E4CE2ED73 |
ieupdate.exe | WinGo/Agent.ZO | MythicRatatoskr backdoor. |
| 69969EEB7E0A3D84C4E7 |
ieupdate.exe | WinGo/Agent.ZO | MythicRatatoskr backdoor. |
| 01855153CA7A33AD5FF3 |
krbtman.exe | WinGo/Agent.ZO | MythicRatatoskr backdoor. |
| E29AF83A07FB32EB47C2 |
OneDriveLiveUpdater.exe | WinGo/Agent.ZO | MythicRatatoskr backdoor. |
| 028CA11F3F0D8396043A |
windowsdefender |
WinGo/Agent.ZO | MythicRatatoskr backdoor. |
| 9085896989947C0919A6 |
windowsdefender |
WinGo/Agent.ZO | MythicRatatoskr backdoor. |
| D7E6A5A46C6ED3510997 |
updater.exe | WinGo/Agent.ZO | MythicRatatoskr backdoor. |
| 131A371A1E4EE78EC3B2 |
krbtman.exe | WinGo/Agent.AOK | SOCKS5 server. |
| 09C816697C0C2AFF9B4F |
nbtresolver.exe | WinGo/TrojanProxy |
SOCKS5 server. |
| 8CEB5F8BCDF4995B7164 |
ieupdate.exe | WinGo/Agent.ZO | MythicRatatoskr backdoor. |
Community
| IP | Area | Internet hosting supplier | First seen | Particulars |
| b479:2771:8df4:b5e |
N/A | N/A | 2025‑07‑17 | MythicRatatoskr C&C server inside the Yggdrasil community. |
MITRE ATT&CK strategies
This desk was constructed utilizing model 19 of the MITRE ATT&CK framework.
| Tactic | ID | Title | Description |
| Preliminary Entry | T1566.001 | Phishing: Spearphishing Attachment | UAC‑0099 gained preliminary entry by sending spearphishing emails containing a malicious attachment. |
| Execution | T1059.003 | Command and Scripting Interpreter: Home windows Command Shell | MythicRatatoskr can execute shell instructions utilizing cmd.exe. |
| Persistence | T1543.003 | Create or Modify System Course of: Home windows Service | MythicRatatoskr persists as a Home windows service. |
| Protection Evasion | T1027.013 | Obfuscated Recordsdata or Data: Encrypted/Encoded File | The MythicRatatoskr configuration file is encrypted through AES. |
| T1678 | Delay Execution | Some MythicRatatoskr samples introduce an preliminary delay previous to connecting to the C&C server. | |
| Assortment | T1113 | Display screen Seize | MythicRatatoskr helps a command for taking screenshots. |
| T1005 | Knowledge from Native System | Operators can use MythicRatatoskr’s command ls to seek out information of curiosity previous to exfiltration. | |
| Command and Management | T1090.001 | Proxy: Inside Proxy | The operators deployed the SOCKS5 server to proxy connections within the goal community. |
| T1090.003 | Proxy: Multi-hop Proxy | MythicRatatoskr connects to the C&C server inside the Yggdrasil mesh community. | |
| T1573 | Encrypted Channel | The communication between friends inside the Yggdrasil community is end-to-end protected. | |
| T1105 | Ingress Instrument Switch | The operators in all probability deployed the SOCKS5 server, seemingly through MythicRatatoskr. | |
| T1071.001 | Software Layer Protocol: Net Protocols | MythicRatatoskr communicates with the C&C server inside the Yggdrasil community utilizing HTTPS. | |
| T1132.001 | Knowledge Encoding: Normal Encoding | The information despatched to the C&C server is encoded through base64. | |
| Exfiltration | T1041 | Exfiltration Over C2 Channel | MythicRatatoskr can exfiltrate information to the C&C server. |
| Affect | T1485 | Knowledge Destruction | Sandworm carried out data-wiping assault utilizing SDelete. |
Listing of friends in MythicRatatoskr
tls://37.205.14[.]171:993
tls://109.176.250[.]101:65534
tls://65.21.57[.]122:61995
tls://95.217.35[.]92:1337
tls://51.255.223[.]60:54232
tls://51.15.204[.]214:54321
tls://s2.i2pd[.]xyz:39575
tls://62.210.85[.]80:39575
tls://vpn.ltha[.]de:443?key=0000006149970f245e6cec43664bce203f2514b60a153e194f31e2b229a1339d
tls://mlupo.duckdns[.]org:9001
quic://ip6.fvm.mywire[.]org:443?key=000000000143db657d1d6f80b5066dd109a4cb31f7dc6cb5d56050fffb014217
tls://helium.avevad[.]com:1337
tls://yggdrasil.neilalexander[.]dev:64648?key=ecbbcb3298e7d3b4196103333c3e839cfe47a6ca47602b94a6d596683f6bb358
tls://bode.theender[.]web:42169?key=f91b909f43829f8b20732b3bcf80cbc4bb078dd47b41638379a078e35984c9a4
tls://g.ygg[.]yt:443
tls://b.ygg[.]yt:443
tls://n.ygg[.]yt:443
tls://ygg1.grin[.]hu:42444
tls://[2a03:90c0:85:[:]28a]:443
tls://srl.newsdeef[.]eu:59999
tls://23.137.249[.]65:444
tls://ygg-nl.incognet[.]io:8884
quic://0.ygg.l1qu1d[.]web:11102?key=0000000998b5ff8c0f1115ce9212f772d0427151f50fe858e6de1d22600f1680
tls://london.sabretruth[.]org:18472
tls://yggdrasil.sunsung[.]enjoyable:4443
tls://78.27.153[.]163:33166
tls://193.93.119[.]42:443
tcp://sysop[.]hyperlink:555
tls://sto01.yggdrasil.hosted-by.skhron[.]eu:8884
tls://ygg.ace.ctrl-c.liu[.]se:9999?key=5636b3af4738c3998284c4805d91209cab38921159c66a6f359f3f692af1c908
quic://spain.magicum[.]web:36900
tcp://y.zbin[.]eu:7743