
An unknown risk actor has contaminated 953 on-line shops, most of them working Magento, as a part of a long-running marketing campaign lively since July 2025.
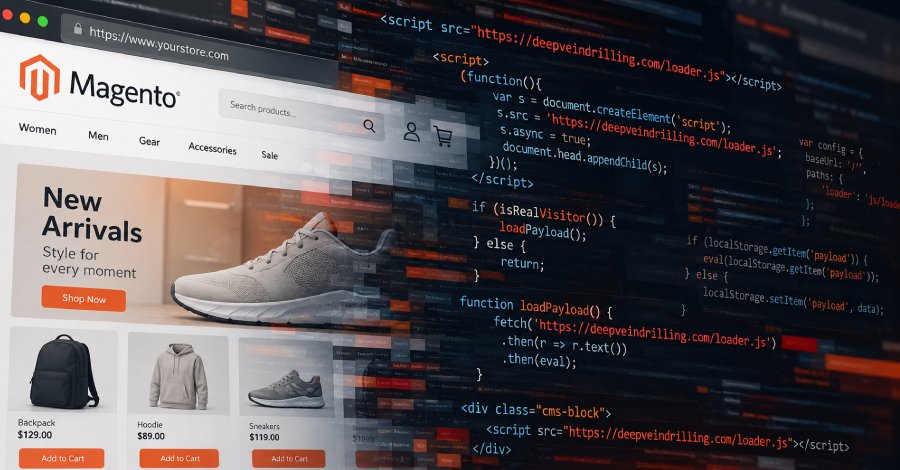
Based on Dutch e-commerce safety firm Sansec, the exercise is designed so as to add a small piece of code to the shop’s pages that, when visited by unsuspecting customers, serves malicious JavaScript loader code by Magento CMS blocks.
“If you go to, that code makes your browser ask the group’s server what to do subsequent,” Sansec mentioned. “The server first checks whether or not you’re a actual shopper or a safety scanner, so scanners get nothing.”
At least 5 distinct domains have been noticed over time in reference to the marketing campaign –
- manulfie[.]click on, first seen in July 2025
- neswnsssn[.]click on, first seen in December 2025
- lanhd6549tdhse[.]high, first seen in March 2026
- additionalver[.]com, first seen in June 2026
- deepveindrilling[.]com, first seen in October 2026
Sansec mentioned it discovered deepveindrilling[.]com within the CMS blocks of 83 on-line shops because the area was registered on October 6, 2026.
The newest JavaScript loader area is hosted behind Cloudflare and solely responds to script requests from actual guests of contaminated shops. The loader is staged inside Magento’s cms_block database desk, which is used to render static content material into storefront pages.
The final word goal of the assault is to launch the attack-controlled code when the CMS block is rendered after a consumer opens the compromised web site.
Whereas Sansec doesn’t disclose whether or not the risk actor modifies an present CMS block (resembling header, footer, or promotional banner) or creates a brand new block, the attacker can undertake both of the approaches to run the loader.
Two completely different variations of the loader have been noticed. In a single model, the exterior JavaScript loaded from the attacker’s area shops the payload within the browser’s localStorage. This causes the stashed code to be run once more on subsequent visits, even when the exterior area turns into unavailable.
The second model expands on this habits by incorporating browser fingerprinting checks to filter out bots and safety scanners, whereas making certain that solely actual consumers are uncovered to the malicious code. The precise nature of the ultimate payload stays unknown.
Early iterations of the marketing campaign have additionally been noticed utilizing Keitaro, an promoting tracker and analytics platform, as a site visitors distribution system (TDS), to route guests to completely different responses – i.e., return a payload, a redirect or nothing – primarily based on their traits.
Sansec mentioned requesting the additionalver[.]com script as a Home windows desktop customer returned as response “QWE=123;,” which does nothing other than setting a cookie that marks the customer for twenty-four hours. The deepveindrilling[.]com area, however, drops the Keitaro part and integrates the bot-filtering logic into the loader itself.
As for the preliminary entry vector, 471 Magento shops are estimated to have been injected with the loader by the PolyShell (aka CVE-2026-48356) vulnerability. One other 102 shops noticed information uploaded by the PolyShell or SessionReaper (aka CVE-2025-54236) vulnerabilities.
“One retailer on Magento 2.4.7-p1 had PolyShell webshells disguised as PNG pictures in pub/media/custom_options/quote/, subsequent to the additionalver.com loader in a CMS block,” Sansec mentioned. “The block switched to deepveindrilling[.]com on October 7. The shop nonetheless lacks APSB26-73, Adobe’s PolyShell repair for supported launch traces.”
In one other case, an e-commerce retailer working Magento 2.4.7-p10 with no lacking core patches was compromised so as to add a rogue administrator account after which use it to inject the code.
Web site house owners are suggested to audit their websites for suspicious accounts and surprising CMS blocks within the cms_block and cms_page tables. It is also suggested to maintain the websites up-to-date and implement sturdy passwords.
The disclosure comes in opposition to the backdrop of PHP2Shell, a set of two crucial vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619) which have witnessed widespread exploitation makes an attempt following their disclosure final week.
Nonetheless, Perplexity researcher Adel Karimi has recorded what seems to be the primary in-the-wild profitable exploitation of the vulnerabilities to run shell instructions on honeypot servers. These instructions have been noticed utilizing wget, curl, or PHP CLI to fetch extra payloads from a distant server (“162.35.99[.]94:80”).No downloaded second-stage artifacts have been noticed up to now.