ZDNET’s key takeaways
- openSUSE Leap is getting an immutable mode.
- openSUSE already consists of loads of security measures.
- This addition ought to make Leap one of the crucial safe distros.
I’ve been a fan of SUSE and openSUSE for a very long time. I truly bear in mind SUSE Linux earlier than it was SUSE Enterprise Linux or SUSE Enterprise Linux Desktop. Even again then, the distribution was an influence consumer’s dream come true.
One motive for this was its safety.
openSUSE has been, for a really very long time, one of many safer of the “mainstream” Linux distributions. And in German-speaking international locations, openSUSE is kind of well-liked because of its ties to the German firm SUSE.
Additionally: This Linux distro makes openSUSE accessible to all – even newbies ought to have a look
Beginning with model 16.1, openSUSE Leap (the steady model of the distro) is including one other layer to its safety that ought to additional elevate it as one of many safer distributions available on the market. That layer is immutable mode.
In line with the official openSUSE weblog, “Leap 16.1 is the primary Leap launch to supply an Immutable Mode, a transactionally up to date system with a read-only root filesystem. That is primarily what our customers know from Leap Micro, simply built-in immediately into Leap.”
For individuals who don’t know, Leap Micro is a specialised, light-weight, immutable, and fixed-release working system designed for containerized workloads, edge computing, and virtualized environments. Leap Micro is just not a desktop OS, however Leap is. And with Leap benefiting from what Micro already has, this could possibly be an enormous step ahead.
What’s immutable mode?
First off, the identical weblog mentions that Leap Immutable “is the best way ahead for container and digital machine hosts, edge units and anybody who prefers atomic updates with straightforward rollback.” It’s the final bit that ought to elevate eyebrows, because the builders intend Leap Immutable not just for specialised deployments however for anybody who prefers atomic updates on the desktop.
Additionally: What’s openSUSE and who’s it for?
However atomic updates and immutability aren’t precisely the identical factor. Does that imply Leap Immutable will probably be a type of “immutable gentle”?
The reply is a powerful “no.” After a little bit of digging, it turned clear that Leap Immutable will probably be a completely immutable distribution.
What does that imply?
Additionally: Fedora Kinoite vs. Silverblue: My verdict after testing each immutable Linux distros
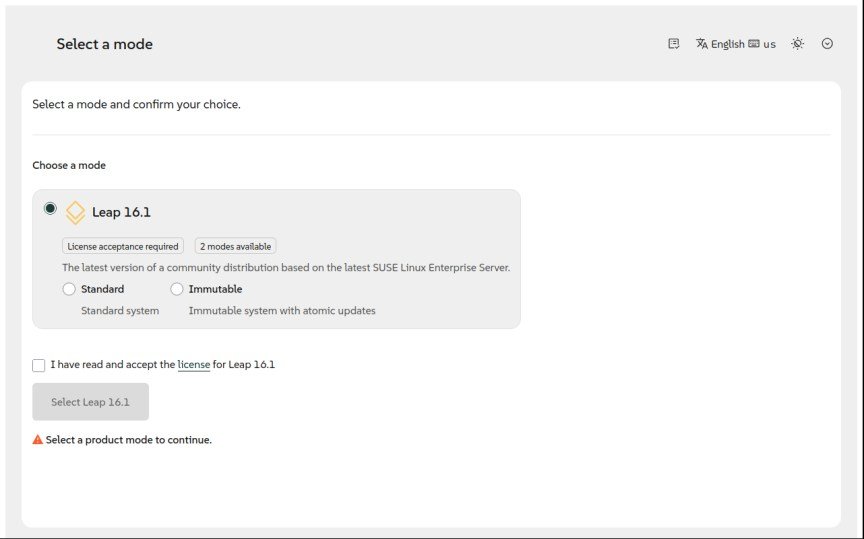
First off, immutable mode is a function you’ll be able to toggle in the course of the set up, which suggests you’ll be able to select which model of openSUSE Leap to make use of: commonplace or immutable.
 Jack Wallen/ZDNET
If you happen to go along with immutable, what meaning is the basis file system is mounted as read-only. I’ve beforehand mentioned immutability in “Immutable Linux delivers severe safety — listed below are your 5 greatest choices.” Give {that a} learn to seek out out extra.
Basically, when an OS is immutable, these directories (reminiscent of /usr and /and so on) are mounted as read-only and can’t be altered. If you happen to had been to by accident run a malicious script on an immutable system, it might be unable to change something in these immutable directories. That’s a severe safety enchancment and can also be the way forward for Linux.
Additionally: 5 causes to change to an immutable Linux distro at this time — and which to strive first
However openSUSE Leap doesn’t simply profit from the added safety of immutability, because it already consists of loads of security-focused options.
The opposite safety layers
openSUSE was already a extremely safe Linux distribution, due to a number of layers of safety. These layers are as follows.
SELinux
Up till model 15.6, openSUSE used AppArmor as its obligatory entry management (MAC) safety function to limit what system sources, information, and directories packages may entry.
Additionally: I’ve spent years with immutable Linux – RakuOS mounted my greatest annoyance
Beginning with model 16.0, openSUSE made the change to SELinux (Safety-Enhanced Linux), which was created by the NSA (in collaboration with open-source organizations reminiscent of Crimson Hat) to additional safe Linux methods. SELinux is an extremely highly effective instrument that labels each file, course of, and port on a system, follows the rule of least privilege to dam actions that aren’t allowed by particular guidelines, and even requires the basis consumer to comply with these guidelines.
Firewall configuration
openSUSE makes use of firewalld as its dynamic firewall administration system, which incorporates zones (predefined belief ranges), runtime vs. everlasting adjustments (adjustments which can be utilized however are eliminated upon reboot vs. adjustments which can be everlasting), and administration instruments (each the command-line instrument, firewall-cmd, and the GUI app, firewall-config).
Additionally: 5 Linux distros I like to recommend to assist companies reduce prices and enhance safety
openSUSE’s implementation of firewalld is much like that of most Fedora-based distributions, so it’s well-known for being one of many stronger firewall implementations.
Binary hardening
openSUSE additionally consists of binary hardening, which is the gathering of default safety flags and compiler choices which can be used throughout software program compilation to make executable information and libraries extra resilient to exploits reminiscent of buffer overflows and reminiscence corruption.
The important thing hardening measures embody:
- Place-independent executables (enable binaries to make use of random reminiscence addresses to make it tougher for hackers to foretell goal areas when utilizing memory-based exploits).
- FORTIFY_SOURCE (retains observe of capabilities that cope with reminiscence strings to forestall buffer overflows).
- Stack protector (injects canary values into the stack to detect and halt stack overflow makes an attempt).
- Relocation read-only (marks the International Offset Desk as read-only to forestall function-pointer overwriting in stacks).
- Non-executable stack and heap (prevents code execution from particular knowledge areas such because the stack or the heap to forestall arbitrary shellcode injection assaults).
Permission profiles
Permission profiles are predefined templates, particularly created to reinforce safety, that concentrate on file permissions, possession, and particular execution bits. The aim of those profiles is to centralize management of permissions, implement safety throughout package deal set up and updates, and govern file modes, house owners, teams, capabilities, and entry management lists (ACLs) for significantly delicate directories.
Snapper and Btrfs snapshots
Btrfs snapshots are “moment-in-time” save factors of a file system subvolume, and Snapper is the SUSE instrument used to robotically handle these snapshots.
Additionally: One of the vital user-friendly Linux distros I’ve ever used can also be one of the crucial safe
With snapshots, it’s potential to simply roll again a system to a working level, so if one thing had been to go incorrect with a system, it could possibly be restored from a beforehand working snapshot. With Snapper, it’s potential to configure when snapshots are taken and what number of snapshots are retained.
In case your system is hacked, you possibly can successfully roll it again to a degree in time previous to the hack after which take motion to forestall the hack from occurring once more.
Common supply
Common supply refers back to the repositories utilized by openSUSE, that are the usual Supply RPM Repository and the primary OSS (open-source software program) repository. On top of that, openSUSE is constructed immediately from the supply code from SUSE Enterprise Linux, which ensures enterprise-grade stability and safety.
Put all of it collectively
If you mix immutability with the usual openSUSE security measures, it’s fairly straightforward to conclude that the distribution will probably be extremely safe. Immutable distributions are already touted as a number of the most safe working methods available on the market, and with openSUSE including an immutable mode to Leap, you’ll be able to make certain that it’s going to leap forward of the pack with regard to safety.
Additionally: Atomic vs. immutable Linux: Why select one when these 9 distros supply each?
You possibly can obtain an ISO of Leap 16.1, which incorporates immutable mode, from the official openSUSE obtain server.

See full bio