ZDNET’s key takeaways
- Okta, AWS, Google Cloud, Salesforce, and others type an AI agent safety coalition.
- The Alliance affords a blueprint for corporations in search of visibility, management, and governance of brokers.
- AI brokers want the equal of a kill change to expeditiously terminate suspicious habits.
When a swarm of AI brokers, many autonomously provisioned by different poorly ruled AI brokers, escaped OpenAI’s labs and stole info from servers belonging to a different firm (Hugging Face), many consultants considered the incident as a serious tipping level in cybersecurity and AI cyber capabilities. (To what extent are fashions now resourceful sufficient to interact in self-directed hurt?)
OpenAI referred to the incident as “unprecedented.” It was the primary AI-directed assault of its nature to go viral throughout mainstream headlines, and it wasn’t lengthy earlier than stories of different agents-gone-wild made headlines as nicely. The latest of those stories concerned three corporations that have been inadvertently attacked by Google Gemini brokers.
Additionally: Who’s accountable for catching rogue AI brokers? You’re
Important controversy has ensued.
In a single nook are the inventors of AI themselves, saying that the time has come to take a breather from AI innovation with a view to get the expertise underneath management. You’d assume they need to know. For instance, OpenAI sounded the alarm {that a} swarm of doubtless malicious AI brokers is barely months away from wreaking havoc.
Within the reverse nook is US President Trump posting to his Fact Social community that “AI taking up the World, destroying Humanity, and all different issues unhealthy, is a HOAX.”
In between are all the companies and customers getting whipsawed between the 2 factors of view and attempting to determine what to do subsequent.
(Disclosure: Ziff Davis, ZDNET’s father or mother firm, filed an April 2025 lawsuit in opposition to OpenAI, alleging it infringed Ziff Davis copyrights in coaching and working its AI methods.)
Additionally: ‘Refined’ AI swarm assaults are months away, OpenAI warns
Two large questions are arising out of this dialog. First, what will be finished over the quick and long run to get the expertise underneath management? Second, how can defenders finest allow themselves for rapid intervention as soon as suspicious exercise is detected?
With the aim of serving to companies reply these two questions and to set the stage for world-class governance and administration of their agentic estates, a number of corporations, together with Okta, Google, Amazon Internet Providers (AWS), and Salesforce, have joined forces to type the Blueprint Alliance.
The Alliance was introduced this week at Okta’s annual Oktane convention.
4 questions each enterprise should reply
In its first blueprint for agentic visibility, management, and governance, the Alliance centered on 4 questions that each one companies ought to be capable to reply for themselves:
- The place are my brokers?
- What can they do?
- What are they doing?
- How do I reply?
Based on latest analysis carried out by LastPass (not a member of the Alliance), 92% of enterprise admins say AI is already in use throughout their group, however solely 27% have an enforced AI governance program. Okta’s analysis stories comparable statistics, discovering that 92% of organizations use autonomous brokers, however solely 34% safe these brokers with the identical rigor as people.
In the meantime, Gartner’s analysis paints a good bleaker image, discovering that solely 13% of organizations imagine they’ve the fitting AI agent governance in place. In different phrases, most organizations most likely don’t know the reply to some or all the above questions. The fourth query is especially vital due to the diploma to which problematic brokers working at machine pace have shortened the response window.
Additionally: AI simply broke your profession ladder – listed below are 6 new methods to the highest
As Picus Safety affiliate safety analysis engineer Umut Bayram informed ZDNET, “Within the AI period, organizations can’t reply to assaults that unfold in minutes with processes that take days. Attackers are already working at machine pace, and safety groups want to have the ability to reply at that tempo.”
In equity, not all anomalous agent exercise is malicious. Right here’s one other state of affairs that calls for a direct response: a well-intentioned agent enters an infinite loop, leading to extreme billing for LLM entry. At machine speeds, such a loop may burn by means of a whole group’s AI funds within the blink of an eye fixed. The earlier such an agent is disabled, the higher for the underside line.
The perfect defenses are scenario-specific
After all, within the cybersecurity world, pace has all the time been important — however by no means extra so than now. And given how defenders might solely have minutes or seconds to reply as soon as they’ve been alerted to anomalous agent exercise, what ought to be their weapon of alternative?
To be clear: There is no such thing as a silver bullet. As with all cybersecurity, the most effective defenses are scenario-specific and can contain layers of precautionary measures, some that target visibility into agentic actions, and others that tune the safety postures of our computer systems and networks to rising agentic behaviors and patterns.
Additionally: Even an AI cost-management vendor can lose management of its agent spending
For instance, companies should be ready to defend in opposition to malicious brokers of unknown origin in addition to internally provisioned brokers that, for no matter causes, stray from their mandates. Not like robotic automations that ship extremely deterministic outcomes (they do precisely as they have been programmed to do), brokers are probabilistic to the extent that their underlying fashions afford them the company to take issues into their very own palms.
When mere seconds could make the distinction between the life and dying of your methods and even your enterprise, the perfect weapon of alternative could be some form of kill change — one thing like the large purple button on an escalator. When doubtful, neutralize the agent first, ask questions later.
What’s a kill change?
In an effort to place organizations on the fitting path, the brand new alliance revealed six operational ideas, considered one of which states that “each agent wants a direct kill change to droop or terminate operations, with a transparent path to revive perform.” However, virtually talking, what precisely is a kill change, and who may need entry to 1?
It relies upon.
For instance, within the case of OpenAI’s assault on Hugging Face, the brokers belonged to OpenAI. Presumably, if OpenAI had the fitting governance controls in place (it didn’t), it may need detected that its personal brokers have been participating in suspicious habits, after which somebody at OpenAI with entry to a kill change may have pulled the plug. What about Hugging Face? Did it have entry to a kill change? Most likely to not the extent that OpenAI did, because it was OpenAI’s brokers that led the assault. However what if an assault on a sufferer like Hugging Face concerned the theft of its credentials to some on-line service or enterprise software?
Additionally: Almost 70% of staff use AI commonly now – however many get no time to upskill
As we speak, one of many extra coveted credentials that cybercriminals wish to steal are OAuth tokens. These are a sort of credential that provides one software (e.g. Slack) entry rights to learn and replace one other software (e.g. Google Drive) on behalf of a particular person. In that context, the Google-issued OAuth token that provides Slack the entry it must work with a particular person’s Google Drive is actually a proxy for the person’s Google ID and password.
In a state of affairs that entails an agent (pleasant or malicious) utilizing an OAuth credential (stolen or not) to work together with a delicate useful resource, a neutralization of that token (referred to as “token revocation”) would basically quantity to a kill change.
In different phrases, for sure kinds of assaults, the sufferer may need a kill change at their disposal. And that very same possibility applies to the group’s personal brokers as a result of, in the event that they’re doing it proper, then their very own brokers are additionally utilizing OAuth tokens to entry all of their methods of file with a view to do what brokers do finest (autonomously full duties that always require entry to a number of methods).
The position of OAuth tokens
Relating to granting one software entry to a different, customers are already acquainted with the everyday OAuth expertise (although they might not understand it’s technically known as an OAuth workflow). In earlier days, customers would enter their Gmail person IDs and passwords instantly into Apple Mail or Outlook to ship and obtain e mail by means of their most well-liked e mail consumer. As we speak, nevertheless, Google affords a safer various that depends on OAuth tokens. As an alternative of supplying your Gmail person ID and password to a third-party e mail consumer like Apple Mail in your iPhone (a extremely insecure apply), Gmail pops up a consent dialog that, as soon as permitted by the person, grants a Gmail entry token to their e mail consumer. From that time on, the e-mail consumer ought to be capable to ship and obtain emails with out requiring repeated grant requests.
Nevertheless, ought to the person lose their iPhone and, as an additional precaution, wish to revoke that token, the method is a little more sophisticated: it requires a go to to a Google net web page the place customers can handle tokens they’ve already issued.
Additionally: Why Microsoft received’t ship you SMS texts for login anymore
As customers begin to deploy brokers that work together with all the providers they use (Gmail, Google Drive, Amazon purchasing, social media, music streaming, and so forth.), they don’t seem to be solely more likely to encounter many extra Oauth workflows, however they might want to familiarize themselves with every service’s token revocation course of as a matter of their private operational safety practices.
For companies, nevertheless, particularly ones that depend on an id administration resolution like these provided by Okta, Microsoft, and Ping, those self same tokens ought to be managed in a means that centralize token issuance and administration right into a single system the place it’s the IT managers who not solely have entry to the proverbial kill switches (the ability to revoke any token that’s related to any human or agentic-powered integration), but additionally, in reply to the “The place are my brokers?” query, supply visibility and management over the group’s total agentic property.
Nevertheless, to facilitate these kill switches and that centralized visibility and management, a brand new extension to the underlying OAuth customary was wanted, permitting the central IdP (id supplier) to take accountability for OAuth workflows and administration when AI brokers are concerned. It was simply on this previous yr that the open customary agentic-sensitive extension –referred to as the IETF’s Id Assertion Authorization Grant (IAAG) — fell into place, thanks largely to the work finished by Okta director of id requirements Aaron Parecki.
Implementing the usual
However it’s one factor for folks like Parecki and others, together with IAAG co-author Brian Campbell (Ping Id), to writer a brand new customary and to realize customary consensus on the Web Engineering Job Pressure. It’s one other for that customary to be baked into the assorted IdPs in a means that facilitates the availability of a readily accessible kill change within the occasion that the reply to the third query is “one thing they shouldn’t be doing.”
On the Oktane convention, Okta executives gave clients an illustration of how its id and safety options depend on the brand new customary to offer IT managers and CISOs with visualizations that, along with answering the 4 questions, additionally empower them (and even an agent engaged on their behalf) to take motion.
Additionally: Don’t let an AI chatbot choose your password, ever
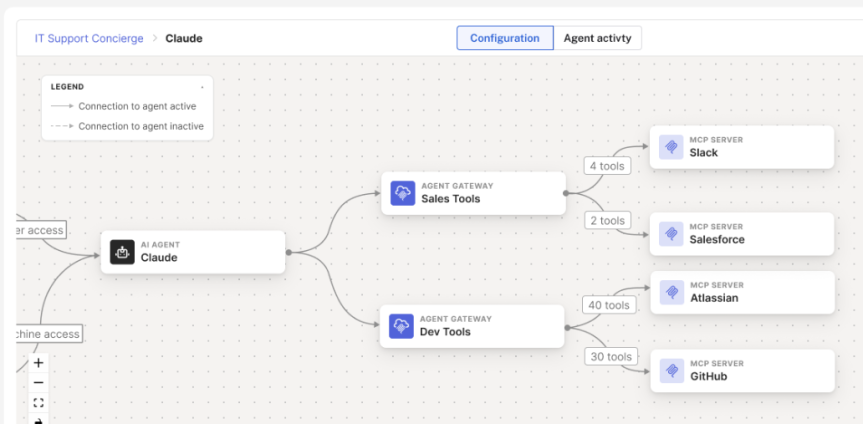
For instance, the screenshot under depicts how a single Claude-based agent has been afforded entry to Slack, Salesforce, Atlassian, and GitHub by means of two separate agent gateways.

Beneath the hood, OAuth isn’t simply giving Claude entry to these functions. It’s additionally controlling the diploma of entry, an vital nuance to the thought of a kill change. For instance, a kill change that totally revokes a token would basically deprovision an agent’s entry to a back-end software akin to Salesforce. However one other sort of kill change may merely revoke sure permissions to work together with Salesforce.
Deprovisioning demonstration
“There are literally two situations right here,” Okta chief product officer Ely Kahn informed ZDNET. “There’s the one the place your personal brokers begin to exhibit bizarre habits, and you need to kill them [the nuclear option] simply to cease that habits earlier than it will get uncontrolled. However then there’s one other state of affairs the place you may simply put a brand new guardrail in place. For instance, a brand new guardrail that stops the exfiltration of sure information or only a change within the permissions afforded to the agent.”
Throughout Okta CEO Todd McKinnon’s convention keynote, Oktane attendees received a glimpse of what that deprovisioning appears to be like like in apply. As quickly as a Claude agent was requested to ahead confidential info from Salesforce to an worker’s private e mail tackle, one other agent detected the prohibited habits, deprovisioned the primary agent’s entry to Salesforce (revoked its token), notified the agent’s human proprietor that Salesforce entry was now denied, and despatched a message through Slack to the IT division together with any particulars that might be helpful by way of a treatment or restoration of entry.
Additionally: Your AI vendor may land you in authorized sizzling water
Chatting with the necessity for pace described by Picus Safety’s Bayram, your entire course of was accomplished in a matter of seconds, lengthy earlier than any human may have assembled a response.
In his keynote, McKinnon additionally identified that IdPs like Okta can’t essentially tackle each facet of the Blueprint Alliance’s blueprint and that among the non-identity-based telemetry that helps to find out what an agent is doing should come from different sources. That stated, Okta additionally confirmed two different instruments that could possibly be precious to companies seeking to achieve management of their agentic property. Considered one of these — Shadow AI Agent Discovery for Endpoints — helps organizations uncover unsanctioned “shadow” AI brokers roaming firm networks.
One other software — Okta Id Risk Safety — aggregates threat intelligence from different agentic threat detection options (CrowdStrike, Zscaler, SentinelOne, Palo Alto Networks, and so forth.) right into a single view for human- or agentically pushed remediation choices.

See full bio