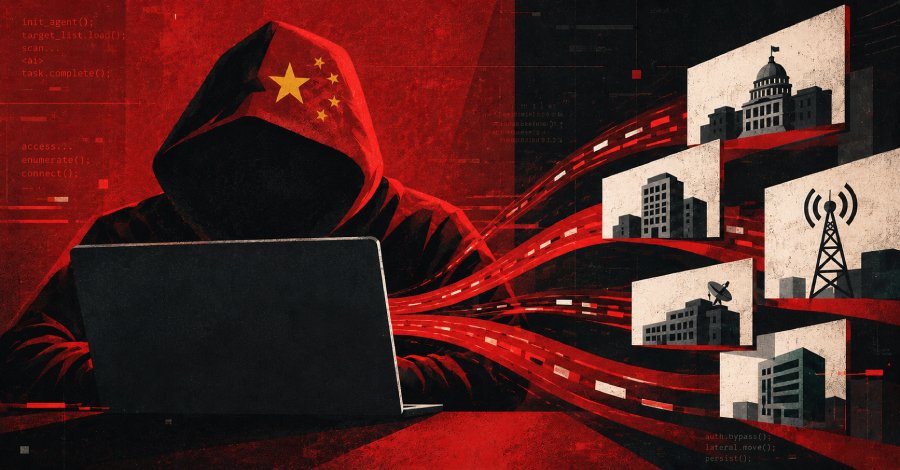

Chinese language state-sponsored menace actors have been noticed utilizing a Go-based synthetic intelligence (AI)-powered penetration testing framework known as ARTEX in assaults geared toward high-value targets concurrently.
The exercise has been attributed by CrowdStrike to a China-based “focused intrusion adversary” it tracks underneath the moniker Vapor Panda (beforehand VexatiousTemper). First recognized in February 2021, the hacking group overlaps with a menace cluster detailed by Development Micro as Earth Estries.
“Agentic tooling like ARTEX allows this scale of growth at pace, permitting a small staff to pursue a wider goal set than guide operations would help, moderately than a wholesale shift away from the adversary’s established access-development mission,” CrowdStrike mentioned in a Thursday evaluation.
Beginning October 17, 2026, Vapor Panda is claimed to have used the AI device in opposition to greater than 200 distinct organizations internationally, together with international ministries in Latin America, Europe, Asia, and the Center East; semiconductor, protection, and assume tank organizations within the U.S.; and telecommunications suppliers in a number of areas.
A number of the notable targets listed by CrowdStrike are listed beneath –
- Overseas ministries of two Latin America-based international locations, Central America, and Asia
- A Center East-based inside ministry
- A European nation’s international ministry, presidency, and prime minister’s workplace, together with protection, justice, finance, and intelligence entities
- 19 U.S.-based organizations within the pharmaceutical, semiconductor, protection, nuclear, and monetary sectors
- Telecommunications suppliers within the U.S., Belgium, and the Philippines
Put up-exploitation exercise has been confirmed at 9 organizations, permitting the attacker to deploy BLOODALCHEMY, a by-product of ShadowPad, adopted by credential spraying, community scanning, and reconnaissance.
Vapor Panda can be mentioned to have carried out password-spraying and credential-scanning exercise in opposition to at the least 12 further organizations, together with U.S.-based assume tanks and authorities entities in Europe.
Central to the operation is the usage of ARTEX with DeepSeek and an as-yet-unknown, subscription-based business massive language mannequin (LLM) to conduct the intrusions at scale, leveraging a military of planner and employee brokers that coordinate with one another in pursuit of a standard purpose to maneuver from preliminary entry to host reconnaissance and lateral motion.
A human operator within the loop oversees the operation, directing the brokers to put in writing net shells, extract area administrator passwords, and enumerate endpoint sensor protection.
“In a single intrusion, Vapor Panda’s planning brokers consumed on the order of 1.4 billion enter tokens, indicating the dimensions of the automated exercise and implying far greater consumption throughout the operation as an entire,” CrowdStrike mentioned.
Not like some campaigns that used to help with particular person digital break-ins, the usage of ARTEX is at a a lot greater stage to run a number of engagements concurrently, with the human operator solely stepping in to steer the brokers to perform their goal, whereas taking steps to bypass endpoint defenses.
Evaluation of the recovered transcripts highlights the usage of ARTEX together with tried-and-tested approaches –
- Chaining an unsigned Safety Assertion Markup Language (SAML) assertion and an XML exterior entity (XXE) flaw to question the cloud Occasion Metadata Service. That is adopted by acquiring a job that may subject administration instructions to hundreds of situations earlier than escalating entry to get well an enterprise administrator account.
- Deploying net shells, abusing an unauthenticated orchestration service to acquire root entry in a manufacturing container surroundings, studying Native Administrator Password Answer (LAPS) passwords, and leveraging resource-based constrained delegation to impersonate a privileged account.
- Supplying the agent with a set of authentication keys that had not been rotated since 2022, which then makes use of these keys to forge an administrator token and skim mailboxes. Within the subsequent part, the agent makes use of VPN configurations recovered from a consumer’s despatched mail, together with a VPN consumer key originating from a purported Could 2024 e mail leak, to succeed in the inner community.
“Throughout these engagements, the brokers pursued a number of assault paths in parallel, spanning net functions, cloud companies, container environments, Energetic Listing, and mail and VPN infrastructure,” CrowdStrike defined. “They shifted to different approaches when a path failed. This breadth probably allows a single operator to use a wider vary of strategies in opposition to extra targets without delay than could be possible via guide operations.”

The event comes as ARTEX has witnessed broad adoption amongst menace actors in a brief span of time, prompting its developer Li Puhua (“Autumn-27”) to take it closed supply.
“It orchestrates a number of LLM backends to autonomously carry out reconnaissance, vulnerability identification, and exploitation, considerably reducing the technical barrier for conducting complicated intrusion campaigns,” Zscaler ThreatLabz mentioned in a report printed earlier this month.
Considered one of Many Panda Risk Clusters
The disclosure additionally coincides with the emergence of 4 beforehand undocumented China-linked state-sponsored menace teams referred to as Hole Panda, Overcast Panda, Titan Panda, and Veiled Panda, which have focused a broad vary of sectors internationally for intelligence gathering and mental property theft.
Overcast Panda, described as “one of the vital operationally subtle and protracted threats dealing with organizations with personnel touring to China,” has been linked to shut entry intrusions wherein the adversary has deployed their proprietary FlowCloud backdoor on victims’ gadgets by way of direct bodily entry when these targets have been within the nation.
FlowCloud is launched via DLL sideloading, with its elements designed to fly underneath the radar and resist forensic evaluation. Command-and-control (C2) is achieved via reliable cloud infrastructure in an try to additional conceal their presence.
“FlowCloud itself is a complicated, purpose-built device uniquely related to Overcast Panda,” CrowdStrike mentioned. “As soon as deployed, FlowCloud supplies the adversary with persistent, covert distant entry to the goal system, enabling keylogging, display seize, file assortment, and credential harvesting.”
Titan Panda, alternatively, has been noticed concentrating on authorized billing software program by exploiting a hard-coded Web Info Providers (IIS) machine key vulnerability in Intapp Time Server to realize distant code execution throughout regulation companies.
The assaults, first detected in April 2026, led to the deployment of an in-memory framework known as IceGiant to hold out reconnaissance, persistence, lateral motion, and information exfiltration. The menace actor is assessed to be operational since at the least 2021, compromising a number of authorized organizations in North America for over two years.
“How Titan Panda obtained the default machine keys is unknown, although IIS compromise of a authorized entity working Intapp Time Server might have uncovered the hardcoded keys within the software’s configuration file, enabling ViewState deserialization assaults in opposition to any group working default installations,” CrowdStrike mentioned.