Cybersecurity for smaller companies typically suffers by being both underpowered or too complicated. This rigidity may be difficult to resolve for small IT groups which will lack an in-house cyber knowledgeable. Understanding the issue shouldn’t be the identical as understanding the place the answer lies.
Efficient SMB safety calls for that distributors lead their prospects by a transparent onboarding course of – and provide sensible and clear steering throughout incident response engagements.
With out trusted partnerships like this, SMBs might battle to optimize the way in which they use safety services and products. They might discover it troublesome to elucidate incidents to insurers and regulators. They usually might fail to be taught from menace occasions in a means that may assist to construct long-term resilience.
Complexity is all over the place
These challenges are essential not only for SMBs themselves to beat. As they make up over 99% of all non-public sector corporations in Europe and North America, small and mid-sized companies are the spine of most economies and comprise the provision chain of bigger organizations. That places them straight within the firing line of menace actors in search of weaknesses to probe, en route to consumer knowledge or community entry. Manufacturing outages at important factors in provide chains can have probably catastrophic knock-on results.
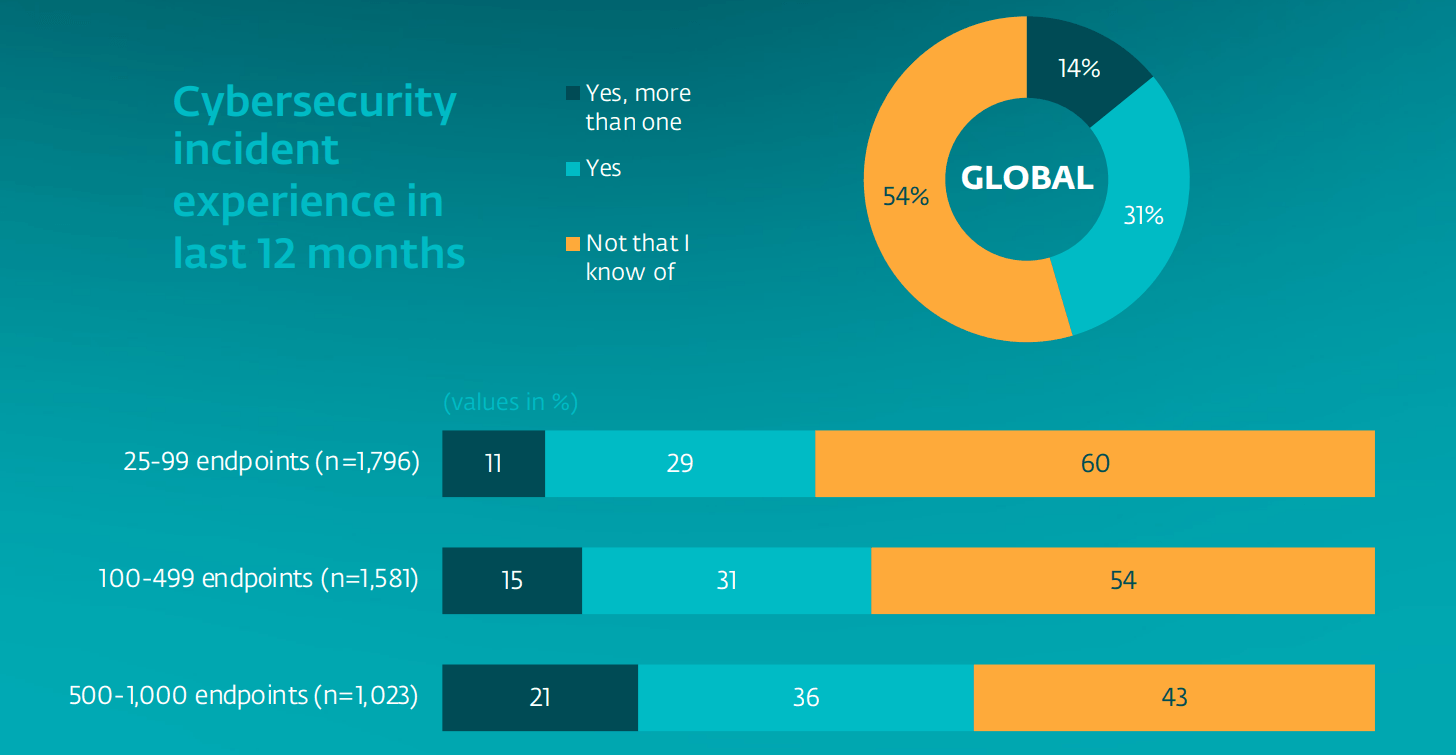
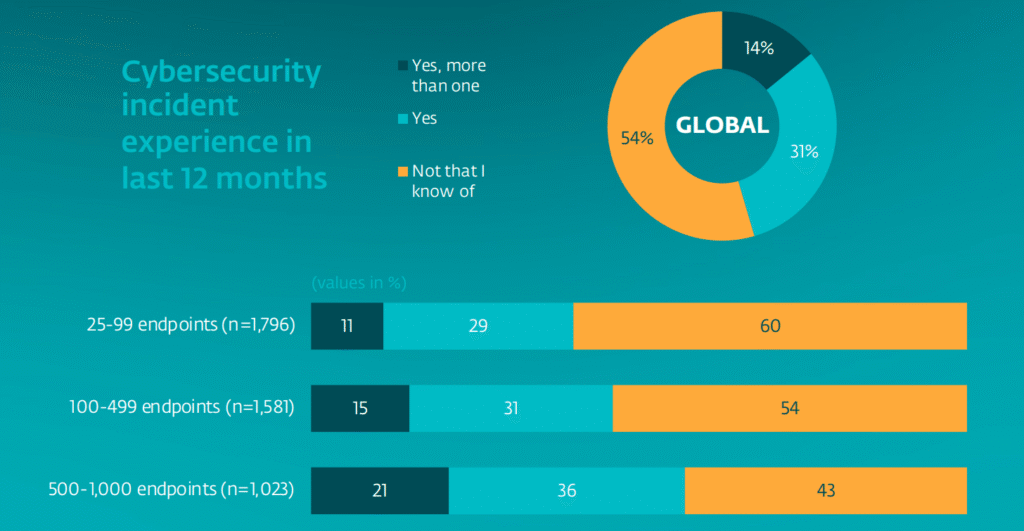
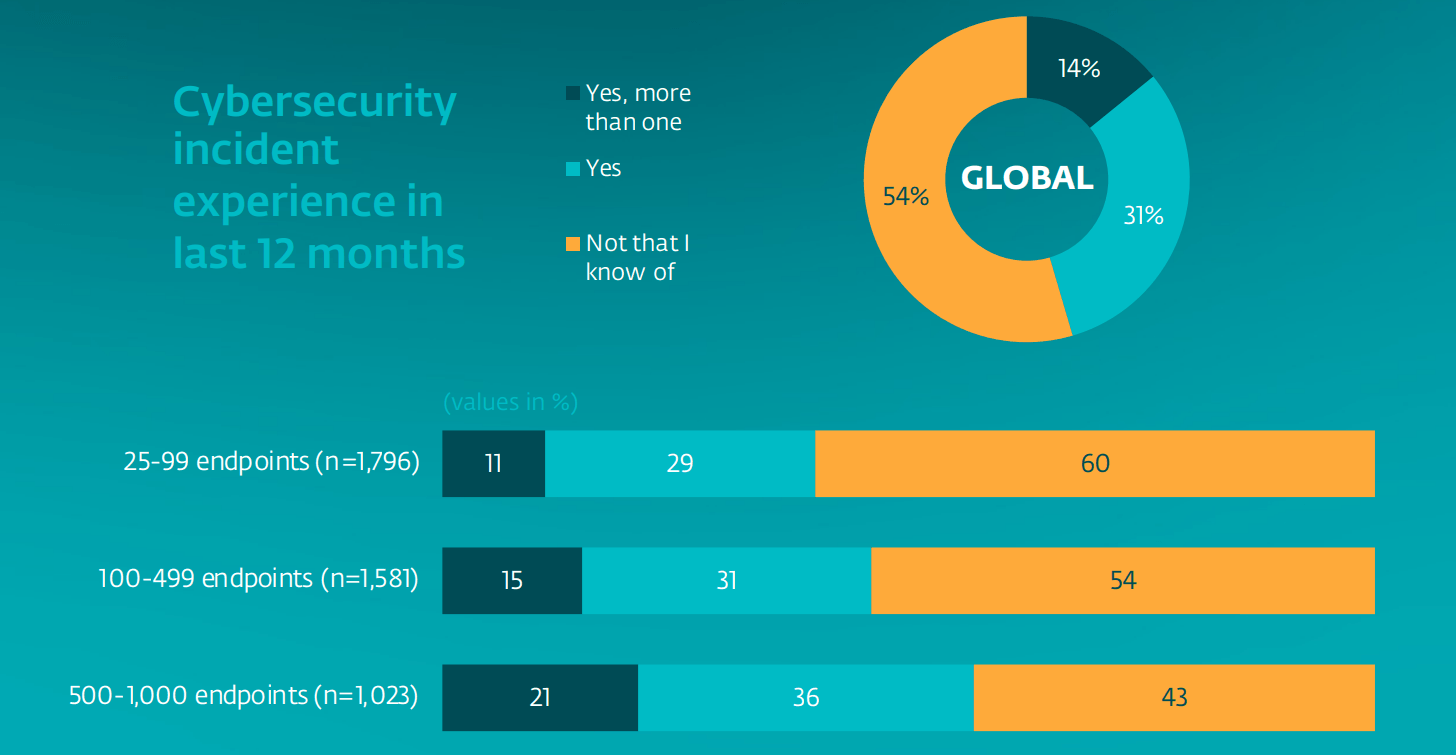
Thankfully, SMB IT and safety leaders get it and more and more take into account cybersecurity very or extraordinarily essential. Which may be as a result of many organizations have suffered a minimum of one cyber incident prior to now 12 months alone. These occasions are likely to focus the thoughts, notably once they’re vital or important and result in system downtime, knowledge breaches, ransomware, e-mail compromise, and extra.
However consciousness and motion are two various things. SMBs know they want efficient safety, however their efforts to attain this typically hit a well-known roadblock: complexity. Many typically say that even maintaining with the most recent developments and threats is a serious problem. The pace with which the menace panorama adjustments is only one of many contributing elements.
At a primary degree, safety finest practices stay broadly the identical, as do the kinds of menace that companies can count on. Phishing, vulnerability exploitation, infostealers, compromised credentials, and enterprise e-mail compromise (BEC) are nonetheless among the many hottest avenues for menace actors. AI merely amplifies and accelerates. Nonetheless, peel again the onion a layer or two and menace intelligence can grow to be intimidatingly complicated.
Understanding what a real menace to the group is and what to not fear about is commonly past the aptitude of a small IT safety workforce. They may have neither the time nor subject material experience to make an efficient evaluation. Safety typically suffers consequently, turning into reactive and piecemeal.
Distributors could make life tougher
The cybersecurity market can compound these challenges. The sheer number of options and providers on provide is staggering. It’s a world market value an estimated $248 billion, rising probably to $699 billion by 2034. This could make it troublesome to check vendor choices successfully, even when they’re nominally in the identical class. And as soon as bought, some options may be difficult for less-skilled groups to configure and function. Getting the suitable match for your online business is important.
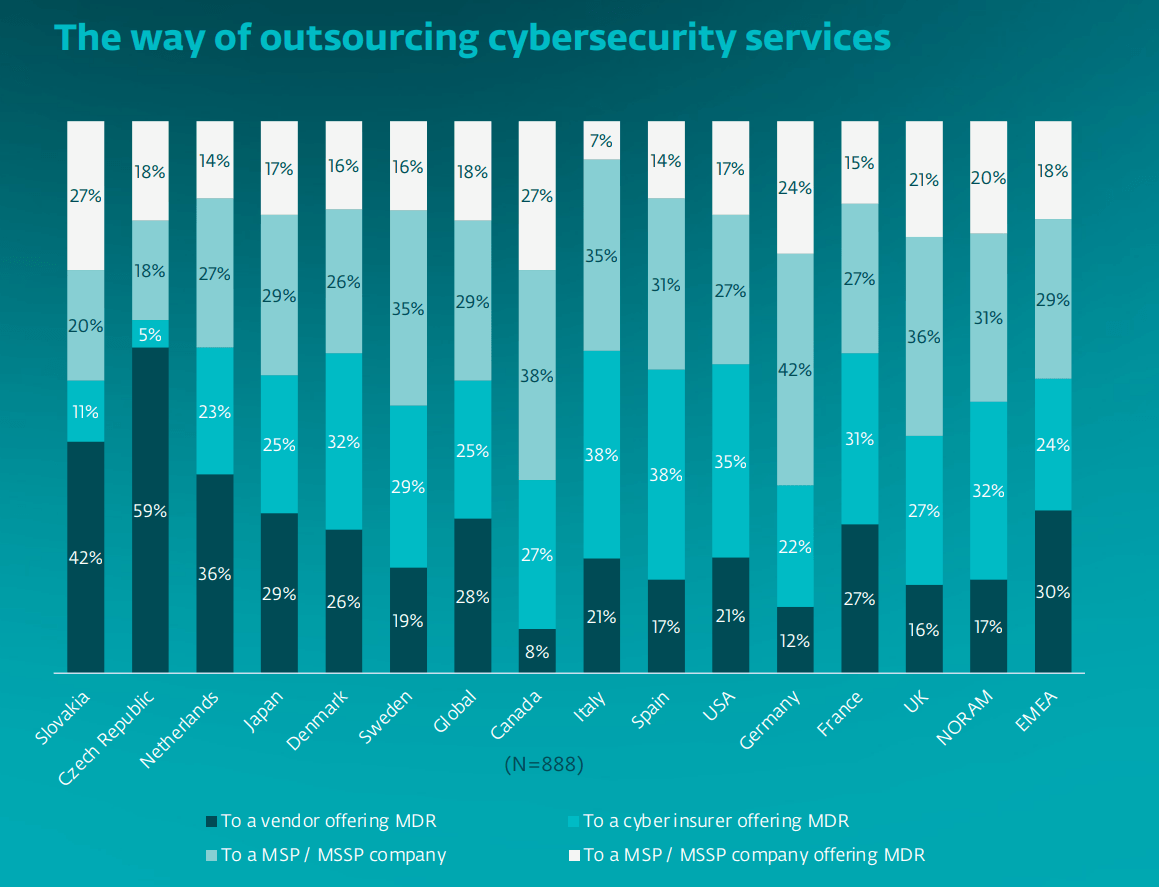
Over half (55%) of SMBs surveyed by ESET argue that the cybersecurity options market is complicated and complex, whereas practically a 3rd (30%) say answer complexity is a serious problem. The language utilized by the business will also be impenetrable. Round three-quarters (72%) need plain-language explanations. Many don’t know the that means of extensively used monikers like MDR, EDR and XDR.
The pathway to supervised help
But there’s some readability amongst this confusion. SMBs know that preventative safety is essential. However additionally they notice that in some circumstances menace actors will at all times get by these defenses. That’s why most companies ESET speaks to need safety that goes past ‘antivirus’ (AV) and important safeguards.
This additional layer of safety ought to operate as superior help for specialised threats, complementing in-house administration of primary safety controls. Fundamental options will block malicious executables, for instance, however what about refined menace actors residing off the land utilizing safe-looking instruments? Or an AI-discovered zero-day exploit for which there isn’t a signature? Detecting these threats is the facility of providers like MDR.
The problem is that they don’t work out of the field. Their effectiveness relies on how nicely a supplier’s folks, processes, and know-how are aligned together with your setting. Protection is crucial, as gaps can imply potential blind spots that hackers can exploit. If any exist, they need to be nicely documented and commonly reviewed as your IT setting continues to evolve.
Visibility should additionally lengthen to the tooling that you’ve got in place. Each group is totally different. Meaning specialist MDR groups should make clear at onboarding the precise IT setup of the consumer, to allow them to shortly spot if an unsanctioned software (like distant monitoring software program) seems, which can point out malicious exercise.
All of which makes onboarding and setup an important first step in a profitable MDR engagement.
What guided onboarding ought to embody
Most SMBs need step-by-step steering on establishing a brand new cybersecurity services or products. This may guarantee it’s built-in seamlessly into day-to-day operations. However what ought to that onboarding embody?
- A reside onboarding session with a vendor knowledgeable supplies an awesome alternative to ask questions as you’re being onboarded. Technical documentation is beneficial to check with in some circumstances. However it could possibly simply grow to be overwhelming for less-skilled IT professionals. That’s why a reside on-to-one session is invaluable; serving to you to fill within the gaps with plain English explanations and be taught by doing, not studying.
- Activation of the setting ensures it’s all up and operating and helps you get an early appear and feel of what to anticipate.
- Configuration and readiness checks are important to make sure the service is optimized to work together with your setting. Activation is simply step one. Configuration will get it operational. These checks are essential to do throughout guided onboarding as they could be difficult for a non-specialist workforce to carry out by itself.
- Steering on notification, reporting and communication is about serving to you perceive how alerts will come by and the way reporting is dealt with. You’ll be taught who will get the notifications in your aspect and what will likely be anticipated of them once they do. It’s important to get this proper as a way to forestall communication gaps between your workforce members and between your workforce and the seller.
- An all-in-one installer may also help to streamline deployment throughout all related endpoints, minimizing the configuration workload, and decreasing time and human error.
- Working by MDR operations, incident workflows and reporting is about understanding how your vendor associate investigates and communicates incidents, and methods to interpret studies. It’s about setting expectations on what your tasks are as soon as the supplier has recognized an incident. Few distributors will care for your entire incident and remediation workflow so figuring out what’s anticipated of your workforce is critically essential.
- A last set of finest practices and next-step recommendations will form your understanding of methods to preserve the service over time, because the IT setting and menace panorama change. Prioritizing what issues most when you’re up and operating is beneficial for groups with few assets who’re dedicated to steady enchancment.
Above all, do not forget that the engineer is there to information you thru the method, not do all of the heavy lifting themself. It’s about supplying you with the know-how to make the partnership a hit, and optimize your use of the services or products.
When achieved accurately, it ought to imply quicker time to safety, a decrease threat of misconfiguration, and improved confidence you can get essentially the most out of your funding.
Steering throughout use
When you’re up and operating, vendor ought to information you thru the method of incident detection and response. Meaning serving to you to grasp:
- What occurred: Explaining an incident in plain English. What sort of menace was detected. Which IT programs had been affected. How the adversary gained preliminary entry. Whether or not knowledge was compromised or stolen. And what stays unclear.
- Why it issues: Your vendor ought to assist by translating technical into enterprise dangers. That can assist you to perceive what the implications are for the group, reasonably than considering solely in IT phrases. For instance, a vulnerability exploitation might have enabled entry to a buyer database, which might increase the prospect of information loss and a GDPR investigation.
- What the supplier did: Your safety associate ought to element precisely what steps it took to research and include the menace, corresponding to resetting passwords or isolating accounts. And what has but to be achieved.
- What occurs subsequent: That is a very powerful a part of the steering. Your supplier ought to present actionable subsequent steps, ideally so as of significance. It might embody patching an exploited system, enabling MFA, restoring knowledge from backups, and many others. These suggestions ought to be clear, together with who’s accountable and ultimate timelines. As a result of when intrusions occur, minutes matter.
They need to additionally include supporting proof corresponding to logs that can be utilized to share with auditors, regulators and insurers if required. And to tell any buyer outreach or enterprise continuity efforts (corresponding to restarting programs) that could be required. Proof can also be important to attenuate the probabilities of an analogous incident occurring once more. Resilience is all about studying the teachings of every intrusion to shut off potential pathways for future threats.
Transparency is important
If SMBs don’t obtain this sort of readability and element throughout reside incidents, there’s a threat that they could mistakenly imagine malicious exercise has been remediated, when in actual fact there’s work left to do to include and resolve the difficulty. That may permit the blast radius of an assault to unfold, inflicting extra harm.
Prospects, regulators and different stakeholders may additionally stay in the dead of night, creating additional reputational and monetary threat. And the group itself is not going to have the forensic data at hand to enhance cyber resilience going ahead.
Essentially, if you happen to’re unable to find out what actions your supplier took, you’ll be able to’t calculate whether or not their service is definitely worth the cash you’re paying for it.
The worth of human relationships
SMBs perceive the worth of cybersecurity. They usually know that the menace panorama is turning into extra unstable, probably imperilling their enterprise. However these with out adequate experience are pissed off by the “recognized unknowns” that forestall them from understanding how the most recent threats and developments have an effect on their group.
That is the place safety distributors should step up. They’re trusted by extra SMBs than some other entity – together with inside employees, business friends, and governments – as a trusted supply of cybersecurity steering.
SMBs don’t need to hand over all management for menace safety. They need to be empowered by trusted companions to maintain their enterprise safer. On the heart of this dynamic sit human relationships – and we all know that SMBs worth entry to a human knowledgeable.
The important thing for distributors is to make sure these specialists can be found at onboarding, to information SMBs by configuration, activation and setup. And that they’re available throughout incident response, to elucidate what occurred, why it issues, what steps have been taken, and what there’s left to do. It’s the sort of supervised safety that might flip cybersecurity from a price of doing enterprise into a real development enabler for SMBs.