Observe us
Add us as a most popular supply on Google
Google has taken down an enormous Android malware operation that turned over 1.3 million Android TV containers into weapons for cyber criminals.
The corporate revealed that the operation was carried out by Videostrong Know-how, a tool maker that has been accused of deliberately placing a hidden backdoor on its merchandise and promoting entry to felony associates.
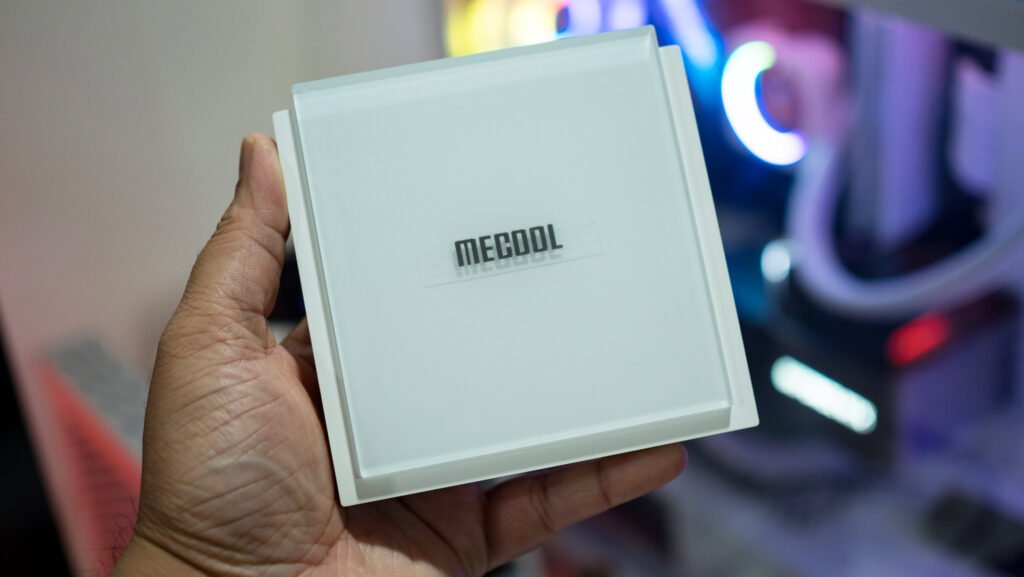
The malware, dubbed XCPE or x.cpe, was instantly embedded within the firmware of Android TV containers offered beneath completely different manufacturers. Google’s Risk Intelligence Group stated that Videostrong developed the backdoor as a enterprise, not letting it slip by by accident. Prison companions may use contaminated gadgets to generate pretend advert views, reroute web site visitors by unsuspecting houses, and set up extra malware.
Newest Movies FromAndroid Central
A backdoor that provides criminals management of your TV field
Google is especially involved about XCPE as a result of it runs with Android system-level privileges. It connects to distant command-and-control servers, enabling attackers to silently set up purposes, execute shell instructions, take screenshots, and accumulate gadget info.
Google additionally discovered that the malware may accumulate account info, utility lists, and system logs. Some operators even used the flexibility to remotely entry the gadgets to seize keystrokes and set up reverse shells.
Simply eradicating the malware utility isn’t sufficient, although. The backdoor can restore itself from a protected firmware partition on each gadget reboot. It might additionally have an effect on Google Play Defend by altering the safety settings, making it rather more troublesome to detect and take away.
The most typical approach the an infection spreads is thru Android TV containers, however researchers additionally noticed XCPE on different Android-based gadgets resembling karaoke machines, telehealth tools, and digital signage techniques.
Google cuts off Videostrong and its felony companions

Google labored with Japan’s Nationwide Police Company, Lumen, HUMAN Safety, Plume, Synthient, and TrendAI to take the operation down. Its grievance focused command servers operated by Videostrong, in addition to the infrastructure behind greater than a dozen different households of malware.
The corporate additionally banned Videostrong and future subsidiaries from making licensed Android gadgets or supplying software program to licensed producers.
The disruption may unfold even additional. Disabling the command infrastructure utilized by felony associates will lower off entry to at the least 10 million extra compromised gadgets contaminated by completely different distribution channels, Google figures.
Contaminated Android TV containers would possibly want changing
There’s a catch for shoppers, nonetheless: the takedown doesn’t robotically take away XCPE from impacted {hardware}. Based on safety researchers, customers ought to establish doubtlessly compromised gadgets, disconnect them, and take into account substitute relatively than counting on an atypical app uninstall.
Google additionally tightened its firmware integrity checks and producer vetting course of after it discovered that Videostrong used obfuscation to load malicious code after a tool initially booted up.