
Passwords and API keys that builders typed into instructions they accepted in Claude Code are sitting in public GitHub repositories, the place anybody can learn them.
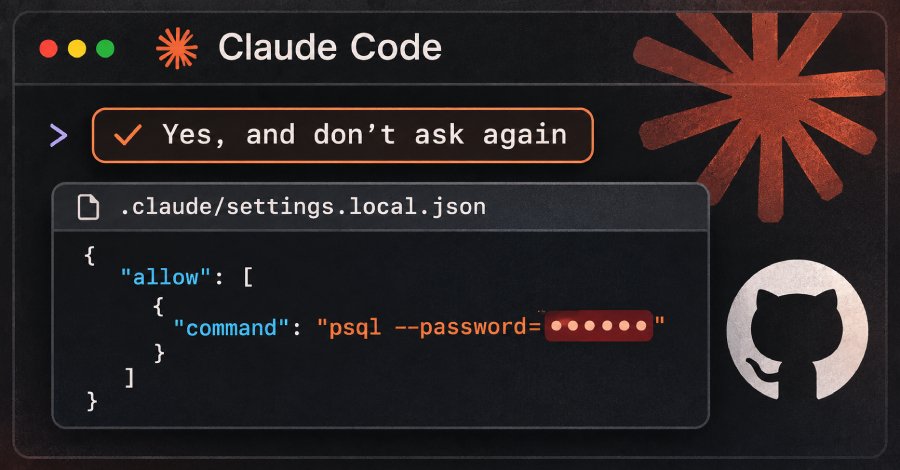
When a person selects “Sure, and do not ask once more,” Anthropic’s AI coding assistant can save the command, word-for-word, together with the key, in a mission settings file.
Software program safety firm Apiiro stated yesterday that 1,122 public copies of that file maintain at the least one secret, although it didn’t check whether or not any nonetheless work. One firm the researchers notified earlier this week confirmed its key had been dwell.
The file is .claude/settings.native.json. Eradicating it from a mission doesn’t undo the leak, as a result of older variations keep in git historical past and in forks of the repository. The researchers’ recommendation is to rotate first: change each password, token, and key the file has ever held, then clear up.
How a Secret Lands within the File
By default, Claude Code asks earlier than it runs most shell instructions. If the person picks “Sure, and do not ask once more,” it saves an enable rule in .claude/settings.native.json contained in the mission, in line with its permissions documentation. Matching instructions then run with out asking in later periods.
The rule covers solely what the immediate supplied. Typically that may be a sample, similar to npm check *, and generally one precise command. When it’s the precise command, any password or token typed into it’s saved too, in plain textual content.
In public information, the researchers discovered saved instructions with the key nonetheless inside, and so they reproduced the habits with the newest fashions, Opus 5.5 and Fable 5.1.
Claude Code tries to maintain the file out of git. The primary time it writes the file in a git repository, it provides the file to the person’s international git excludes, its settings documentation says. Git on that pc then ignores the file in each repository.
That safety stays in a single person’s git settings on one pc. It does nothing for a file that was already dedicated, the researchers say. Claude Code by no means provides the file to the mission’s personal .gitignore, so the safety doesn’t journey with the mission.
In 539 of the 1,105 repositories the researchers traced, a commit itemizing Claude as a co-author modified the file. They take this to imply Claude typically commits the file itself.
What Apiiro Discovered
Apiiro’s search of public GitHub discovered 104,185 copies of the file in 103,617 repositories, its analysis write-up exhibits. About 1.1% of them, or 1,122 copies, maintain at the least one secret. Collectively they maintain 1,379 completely different secrets and techniques.
A price counted as a secret when it matched a identified key format, or when a password or token sat beside the handle of a public server. An AI reviewer additionally needed to agree. The researchers don’t say whether or not anybody has used these secrets and techniques.
Greater than a 3rd of the secrets and techniques open a database immediately, together with 379 database passwords. Others embrace 43 SSH logins for public servers, 42 tokens for GitHub, GitLab and npm, and 23 AWS keys.
Among the many house owners of those information are 63 organizations, principally software program firms of all sizes. The strongest circumstances embrace a database vendor’s personal admin-level cloud key and the proprietor password of a medical-records database, the researchers say.

As of Monday, each file with a secret was nonetheless on its repository’s default department, and in half of these repositories it had been there for at the least 217 days.
Older variations of the file comprise 734 extra secrets and techniques throughout 509 repositories that aren’t current in any present copy, often as a result of the file was deleted. Forks unfold the information additional: 211 forks of 74 repositories carry the identical secrets and techniques because the originals.
Secrets and techniques additionally sit in 298 of 76,011 copies of the shared .claude/settings.json file, which groups commit on function, principally inside enable guidelines. Together with these, the older variations, and saved agent chat logs, the overall is 2,539 secrets and techniques throughout 1,994 repositories.
Of 16 coding brokers whose documentation the researchers in contrast, Claude Code is the one one confirmed to avoid wasting the complete accepted command in a mission file by default.
What to Do
For builders, the researchers advocate these steps:
- Search your GitHub group for .claude/settings.native.json and .claude/settings.json, and verify every repository’s git historical past for them, even the place the information are gone.
- Rotate each password, token and key the information have ever held, earlier than cleansing up.
- Cease monitoring the native file with git rm –cached .claude/settings.native.json, and add it to the repository’s personal .gitignore.
- Open the file by yourself pc, even when it was by no means dedicated, and delete each rule that accommodates a secret.
- Maintain secrets and techniques out of instructions. Discuss with them as variables from a secrets and techniques supervisor, similar to $DB_URL, so the saved rule holds the variable identify and never the key.
- Approve patterns, similar to Bash(npm run:*), as a substitute of single instructions.
Copies that by no means attain GitHub nonetheless matter, the researchers say. The file is obvious JSON within the mission folder, and it may also be left inside an npm bundle, a Docker picture, a zipper archive, or a synced folder.
Malware has beforehand appeared for secrets and techniques on developer machines. In September 2025, the Shai-Hulud worm ran the TruffleHog secret scanner over contaminated computer systems, and the scanner flagged greater than half of the information as secret.
Frequent secret scanners miss many of those information. The researchers ran gitleaks and TruffleHog over each copy, with out the instruments’ verification step. Of the 1,122 information with a secret, gitleaks flagged 564 and TruffleHog 643, and neither flagged 215.
Most misses are passwords typed inside instructions. Scanners search for identified key codecs, and a password after PGPASSWORD=, sshpass -p , or mysql -p appears like an strange phrase in an strange command line.
For safety groups, the researchers advocate:
- Deal with agent folders similar to .claude/, .cursor/, .gemini/ and .specstory/, and agent reminiscence information, as holding secrets and techniques, like .env information, on laptops in addition to in repositories.
- Add them to pre-commit and CI secret scanning, together with git historical past, and ensure the scanner catches passwords inside instructions, not solely identified key codecs.
- Add .claude/settings.native.json to the group’s .gitignore templates.
- Verify credentials paired with a public server first, as a result of these are those that give entry.
Earlier Studies
Claude Code customers have reported this habits earlier than. An earlier bug report, filed on August 11, 2025, stated accepted instructions with API keys and tokens had been being saved phrase for phrase in settings.native.json.
An automatic bot closed that report as “not deliberate” on January 3, after 60 days with out exercise.
As of at this time, the 4 associated studies the researchers cite have all been closed by the identical bot, the newest yesterday. None received a reply from Anthropic, they are saying.