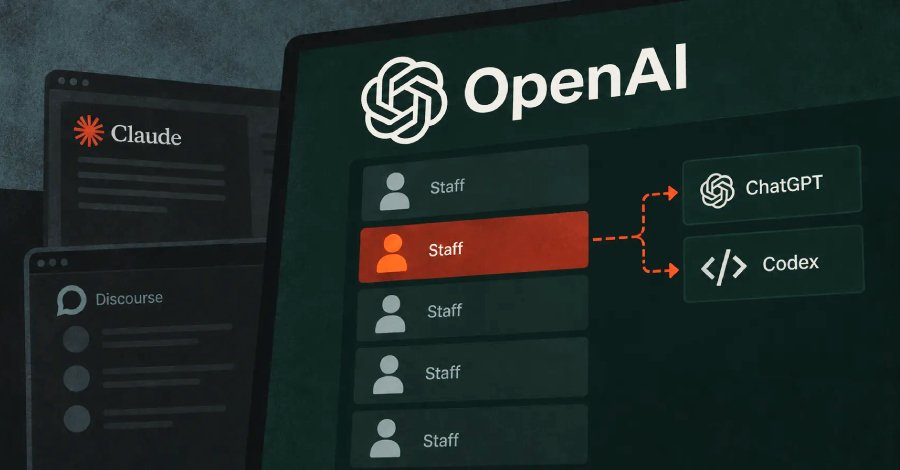

Three researchers on the safety agency Hacktron used Anthropic’s Claude Opus 5 to chain two flaws and take over the ChatGPT and Codex accounts of a number of OpenAI staff, then attain an inner OpenAI code repository.
The chain started with a bug within the software program that runs OpenAI’s public assist discussion board and moved by way of a weak point in OpenAI’s personal login system.
This was safety analysis, not a real-world assault: the group reported the failings to OpenAI, proved the entry with a innocent pull request, after which stopped. From the primary look, that inner entry took below 72 hours.
OpenAI confirmed a repair about 14 hours after the report, in response to Hacktron, and on September 1 paid the group a $6,500 bounty. OpenAI mentioned the award “acknowledges the OpenAI-side discovering, not the actions in opposition to Discourse,” the open-source software program that runs the discussion board. Testing the discussion board itself was exterior its bug bounty program.
OpenAI has not publicly described the login flaw, and it confirmed the discovering by way of that repair and fee quite than by detailing the account takeovers.
Hacktron, which describes itself as an AI-assisted safety analysis agency, was cautious about what it did and didn’t do. When one worker’s Codex hyperlink to OpenAI’s code on GitHub was opened, it triggered a single pull request within the inner repository. It didn’t learn any supply code, merge or ship something, or contact buyer information.
What the chain may have reached was far bigger. As a result of workers connects different providers to ChatGPT and Codex, the group mentioned the identical entry may in idea have prolonged to instruments similar to GitHub, Slack, and e-mail. That wider attain was potential, however not used.
Why a Discussion board Bug Reached Workers Accounts
The rationale a bug in a public discussion board may attain workers accounts lies in OpenAI’s login system, not within the discussion board software program. OpenAI’s discussion board provides a “Sign up with OpenAI” possibility, the identical single sign-on (SSO) that workers makes use of elsewhere.
As soon as the researchers took management of the discussion board server, the shared login allow them to take over the ChatGPT and Codex accounts of discussion board members who labored at OpenAI. The victims didn’t should do something.
Hacktron mentioned this was an OpenAI identification drawback, not a flaw within the discussion board software program: any first- or third-party service utilizing the identical sign-on may have granted the identical entry.

The way in which in was a picture bug. The discussion board runs on Discourse, and Discourse passes uploaded HEIC and HEIF pictures to a device known as ImageMagick, which makes use of the libheif library to learn them. A flaw in libheif let a specifically crafted picture corrupt the discussion board server’s reminiscence.
Discourse’s advisory charges the consequence as distant code execution, scores it 8.8 out of 10, and tracks it as CVE-2026-32882. The general public file for the flaw itself is narrower. In libheif’s personal advisory and in nationwide vulnerability databases, CVE-2026-32882 is an out-of-bounds learn that may crash the software program or leak close by reminiscence, not a direct code-execution bug.
That leaked reminiscence helps defeat a typical safety known as ASLR. The researchers say they mixed libheif’s reminiscence bugs, with the AI’s assist, to show the crash into working code execution on the discussion board server. Upstream, the flaw was mounted in libheif 1.22.0 in Might 2026.
That repair existed months earlier than the check. However the discussion board’s server picture, constructed on the Debian 12 Linux distribution, nonetheless shipped the outdated, unpatched libheif, model 1.19.7, when the researchers appeared in July. The repair and its CVE had been already public, however Debian had not but included them within the packaged model the discussion board used.
If you happen to run your individual Discourse server, this half impacts you straight. Rebuild on the newest picture to get the patched libheif, as a result of a web-interface replace alone might not change the outdated library. Websites hosted by Discourse had been already patched, and the mounted self-hosted releases are 2026.7.0, 2026.6.1, 2026.5.2, and 2026.1.6.
How the Researchers Used AI
The researchers used AI to do the exhausting half. They first tried Claude Opus 4.8, which struggled over a number of classes to construct a working exploit as soon as an ordinary reminiscence protection, ASLR, was enabled.
Anthropic launched its subsequent mannequin, Claude Opus 5, on the night of July 24, and in a contemporary session it produced a working exploit inside hours.
Opus 5 shipped with safeguards meant to cease it from writing exploit code for actual targets. The researchers obtained round them by pointing the mannequin at their very own check server, disguised as a capture-the-flag apply goal, then letting it run in an automatic loop. Even so, they are saying the work was not hands-off: expert human route nonetheless mattered, and this was not automated hacking with nobody on the controls.

The case matches what researchers and AI corporations have described this 12 months: succesful AI fashions are sharply chopping the time and talent that severe offensive work used to take. Anthropic has reported that legal and state-backed teams are already utilizing its Claude fashions to run actual intrusions, not simply to reply questions.
OpenAI was one goal in a wider venture Hacktron calls HEIF Heist. Over about two months, the group says, it discovered the identical class of image-decoding flaws in software program utilized by different massive corporations, at a complete price of below $3,000 in AI utilization. It hyperlinks the marketing campaign to reported bugs in Slack, Meta’s merchandise, GitHub Enterprise, and net frameworks similar to Subsequent.js.
These broader claims are backed inconsistently. The Subsequent.js flaw is confirmed in Vercel’s personal advisory, and libheif’s maintainers confirmed a working code-execution exploit for the bug tied to Meta. The broader declare of code execution throughout many purposes has not been independently confirmed, a restrict The Hacker Information famous when it first lined the Subsequent.js flaw in August.
The broader marketing campaign used a special mannequin, OpenAI’s personal GPT-5.6 Sol, for circumstances the place the group knew nothing concerning the goal prematurely. Just one firm, Shopify, seems to have seen the exercise, the researchers say, regardless that its picture processors crashed repeatedly below hundreds of check uploads.
The Hacker Information has contacted Hacktron with questions on how the discussion board code execution was achieved and concerning the scope of the account entry.
What to Do
The larger classes transcend Discourse. In case your service accepts consumer pictures and reads HEIC, HEIF, or AVIF information by way of libheif, an outdated construct might be uncovered.
And if a public, lower-trust service shares your single sign-on with inner instruments, a break-in on that service can grow to be a break-in in every single place the identical login reaches.
- Replace libheif to the newest safety launch (1.23.4 as of early September 2026) or to your distribution’s patched construct.
- The place you don’t want it, flip off decoding of untrusted HEIF and AVIF pictures, or run picture processing inside a locked-down sandbox.
- Restrict which providers your single sign-on trusts, and require a contemporary identification test earlier than delicate actions quite than trusting an present session.
There isn’t a signal the OpenAI flaw was used in opposition to anybody in the actual world. As of mid-September 2026, it was not on the U.S. authorities’s checklist of vulnerabilities identified to be exploited, although that checklist is just not proof both method.
What the accessible stories don’t settle is whether or not a corporation that has already patched ought to nonetheless test for earlier entry; on that time, the sources are silent.