The cyberthreat panorama has been evolving for years. However there’s a way as we speak that issues are escalating extra quickly than earlier than. That’s largely the results of AI. The know-how shouldn’t be solely arming menace actors with the means to launch extra subtle assaults at better velocity and scale than earlier than. It’s also offering them with a bigger assault floor to goal at, as companies rush to undertake the know-how. In lots of circumstances, that adoption is outpacing the important governance efforts wanted to securely handle and comprise it.
In opposition to this backdrop, SMB enterprise and IT leaders perceive the significance of efficient cybersecurity. They need to be protected, operational, and resilient. However they don’t have an infinite finances to spend. They need safety that’s easy to grasp, undertake and function. This requires a special operational mannequin the place AI and automation assist safety groups the place it is smart, with human oversight for choices that require context and judgment. Discovering the appropriate stability, and the appropriate associate shall be key to driving readiness and resilience.
AI is altering the menace panorama
AI is altering the sport in spectacular methods. Executives are wowed by the potential for productiveness and course of effectivity good points. By the prospect of reworking buyer expertise, accelerating enterprise determination making, and breaking into new markets. ESET SMB Cyber Readiness Index 2026 discovered that the majority (73%) SMBs are integrating AI into their enterprise.
But the place there’s alternative, there’s additionally danger – and most companies acknowledge that. As AI turns into a rising a part of enterprise operations, it additionally turns into a part of the assault floor. It could possibly be a customer support chatbot, a coding assistant deployed by DevOps, or a fleet of brokers utilized by the finance staff for repetitive bookkeeping duties. Wherever AI has entry to delicate information and/or techniques, extreme permissions, and the flexibility to make choices and take actions, it represents a possible safety danger. These dangers are inclined to proliferate within the darkness. In response to the report above, 40% of all companies lack a correct AI coverage.
Unintentional information leakage or rogue AI brokers are one factor. However there’s arguably an excellent better menace from malicious third events. AI expertise repositories are a rising space of danger. Abilities work like browser plugins, however for AI brokers. However a rising quantity are designed to steal information, abuse permissions, obtain malware, or carry out unintended actions. ESET analyzed 900,000 such expertise throughout a number of fashionable repositories between March and Could 2026. It found over 25,000 that have been suspicious, and greater than 3,000 tagged as malicious. Some exfiltrated information and executed malware. Others manipulated delicate techniques, overrode directions via immediate injection, and altered agent habits.
Sadly, expertise are simply the tip of the iceberg. Customers can encounter malicious hyperlinks through chatbots, main them to phishing websites and malware installs. Or they might discover attackers have poisoned obtain sources and different parts that AI brokers work together with, resulting in hijacking, fraud, malware and different threats.
Immediate injection is one other menace – one just lately branded probably the most harmful of all LLM threats by OWASP. Attackers manipulate AI both by feeding malicious directions (prompts) immediately or hiding them in content material that the AI will later retrieve or learn. It makes each piece of content material a possible assault vector.
AI turns up the warmth
AI isn’t just a goal for assault. It’s a strong device for menace actors to wield in assaults. As British authorities safety consultants warned again in March 2025, the know-how “will nearly definitely proceed to make components of cyber-intrusion operations simpler and environment friendly, resulting in a rise in frequency and depth of cyber threats.” It names a number of areas of notably word, together with:
- Sufferer reconnaissance: AI can automate and improve the method of trawling via social media accounts, firm web sites, and different sources to shortlist potential victims. Then it may possibly map relationships to assist with phishing and fraud, and discover assault paths to strive. Most significantly, it does all this work at a velocity and scale that may not have been doable a yr or two in the past.
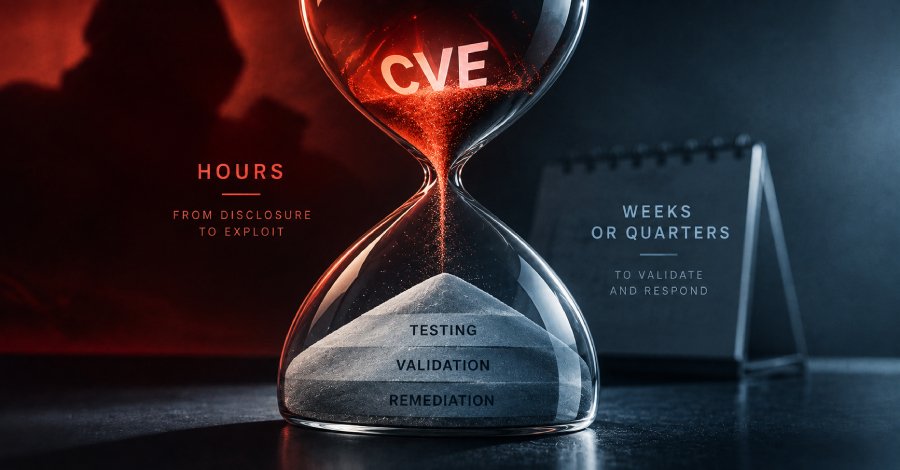
- Vulnerability analysis and exploit growth: One of the impactful use circumstances of AI in latest months. The know-how has successfully collapsed the exploitation window, enabling menace actors to search out novel vulnerabilities, and to develop exploits for newly found flaws earlier than most community defenders have had time to check and deploy patches. This has sparked warnings from numerous quarters, together with the UK’s monetary authorities, and their counterparts in New York.
- Social engineering: Composing extremely convincing, fluent and error-free messages to trick victims into clicking on malicious hyperlinks or handing over cash, private info or login particulars. When mixed with AI-powered sufferer reconnaissance, it’s a doubtlessly highly effective device for large-scale, extremely personalised phishing campaigns in native languages.
- Fundamental malware growth: AI is reducing the barrier to entry for much less expert menace actors, lowering the information wanted to show an thought for a marketing campaign into working code, albeit pretty unsophisticated malware. ESET has additionally noticed AI in use elsewhere, akin to PromptSpy, the primary AI-powered Android adware. This menace abuses Google’s Gemini at runtime to realize persistence.
- Processing exfiltrated information: AI quickly classifies, cleans-up, and extracts giant volumes of data from stolen information in an effort to make it extra monetizable/usable for cybercriminals.
Using AI brokers that may be set to work autonomously on duties at machine velocity might drive even better productiveness advantages for menace teams. For community defenders, this new panorama calls for an association that may hold tempo with out asking the already-stretched groups to interpret each alert and make each determination alone.
Why SMBs are fighting complexity
Sadly, safety groups are already on the again foot. They wrestle with IT and cybersecurity complexity – the rising variety of techniques and instruments they’re anticipated to handle. And the know-how required to deploy, optimize and monitor these options for the most effective outcomes. This could problem even a big enterprise. So it’s no shock that SMBs specifically are struggling, given their relative lack of time, expertise and assets.
Fixing this downside isn’t a case of shopping for extra know-how to take a seat on prime of what they’ve beforehand put in. That can solely compound complexity and stretch information and assets even additional to breaking level. SMBs don’t need extra dashboards and alerts to research. They want safety that simplifies. AI-driven instruments tackle repetitive evaluation and prioritization whereas human consultants examine ambiguous circumstances and information the response. The result’s robust safety that’s simpler to grasp, undertake and run.
These SMB ache factors will be summarized as follows:
- Too many instruments, alerts, dashboards and technical choices to make. Safety is just too advanced, making it obscure if the group is correctly protected and what to prioritize
- Stretched groups which regularly don’t comprise any cyber consultants. There’s no hope of investigating each alert with small in-house groups
- No 24/7 monitoring, that means threats sneak into the enterprise throughout evenings, weekends and holidays. Dwell time surges, rising the chance of main enterprise disruption
- Alert fatigue that stems from a insecurity and know-how in safety operations (SecOps). Groups waste time chasing false positives whereas false negatives sneak in
- Operational disruption and enterprise influence stemming from incidents. SMBs don’t simply concern the technical incident. They’re saved awake by the misplaced income, downtime, buyer churn and reputational harm that would consequence
- Misconfigured safety purchases, which might result in detection blind spots and influence cyber readiness
- AI adoption at tempo usually leaves governance gaps which result in information leaks, unsafe outputs, shadow AI and different enterprise dangers
- Safety which creates an excessive amount of work, reasonably than empowering SMBs to make higher choices
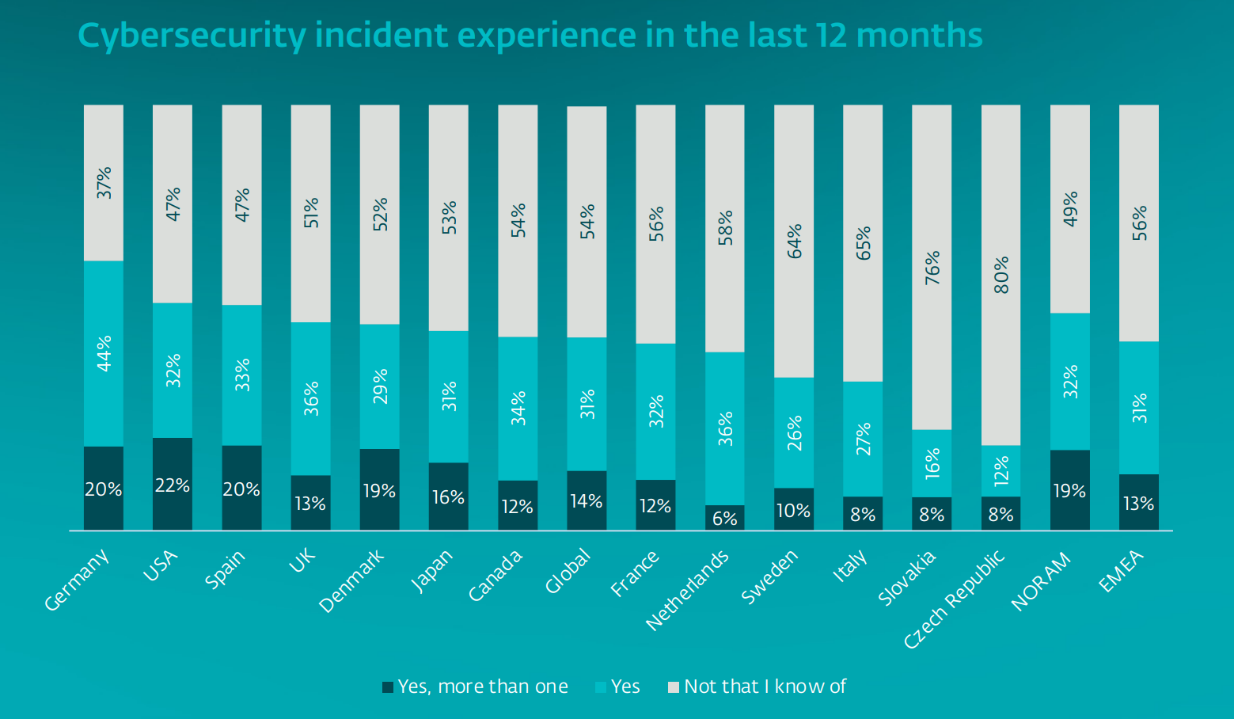
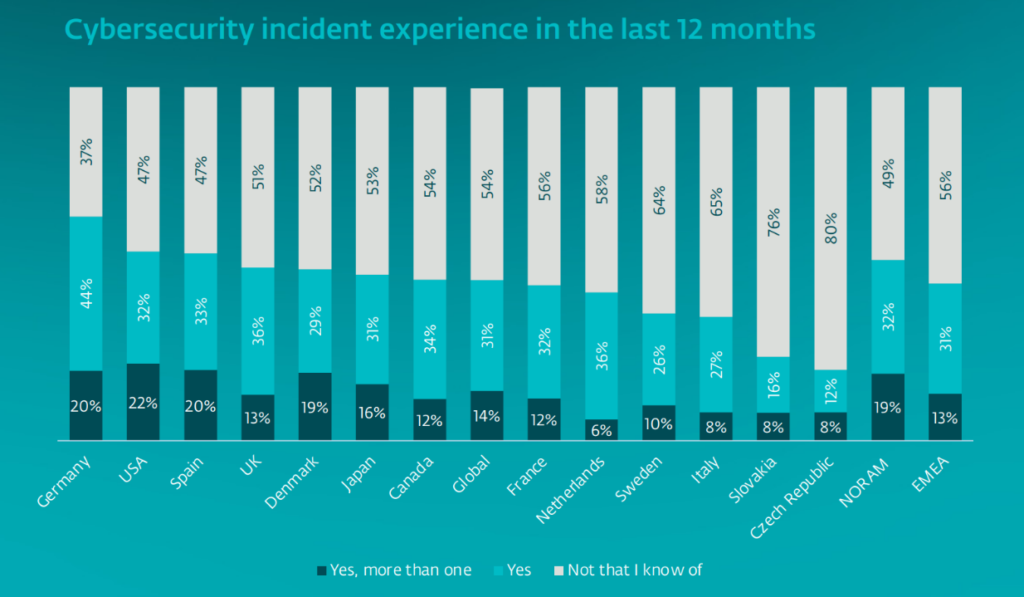
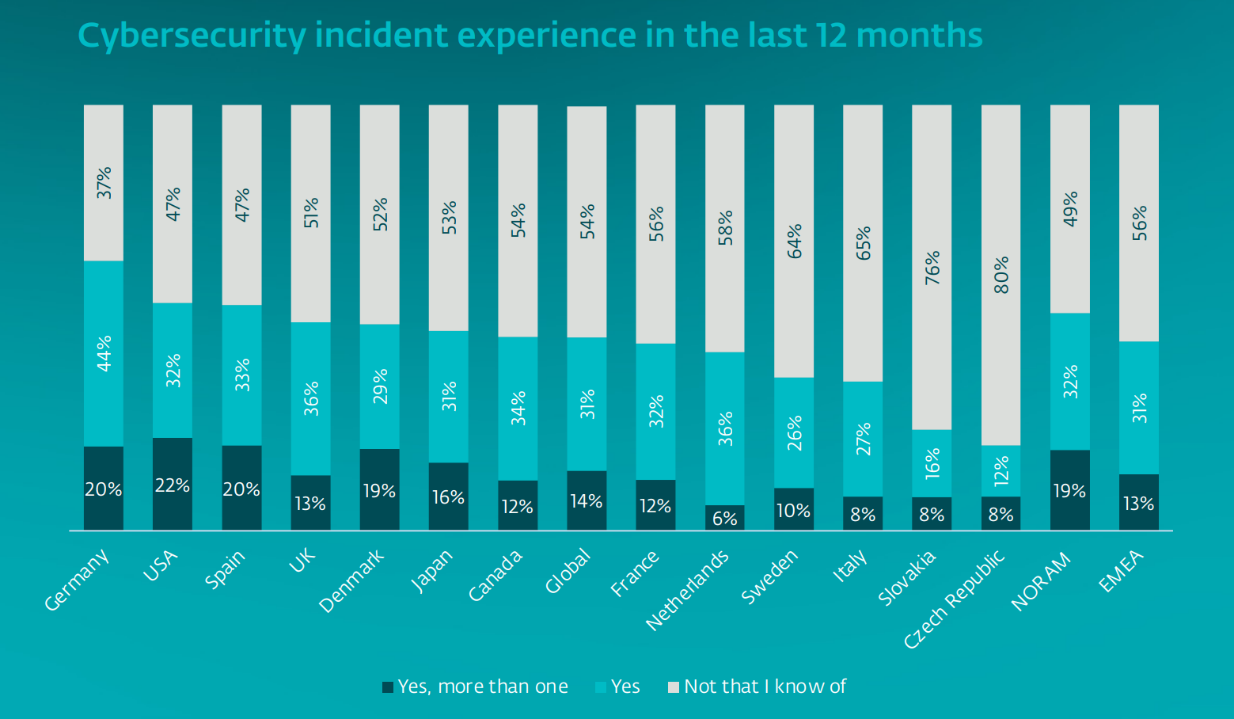
In opposition to this backdrop, safety should not solely be easy to grasp and easy to make use of. It should additionally assist the core requirement of operational resilience. Our information reveals that almost half (45%) of world SMBs suffered a cybersecurity incident final yr. And two-fifths (40%) cite operational disruption as their largest concern. The truth is, it’s the consequence most continuously related to important or crucial influence.
If breaches are more and more inevitable, the important thing for SMBs is subsequently to find intrusions as rapidly as doable, stand up to the onslaught, and keep minimal viable operations whereas recovering as rapidly as doable. These firms finest outfitted to realize this sort of resilience aren’t those with the largest funding in AI or the most important safety stack. They’re those with a keener give attention to aligning know-how with enterprise outcomes. On investing in safety that may assist them make higher choices below strain for operational continuity.
That is much more essential at a time of financial uncertainty the place money reserves are low, safety budgets are slim, and even brief durations of downtime can have an outsized impact on the underside line.
What occurs subsequent?
ESET information reveals that SMBs are taking cyber critically. They’re investing in safety. But for a lot of, these investments are nonetheless largely about managing issues in home. Readiness lags, that means organizations don’t have the processes and controls in place to stop, detect and reply to threats successfully. Few have put in place documented incident response plans which are usually reviewed.
That’s why they want a safety associate they will belief that gives complete, prevention-centric capabilities to deal with conventional threats, in addition to an additional layer of safety that displays for threats and permits organizations to take fast motion to comprise and get better. AI can assist that layer course of and prioritize exercise at a scale that small groups can’t handle alone. Skilled third-party groups can examine what it surfaces and information the response, appearing like an extension of the shopper’s personal in-house IT employees.
That method, the shopper stays answerable for their very own surroundings and determination making. However it additionally ensures safety turns into simpler to grasp and function. Highly effective safety, delivered as a service for max safety with out the necessity to keep a big in-house safety staff.
Any safety associate delivering these capabilities should be capable of cowl the complete assault floor, from endpoints and cloud servers to collaboration instruments, id and – in fact – AI. Which means safety for AI conversations, brokers, AI-generated outputs, AI parts, delicate information, and the broader AI ecosystem. A trusted safety associate would additionally leverage AI and automation to chop the operational burden on its clients and speed up menace detection and response. Consultants would oversee investigations and convey enterprise context to consequential choices.
Decreasing danger, defending operations, rising confidence
The excellent news is that each one of that is doable as we speak. Safety designed to beat conventional operational complexity and functionality gaps. Delivered as a service by consultants to construct confidence and resilience with out overwhelming. With the appropriate associate, SMBs can profit from enterprise-grade safety to scale back danger throughout the company assault floor.
That can spur safer adoption of AI, to create new enterprise alternatives and efficiencies. And operations which proceed to operate even throughout incidents, so that you’ll by no means should let your clients down. Easier safety that permits your staff to give attention to what issues; assured that they’ve what it takes to cease even novel threats.