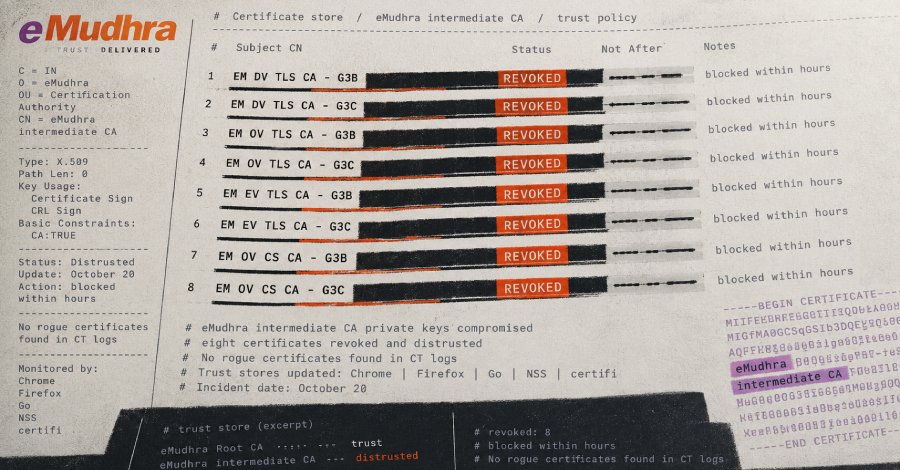

The non-public keys of eight eMudhra intermediate certificates authority (CA) certificates are compromised, Mozilla and Google’s Chrome Root Program confirms on October 20.
An intermediate CA indicators the certificates that web sites current, so anybody holding one among these keys may problem a certificates for any web site {that a} browser would settle for.
A researcher reported the compromise to the foundation applications on the night of October 17, and Chrome and Firefox blocked the eight certificates inside hours, after Chrome verified the findings.
No TLS certificates chaining to the six intermediates used for web sites had been logged to Certificates Transparency (CT) earlier than Chrome’s block, so none may have been trusted by default in Chrome or another browser that requires CT logging, the Chrome Root Program mentioned.
It isn’t identified how the keys left eMudhra, when, or whether or not anybody moreover the researcher holds them.
The keys are those Go blocked in its October 20 safety releases with out naming the CA, as The Hacker Information reported earlier. The eight hash values in Go’s code match the eight certificates. Go dealt with the repair on its URGENT observe, which its safety coverage reserves for threats to the ecosystem’s integrity or flaws being exploited within the wild, and neither the difficulty nor the discharge notes say which utilized.
What Was Compromised
eMudhra is an Indian CA that sells certificates underneath the emSign model via firms in India, america, and the Netherlands, and it has roots within the Mozilla, Chrome, and Apple root shops. The eight compromised certificates are:
- TLS, area validated: EM DV TLS CA – G3B (eMudhra BV, Netherlands) and EM DV TLS CA – G3C (eMudhra Inc, United States)
- TLS, group validated: EM OV TLS CA – G3B and EM OV TLS CA – G3C
- TLS, prolonged validation: EM EV TLS CA – G3B and EM EV TLS CA – G3C
- Code signing: EM OV CS CA – G3B and EM OV CS CA – G3C
The six TLS certificates had been issued by emSign Root TLS CA – G3 and chain to emSign ECC Root CA – G3, a root within the Chrome and Apple shops and, till October 20, in Mozilla’s.
Every of the eight additionally exists as a second certificates with the identical public key, cross-signed by Sectigo underneath its AAA Certificates Companies root, in accordance with a certificates listing printed by Dennis Jackson, a Mozilla cryptography engineer.
Chrome didn’t want to dam the 2 code-signing certificates, as a result of its TLS verifier won’t construct a path via an intermediate restricted to code signing, the Chrome Root Program mentioned.
Who Is Protected, and How
The Chrome Root Program obtained the report at 18:05 UTC on October 17 and had a CRLSet replace blocking the six TLS intermediates in place by 19:45 UTC.
Mozilla obtained it at 20:06 UTC and completed pushing a OneCRL block to Firefox installations with customary settings at 22:59 UTC. CRLSets and OneCRL are revocation lists that the 2 browsers fetch on their very own, so neither wanted an replace or a restart.
Chrome’s block matches the general public key fairly than the certificates, so it additionally catches the Sectigo cross-signed copies. It’s the similar mechanism Chrome used earlier this month in opposition to rogue certificates for Google domains.
The researcher, credited by Mozilla solely as Wayne, signed the message “We’ve an issue right here – Wayne” with every of the eight keys and despatched it to the foundation applications that day, in accordance with Jackson, who printed the signatures and certificates on a one-page website.
eMudhra has revoked the eight certificates. Apple blocked them on October 19, Microsoft on October 20, and different belief shops had been notified on October 19, in accordance with Jackson’s website.
The cross-signed copies didn’t widen the chance in Chrome or Firefox. Each stopped trusting Sectigo’s AAA Certificates Companies root for web sites in April 2025, and Chrome’s root retailer file doesn’t carry it. Apple’s root listing for iOS 26 and macOS 26, printed in December 2025, consists of it.
Mozilla doesn’t consider, for now, that the issue impacts different CAs, Jackson wrote on Mozilla’s coverage listing, and Chrome mentioned it checked each different CA certificates in its retailer and “discovered no different situations of this failure mode.”
What to Replace
Browsers get revocation pushed to them. Many different applications that verify TLS certificates, from Go binaries to something utilizing Python’s certifi bundle, don’t verify revocation information and hold trusting a sequence till their code or their root bundle adjustments.
Mozilla’s recommendation to anybody who runs a belief retailer: nothing is required the place purchasers reliably verify revocation and refuse connections after they can’t verify, the eight intermediates must be blocked now the place the software program can block particular person intermediates; and in any other case the operator ought to think about eradicating belief within the roots that signed them.
The fixes printed to date, and what every one does:
add border:
| Software program | Mounted in | What it does | Standing |
|---|---|---|---|
| Go |
1.27.3 and 1.26.10 |
Rejects any chain containing one of many eight keys (CVE-2026-111943) | Launched October 20, rebuild required |
| Firefox |
158.0.1 , ESR 115.43.1 and ESR 153.5.1 |
Carries the OneCRL block for installations that can’t obtain Distant Settings (
CVE-2026-113470 ) |
Launched October 20 |
| NSS |
3.131.1 |
Removes emSign ECC Root CA – G3 from the trusted listing | Launched October 20 |
| Python certifi |
2026.10.19 |
Drops emSign ECC Root CA – G3 from the bundle | Launched |
| Rust webpki-roots |
1.0.10 |
Drops emSign ECC Root CA – G3 | Launched |
| Homebrew ca-certificates |
2026-09-25_1 |
Excludes emSign ECC Root CA – G3, emSign Root TLS CA – G3 and AAA Certificates Companies by public key | Launched |
| Node.js | None but |
A
draft change would block the eight keys |
Pending |
| Composer ca-bundle | None but |
An
open change would take away emSign ECC Root CA – G3 |
Pending |
Go’s filter sits in the usual library and rejects any chain containing one of many eight keys, on Go’s personal verifier and on the macOS and Home windows system-verifier paths, and the change provides no setting to show it off. A program picks it up solely when rebuilt with the brand new launch; Go 1.25 and older are out of help and get no fixes.
Three of the fixes work by eradicating roots fairly than blocking the keys. certifi, webpki-roots, and Homebrew’s ca-certificates drop emSign ECC Root CA – G3 from their bundles, and Homebrew additionally drops Sectigo’s AAA Certificates Companies root and emSign Root TLS CA – G3.
That additionally cuts off each authentic certificates that chains to these roots. Mozilla, which made the identical change to NSS, mentioned some servers will grow to be unavailable to non-Firefox customers of its belief listing till these servers transfer to new certificates chains.
Firefox wants nothing except Distant Settings is disabled by coverage or blocked on the community. The October 20 releases carry the block listing for these installations.
Not one of the sources present a method to detect previous misuse of the keys past Chrome’s CT search, which covers solely logged certificates.
What Occurs to eMudhra
Mozilla eliminated emSign ECC Root CA – G3 from NSS on October 20. Chrome will take away the identical root in model 43 of its root retailer and is reviewing the standing of eMudhra’s different root in its retailer, emSign Root CA – G1, the Chrome Root Program mentioned, citing the seriousness of the incident.
How the keys left eMudhra and when stay open questions. Mozilla mentioned it’s working with the CA, different root applications and downstream belief shops on the foundation trigger and can publish extra when it could. eMudhra’s trust-services repository carried no discover in regards to the incident as of October 20.
Go has not named the CA on its problem, the place its launch notes cite “particular safety considerations round their operation”, and a commenter requested for the hashes within the patch to be defined.
Filippo Valsorda, who maintains the cryptography packages in Go’s customary library, replied that the keys are compromised and the certificates revoked, that Linux root shops are too poorly maintained for revocation to succeed in functions, and that placing the keys in code is the one possibility for now.