
Researchers have disclosed a brand new {hardware} assault, known as DDRop, that breaks the reminiscence safety in Intel and AMD confidential computing by silently dropping writes to a server’s reminiscence, so the processor retains studying outdated encrypted information as if it have been present.
The assault requires an attacker who already controls the server’s software program and might briefly entry the machine to insert a small circuit board, known as an interposer, between the processor and a reminiscence module.
The interposer prices beneath $200 to construct. DDRop works in opposition to Intel TDX, Intel Scalable SGX, and AMD SEV-SNP, the {hardware} that cloud providers use to maintain buyer information personal whereas it’s in use, even from the cloud supplier.
Confidential computing retains a server’s reminiscence encrypted, in order that even somebody with bodily entry to the machine sees solely scrambled information. To cowl the massive quantity of reminiscence {that a} cloud server makes use of, although, these designs omit a assure known as freshness. The processor can verify that reminiscence is encrypted, however not that it holds the most recent written worth, and that outdated encrypted information nonetheless decrypts appropriately.
DDRop turns that hole into an assault. When the interposer drops a write, the sooner worth stays in reminiscence, and the processor reads it again as if the replace had occurred. The encryption engine detects nothing fallacious.
DDRop is the primary energetic interposer assault to work on the DDR5 reminiscence in immediately’s cloud servers, the researchers say, and the primary to interrupt the integrity of an up-to-date Intel TDX system relatively than solely learn information from it.
Earlier DDR5 interposer assaults, similar to TEE.fail, have been passive. They listened to the reminiscence bus and needed to sluggish it right down to work with second-hand lab tools. Lively assaults that modified what the reminiscence noticed, similar to Battering RAM, labored solely on older DDR4, and DDR5’s redesigned command format blocks the address-swapping trick they used. DDRop will get round that by dropping writes as an alternative.
The interposer is a small board of switches that sits on the reminiscence bus and runs at full DDR5 pace. To drop a write, it forces an error on the command bus after which cuts the wire the reminiscence module makes use of to report that error, so the module quietly discards the command and the processor isn’t informed.
DDRop is the work of researchers at KU Leuven, ETH Zurich, Durham College, and Google, and is because of be introduced on the ACM CCS 2026 convention in November. The group says it’s releasing the interposer’s board designs, controller firmware, and assault code on GitHub, alongside their analysis paper.
Breaking Intel TDX
On Intel TDX, the researchers turned write-dropping into full management of a protected digital machine. TDX retains every digital machine’s web page tables encrypted and beneath the management of trusted firmware.
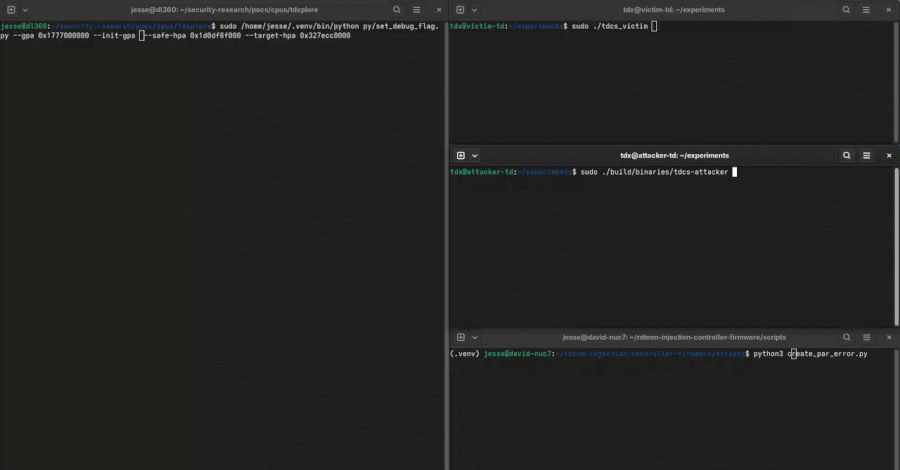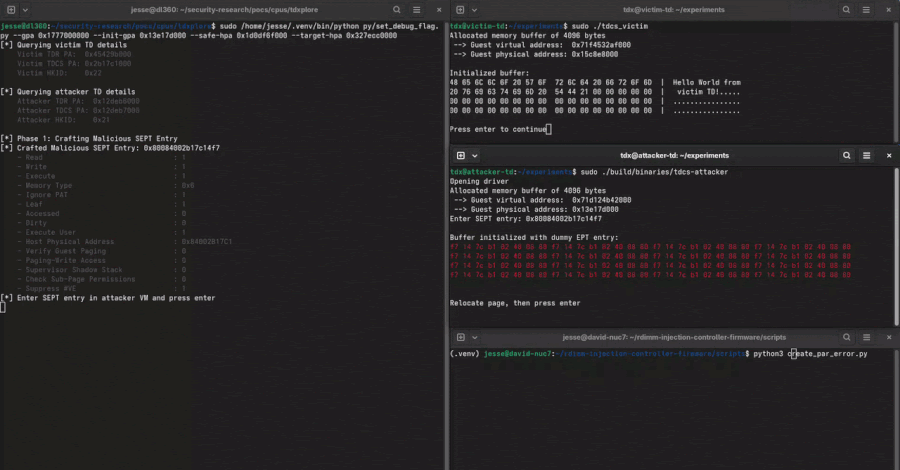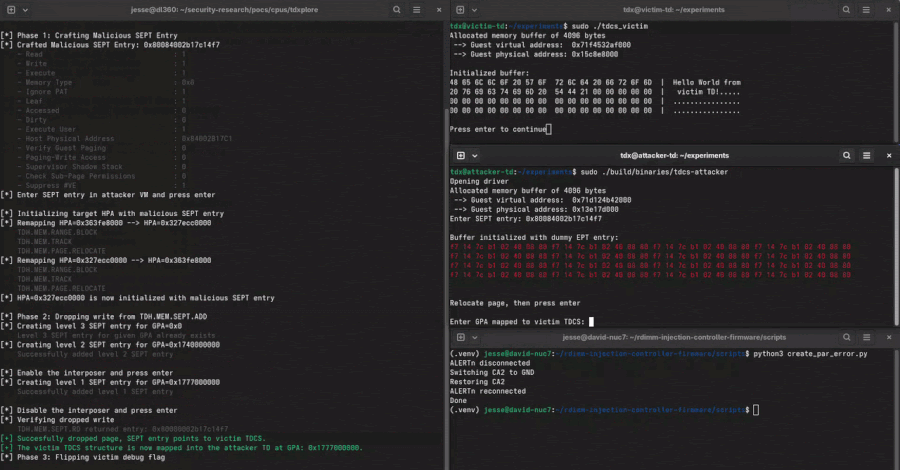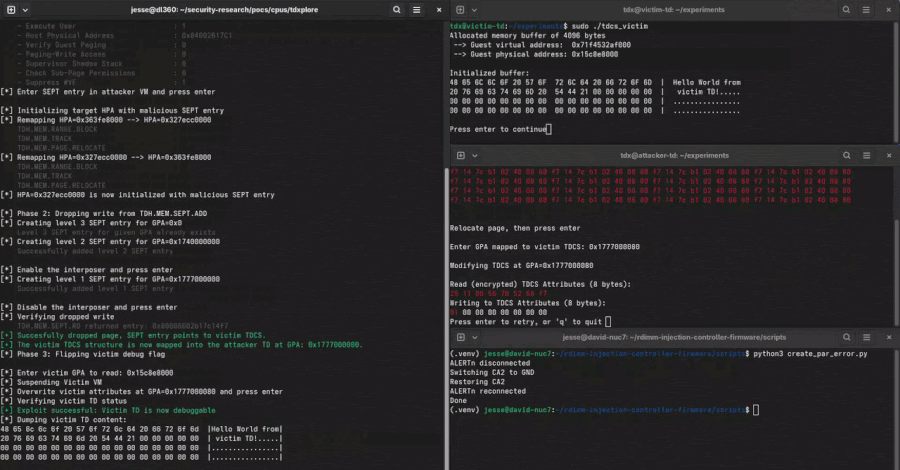
When that firmware writes empty entries to arrange a brand new web page desk, DDRop drops these writes, so the desk as an alternative retains attacker-chosen information left in that reminiscence beforehand. That lets an attacker’s personal digital machine map its reminiscence onto any bodily deal with and browse or change protected reminiscence.

With that entry, the researchers learn a sufferer digital machine’s personal reminiscence and switched a sufferer machine into debug mode, which allow them to copy its reminiscence in plaintext after which restore the unique information so the sufferer confirmed no signal of tampering.
In addition they overwrote the launch measurement {that a} digital machine makes use of to show to a distant buyer that it began in a identified, trusted state. With that modified, a digital machine the attacker controls might cross that verify as if it have been a trusted one.
Two of those outcomes, studying a sufferer’s reminiscence and toggling debug mode, have been proven solely beneath TDX’s default mode, known as logical integrity. TDX’s non-compulsory, stronger mode, known as cryptographic integrity, would block them, the researchers say, as a result of each contain altering information that belongs to a different digital machine.
Forging a machine’s personal attestation, they argue, would nonetheless work beneath the stronger mode, as a result of that write occurs contained in the attacker’s personal digital machine and beneath its personal key, so the {hardware} nonetheless marks the info as legitimate. Cryptographic integrity doesn’t add a freshness verify both, so it can not inform that outdated contents have been reused. Their check system didn’t assist the mode, so they might not verify this.
On AMD SEV-SNP, the result’s narrower. Dropping writes throughout AMD’s page-relocation function let the researchers copy the contents of 1 sufferer web page into one other, however the debug-mode and attestation-forgery assaults are particular to Intel TDX.
All three applied sciences encrypt reminiscence with out the freshness verify DDRop exploits, so all three are affected. Intel’s older Consumer SGX, utilized in some desktop and laptop computer chips, is just not, as a result of it makes use of a {hardware} integrity tree that catches stale information, although Intel has since retired it.
NVIDIA’s confidential-computing GPUs are out of attain, as a result of their reminiscence sits contained in the chip bundle the place an interposer can’t be fitted. The researchers didn’t check Arm’s CCA and say it could be affected too.
The assault is aimed toward cloud servers, not dwelling computer systems or telephones. Intel TDX, Scalable SGX, and AMD SEV-SNP are provided by main cloud platforms, together with AWS, Microsoft Azure, and Google Cloud, to guard buyer workloads. DDRop doesn’t present that any of those providers has been damaged into.
It reveals that an attacker with the fitting entry and an inexpensive piece of {hardware} might undermine the safety these providers depend on.
The researchers informed The Hacker Information they haven’t any proof of DDRop or a comparable energetic interposer getting used outdoors a laboratory.
No Easy Patch
There isn’t a easy patch. The weak spot is within the {hardware} design, the researchers say. As we speak’s scalable reminiscence encryption offers up the freshness verify in trade for shielding massive quantities of reminiscence, and shutting the hole for good would want new memory-encryption {hardware} that provides each integrity and freshness.
Software program modifications can elevate the bar with out eradicating the foundation trigger. These embrace limiting the memory-management options DDRop abuses, checking that necessary writes truly landed, and searching for an interposer throughout boot.
Intel and AMD have been knowledgeable about DDRop upfront by way of coordinated disclosure, and each acknowledged the findings and would problem safety bulletins on the disclosure date. Neither firm provided mitigation steerage or a timeline, the researchers mentioned.
AMD informed The Hacker Information that as a result of the assault requires bodily entry to the system, it falls outdoors the scope of the revealed menace mannequin for SEV / SNP.
Intel takes the identical place on bodily assaults in opposition to server reminiscence.
Intel has individually mentioned that bodily interposer assaults of this type fall outdoors the safety offered by its reminiscence encryption, and that it doesn’t plan to assign such assaults a CVE.
It has additionally described this analysis space as “out of scope, however not out of thoughts.” Intel’s non-compulsory cryptographic-integrity mode, obtainable on some present Xeon processors, already blocks a part of DDRop, and Intel says it’s engaged on stronger memory-encryption designs for future chips.
A kind of proposals, known as cache-line versioning, would add a freshness verify to the reminiscence bus. The researchers say it’s unclear whether or not it could cease DDRop, and that Intel has not mentioned whether or not it could.
AMD mentioned its bulletin on DDRop is because of be revealed on its product safety web page in a while September 14. Intel didn’t reply to a request for remark earlier than publication.
Constructing the interposer is reasonable. The researchers put the elements for one unit at about $159, not counting improvement or labor, and say it may be fitted in minutes after which pushed fully from software program.
As a result of it wants just one temporary go to to the machine, the researchers say the entry it requires might come from a rogue data-center worker, tampering someplace within the provide chain, or {hardware} seized beneath authorized compulsion.