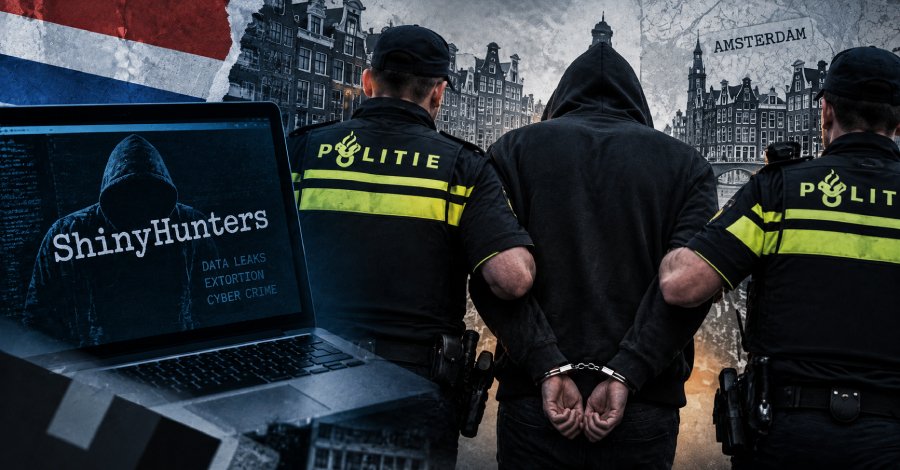

Dutch authorities have confirmed that they arrested a 24-year-old man from Amsterdam in reference to the ShinyHunters group.
“It’s true that this month a 24-year-old man from Amsterdam was arrested in an investigation into the hacker group ShinyHunters,” the Politie Landelijke Opsporing en Interventies stated in an X publish Monday.
Police stated the person is predicted to look earlier than the Rotterdam District Court docket on September 29, 2026.
Though regulation enforcement officers didn’t disclose any extra particulars, unbiased safety journalist Brian Krebs and DataBreaches.Internet recognized the arrested man as Pepijn van der Stap (aka Umbreon), who was beforehand apprehended in 2023 for his position in a sequence of information thefts and extortions.
Per DataBreaches.Internet, van der Stap was arrested on September 15, 2026. In 2023, it emerged that the person labored at cybersecurity firm Hadrian and volunteered on the Dutch Institute for Vulnerability Disclosure (DIVD).
“Working at Hadrian and volunteering at DIVD made me extra paranoid about maintaining appearances, and I really felt extra stress and paranoia as a result of I used to be working such lengthy hours,” van der Stap advised DataBreaches.Internet in June 2023.
“So sure, I used to be doing extra lawful work and far much less unlawful work however I grew to become extra paranoid about getting caught. The paranoia grew to become so excessive that I used to be anticipating a knock on the door at any time.”
He’s presently employed because the offensive safety lead on the Dutch firm Neo Safety, based on LinkedIn.
In his profile, van der Stap acknowledged his journey “hasn’t been a straight line” and that “I’ve seen safety from each side of the terminal, an expertise that taught me exhausting classes however in the end gave me readability: information is for constructing and defending, not breaking.”
When ShinyHunters was contacted by The Hacker Information in regards to the arrest, the group denied having any reference to van der Stap.
“That particular person has no affiliation with us. Frankly, we’re laughing,” the group stated. “Dutch police are chasing consideration and public favour after the huge embarrassment in [sic] results of the Odido hack. They wish to seem to be they’re forward of the FBI in investigating ShinyHunters.”
The event comes as ShinyHunters claimed credit score for its brazen hack of the U.S. Federal Bureau of Investigation’s (FBI) job utility web site apply.fbijobs.gov, stealing terabytes of delicate knowledge.
“This was all a advertising and marketing marketing campaign to guard our enterprise and actively fight disinformation,” a ShinyHunters consultant advised 404 Media. “If we made this assertion usually then this a lot consideration to our phrases and intentions would’ve by no means been this widespread.”
“We might have been ignored and disregarded. Nonetheless, now everybody is aware of what the difficulty is and what we’re doing. Everyone seems to be studying about it. We proved our factors on a number of events. We don’t care what the general public says and we aren’t affected by it nor will we cloud our judgement by exterior opinions and ideas.”
In a press release shared with The Hacker Information, the group reiterated once more that the assault on the FBI’s programs was not extortion and that it is not financially motivated.
“We perceive why many misinterpreted this as extortion and are satisfied we’d publish this knowledge and/or misuse it reminiscent of promoting to 3rd events as a consequence of our historical past in previous operations which has by no means concerned a authorities entity of prominence,” the spokesperson stated.
“We once more wish to emphasise that this isn’t extortion, it was by no means one to start with, not a menace, not a ransom, and never financially motivated. Nothing will occur. We’re well past this example in our enterprise operations and we confidently imagine we now have been profitable as a consequence of seeing a current inflow of success in our operations.”
Though the group stated it exploited a brand new zero-day flaw in Oracle PeopleSoft to achieve unauthorized entry and siphon the information, it is now assessed that ShinyHunters employed a URL-encoding trick to bypass internet utility firewall (WAF) guidelines designed to mitigate CVE-2026-35273.
(The story was up to date after publication to incorporate a response from ShinyHunters.)