
When phishing can more and more move acquainted checks, avoiding or limiting the injury will depend on how rapidly your organization can detect and comprise the assault

28 Sep 2026
•
,
6 min. learn
A lot of right this moment’s phishing makes an attempt are not betrayed by poor grammar, a sketchy URL or a crude login web page. To make certain, it does nonetheless pay to look out for these purple flags, however their absence doesn’t make a message reputable. Fashionable social engineering schemes are more and more designed to resist scrutiny and to supply reassurance the place an assault may as soon as have left some giveaways.
By extension, email-borne threats specifically at the moment are constructed to satisfy as little resistance as potential. They subvert reputable workflows and attain workers mid-task, when their accounts are authenticated and any incoming requests for motion really feel like a part of an bizarre working day. Some strategies go after reside classes themselves, with attackers shifting their focus from stealing passwords to stealing authentication tokens.
With the cybercrime-as-a-service economic system thriving, anybody with ailing intent should buy a ready-made phishing package that arrives full with the equipment for capturing logins. In the meantime, AI has slashed the quantity of effort and time wanted to analysis numerous targets and strike the correct tone for every of them. These shifts are growing sooner than many corporations can come to grips with them.
What the coaching taught
Dangerous grammar was the primary inform to go. Function-built AI instruments now make it trivial to scrub up the language and even tailor the lure for every recipient. As a substitute of one-and-done makes an attempt, some dangerous actors are additionally utilizing AI to construct rapport with their marks earlier than ultimately ‘getting in for the kill.’ Nowadays, polished or culturally nuanced writing says nothing about whether or not a message is real.
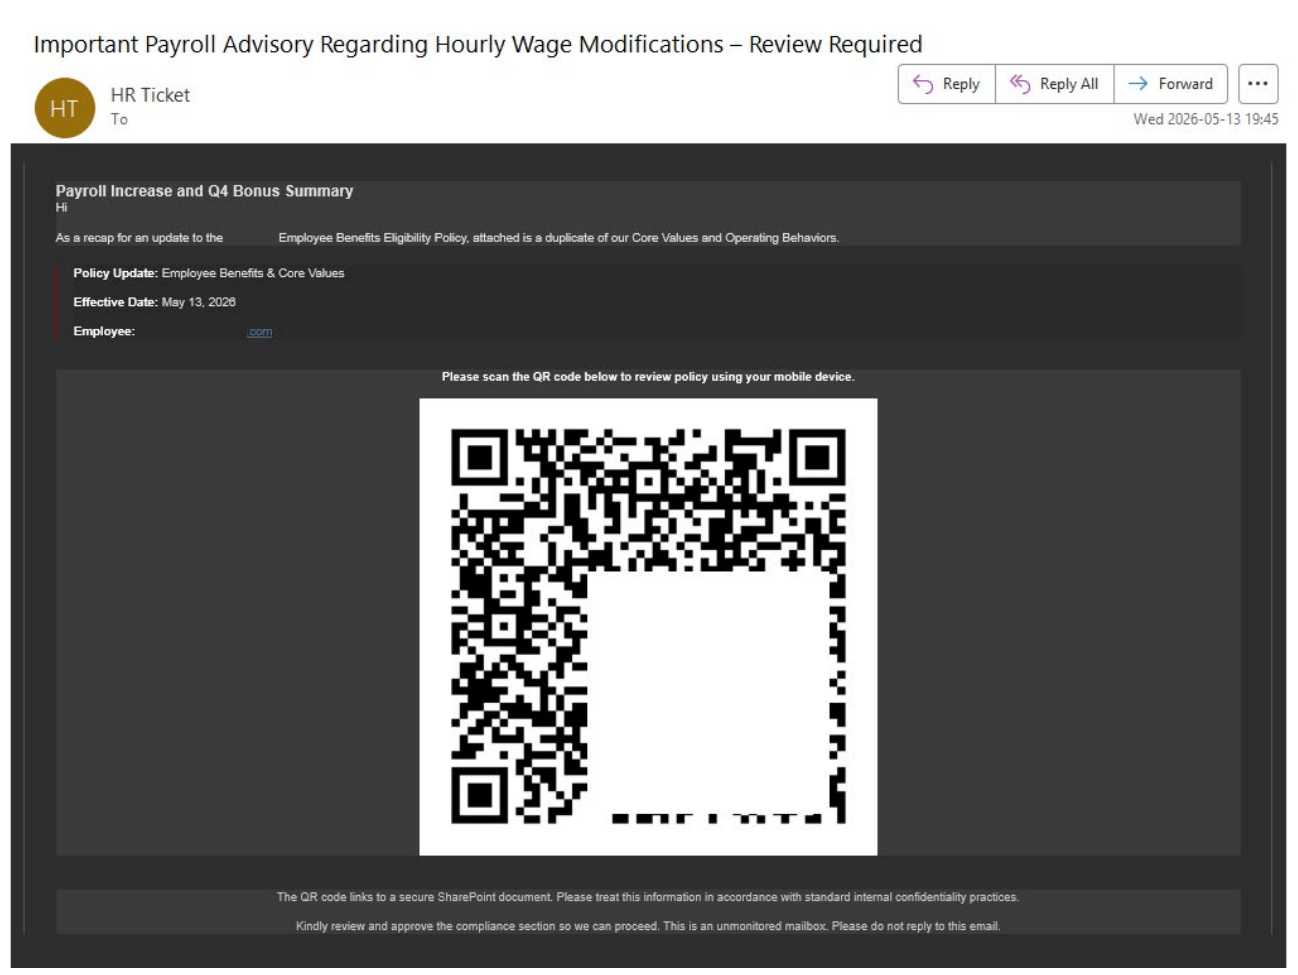
The URL hyperlink has additionally grow to be an ‘unknown amount.’ When the vacation spot URL is hidden inside a QR code, there’s nothing to hover over. What’s extra, the code is scanned on a cellphone, so the standard controls that defend company-issued laptops don’t apply. The ‘gadget hop’ additionally signifies that the corporate might have a tough time growing a full image of the assault. To place issues into perspective – QR code phishing accounted for one in 9 detected phishing emails in ESET’s telemetry within the first half of 2026 whereas Microsoft ranks QR codes because the fastest-growing email-based assault vector.
How in regards to the pretend login web page – the one which consciousness coaching supplies conveniently spotlight in a purple rectangle? ConsentFix, for one, dispenses with it solely. The sufferer lands on a compromised however reputable web site, the place a pretend CAPTCHA-style immediate sends them by an actual Microsoft sign-in circulate earlier than redirecting them to a URL containing an OAuth authorization code. They’re then instructed to stick that URL again into the compromised web page, permitting the attacker to extract the code and change it for entry and refresh tokens. Importantly, as soon as the sufferer already has an lively Microsoft session, no password or multi-factor authentication (MFA) immediate is triggered to foil the assault.
On a associated be aware, detections of ClickFix – a social engineering trick that dupes the sufferer into pasting a command into their very own terminal – proceed to soar. Its variant often known as AI-fix has been noticed inserting pretend troubleshooting directions on reputable domains that belong to Anthropic, OpenAI and Microsoft. In the meantime, a pretend advert blocker often known as CrashFix, factors targets to the official Chrome Net Retailer, and even waits an hour after set up earlier than displaying its first bogus alert, prone to sever the psychological hyperlink between trigger and impact.
As neither seeing nor listening to is believing as of late, a recognizable face or voice doesn’t at all times present conclusive proof of who’s behind the request. Staff who encounter lifelike however pretend audio and video in the midst of work usually lack the chance to look at each body or to pay attention or look ahead to potential artificial tells revealed by older deepfake creations. Certainly, even an imperfect imitation might be convincing when the context feels believable – similar to when a finance worker joined a name populated by deepfake variations of senior colleagues and nonetheless ended up making wire transfers price greater than US$25 million.
Don’t cease at human error
Blaming an incident merely on “human error” identifies only one hyperlink within the chain with out explaining why a momentary lapse in judgment in the end triggered a full-blown disaster. Safety consciousness coaching can instill good habits and sharpen the attention for fraudulent messages, however it might probably’t insert an apparent purple flag right into a message with out one, notably now that many assaults anticipate the checks that workers have discovered to make. The worker’s click on offers the attacker a gap, however the eventual injury, or lack thereof, will depend on the preventive controls nonetheless standing and on how rapidly the corporate detects and comprises what follows.
ESET’s Q1 2026 MDR report additionally discovered that workers usually acknowledge phishing and spam messages for what they’re, but go on to easily delete them, as a result of no person has established the place such messages needs to be reported. The corporate loses the prospect each to show different workers about new ‘methods of the phishing commerce’ and to glean some wider classes from the assault. It might miss an early alternative to analyze whether or not the message is a part of a large-scale marketing campaign.
On this be aware, ESET’s SMB Cyber Readiness Index discovered that the adoption of consciousness coaching is highest amongst companies which have already suffered a number of incidents. The identical survey discovered companies worrying most about AI-powered malware, regardless that precise incidents nonetheless start with phishing, unpatched software program, gaps in monitoring and weak passwords. AI’s position is in making well-established strategies sooner and extra scalable.
Don’t belief – confirm as a substitute
Dangerous actors now reproduce most of the indicators of legitimacy that most individuals have discovered to hunt, so controls have to depend on verification towards one thing that the message did not present. Fee requests and different high-stakes actions more and more require further checks, together with affirmation by a verified channel and probably involving a second approver.
When something convincing might be fabricated with ease, context additionally issues greater than ever. This requires selecting up the assorted ‘breadcrumbs’, similar to community connections and file modifications, which are left as an assault passes by the corporate’s surroundings. Every of them might look unremarkable by itself, however a number of seemingly disparate artifacts might level to an ongoing assault. Automated evaluation can group associated alerts throughout accounts and gadgets whereas analysts set up whether or not the sample quantities to an lively compromise and how one can reply. State-of-the-art managed detection and response (MDR) provides investigative prowess and capability, turning weak alerts right into a coherent story and giving a small crew entry to capabilities that it couldn’t employees and function alone.
ESET MDR telemetry exhibits that nearly 70% of safety incidents happen throughout typical enterprise hours, with 90% falling on workdays. In the meantime, the ESET SMB Cyber Readiness Index – which is predicated on a survey amongst 4,400 decision-makers – factors to how lengthy investigations usually run: 41% are accomplished inside a fortnight; one other 34% take two to 6 weeks. The latter specifically is a timeframe that an organization can hardly take up with out extreme operational disruption.
For SMBs specifically, the assets wanted to look at over the increasing assault floor don’t transfer in lockstep with the rising scale and class of adversarial strategies. 100-person firm might rely upon the identical forms of cloud, identification, cost and collaboration methods as a a lot bigger one, nevertheless it has far fewer folks out there to maintain tabs on them. For a lean IT crew, investigation competes with different duties concerned in conserving methods working, and sprawling toolsets danger forcing understaffed groups to handle inefficient “swivel-chair environments.”
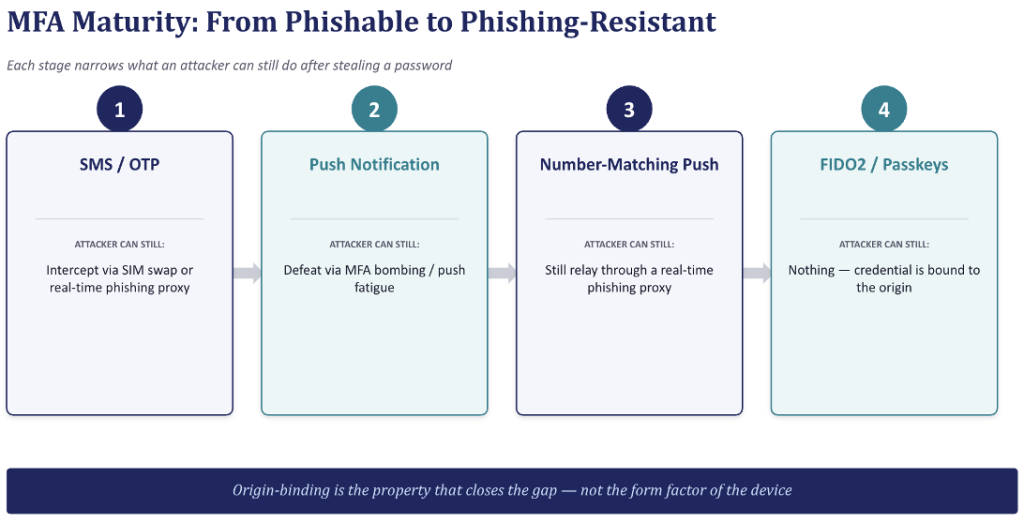
Multi-layered preventive foundations, together with phishing-resistant authentication and session controls, go a great distance towards defeating credential-stealing makes an attempt. Social engineering more and more exams greater than the recipient’s eye for element, and the result additionally hinges on what occurs within the minutes and hours following the press. Any workable safety plan should account for assaults that workers don’t spot. AI helps cope with the amount and velocity concerned, whereas skilled analysts can assess the proof and direct the response.