For almost a decade, multi-factor authentication has been the management each safety chief factors to when requested how they’ve decreased account takeover threat. It sits on nearly each compliance guidelines and almost each cyber insurance coverage questionnaire, and for good cause — including a second issue to a password login closed off an infinite share of credential-based assaults, and organizations that adopted it early noticed the payoff in fewer compromised accounts.
That confidence is now outdated in a approach many safety groups haven’t absolutely registered. The MFA adoption fee reported to a board or an auditor not often distinguishes between the strategy used to fulfill it. A push notification and a {hardware} safety key each rely as “MFA enabled” on the identical compliance report, and so does a one-time code despatched by SMS — regardless of sitting at wildly completely different factors on the spectrum of what an attacker can defeat. Uber’s 2022 breach, the MGM Resorts incident, and a rising record of enterprise intrusions traced again to compromised assist desks all shared the identical root trigger: MFA was current, and MFA nonetheless failed, as a result of the strategy in place was by no means constructed to withstand a focused attacker.
The place push and OTP fail
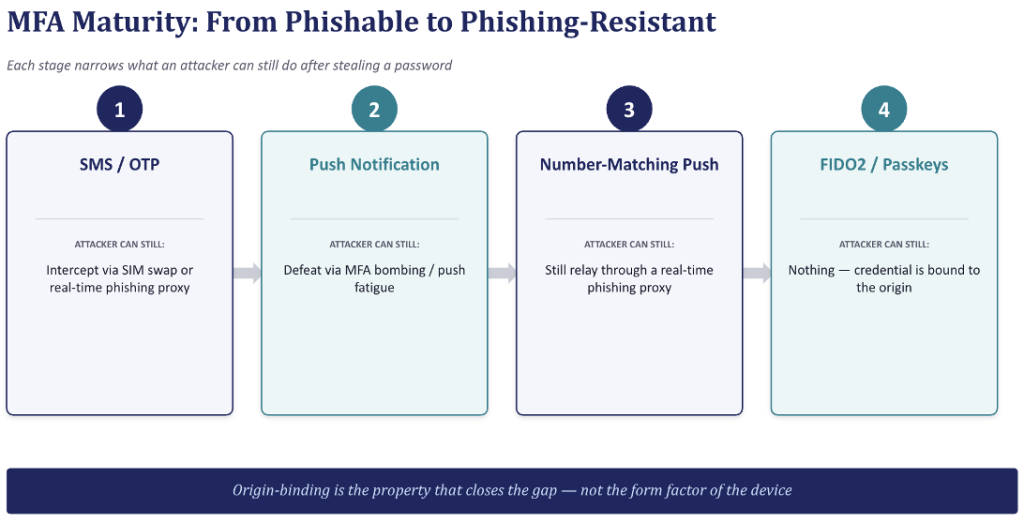
Push notification MFA got here first for many organizations, primarily as a result of it was the trail of least resistance — nothing for the consumer to recollect, nothing to kind and IT may flip it on throughout the corporate in a day. That very same ease of rollout turned out to be precisely what made it straightforward to interrupt. Attackers discovered they didn’t have to steal something refined. They simply wanted a stolen password and the willingness to ship the identical approval immediate to somebody’s cellphone again and again, typically for hours, till the consumer acquired aggravated sufficient — or drained sufficient, or confused sufficient — to faucet approve. Safety groups name this push fatigue or MFA bombing. It really works typically sufficient that it’s now probably the most widespread methods attackers get previous MFA that’s technically “on.”
The OTP downside is easier and uglier than push fatigue. It’s only a code, and a code could be gotten. Typically an attacker convinces a cellular service to maneuver a sufferer’s cellphone quantity onto a SIM they management — a rip-off that’s quietly drained crypto wallets and company e-mail accounts for years now. More and more, although, it doesn’t even require that a lot effort. Phishing kits constructed round reverse-proxy instruments can now intercept an OTP in actual time — the sufferer varieties their password and code into what seems like a standard login web page, unaware that the web page is quietly forwarding every part to the true website on the attacker’s behalf, session and all.
Each failure modes share a easy design hole. The authentication technique by no means verifies that the individual approving the login and the system requesting it are speaking to the identical, respectable vacation spot. That’s the property attackers exploit, and it’s precisely the property newer requirements have been constructed to shut.
Ashish Mishra
The property that closes the hole
Ask what stops a phishing website from working towards FIDO2 or a passkey, and the reply isn’t cleverness — it’s math. A passkey has no code to steal within the first place. What will get created throughout enrollment is a cryptographic key pair locked to at least one web site, completely, and a lookalike area merely isn’t that web site, regardless of how convincing it seems to a human eye. The browser checks the origin earlier than anything occurs, finds it doesn’t match and the login try dies proper there — earlier than the consumer can ever be fooled into approving one thing they shouldn’t.
This origin-binding is your entire level, and it’s value being exact about it, as a result of distributors market a variety of merchandise underneath the “phishing-resistant” label with out all of them assembly the bar. A {hardware} key that also permits a fallback OTP choice isn’t resistant if that fallback stays reachable. A passkey saved insecurely on a shared or unmanaged system narrows the hole however doesn’t shut it totally. The energy of the management is dependent upon the total authentication path, not simply the strongest hyperlink in it.
The migration no person desires to confess is difficult.
If the technical argument for phishing-resistant MFA is that this sturdy, the pure query is why so many organizations nonetheless run on push and OTP. The trustworthy reply isn’t ignorance. It’s friction, and pretending in any other case doesn’t assist anybody plan a migration.
Older on-premises techniques weren’t constructed with WebAuthn in thoughts, and neither have been some SaaS platforms nonetheless in vast use — so someone finally ends up bolting on a compensating management or discovering a workaround, as a result of ripping and changing isn’t practical on most timelines. {Hardware} keys aren’t free both — multiply even a modest per-user price throughout a big workforce, and it provides up quick, and in contrast to a push notification, a misplaced or broken key turns into an precise assist ticket. Then there’s the half no person likes admitting out loud: workers who’re used to tapping approve on their cellphone in two seconds are going to note, and complain, when the brand new course of means digging a bodily key out of a bag and plugging it in. None of which means the migration isn’t value doing. It means it wants a rollout plan behind it as a substitute of a memo telling everybody to modify by Friday.
Beginning small, on goal
The organizations making actual progress on this aren’t changing their whole workforce in a single day. They’re beginning the place the danger is concentrated, and the resistance to alter is lowest: administrator accounts, id supplier entry and anybody with the flexibility to reset one other consumer’s credentials. These are the accounts attackers goal first exactly as a result of compromising one unlocks every part downstream, they usually’re additionally the accounts the place a small inhabitants of technically succesful customers can take in a brand new workflow with out a lot disruption.
Finance and engineering come subsequent, together with some other group sitting near delicate techniques. Legacy functions that may’t but assist the brand new commonplace don’t get a everlasting cross — they get a conditional entry coverage within the meantime and an actual deadline for when the exception closes. SMS-based OTP ought to get the identical remedy, besides with much less persistence. Of each technique nonetheless in widespread use, its weaknesses are the perfect documented and probably the most actively exploited, which is precisely why it ought to carry a sundown date as a substitute of sitting round indefinitely as a fallback.
Attackers have already retooled across the MFA most organizations deployed years in the past. Ready for an even bigger incident to justify the migration isn’t a method; it’s a guess that your group received’t be subsequent. Begin with an trustworthy audit: not which accounts have MFA enabled, however which technique is defending every one.