
Information breach notifications are telling victims lower than ever. What the corporate leaves out can nonetheless form what you do subsequent.

12 Oct 2026
•
,
7 min. learn
Publicly reported knowledge breaches hit an all-time excessive within the US final 12 months, with over 3,300 incidents recorded and almost 280 million sufferer notices mailed out. However are all of those well worth the paper they’re written on? More and more, they lack essential particulars.
As the quantity of information breach incidents will increase, there’s a rising probability that you just’ll be caught up in a single. In accordance with the non-profit Identification Theft Useful resource Heart (ITRC), over 471 million sufferer notices went out within the first half of 2026 alone. But only a quarter (24%) contained particulars concerning the assault vector. That’s the bottom ever price recorded by the ITRC.
That is unhealthy information for customers, company victims and policymakers. A scarcity of element prevents you from understanding your true danger publicity or taking significant motion to restrict the fallout and probably stop it from occurring once more. ITRC’s personal knowledge reveals that three-quarters of victims need a plain-language listing of precisely what knowledge was compromised.
Why are organizations cagey about releasing particulars?
There are lots of the reason why a breached entity is likely to be reluctant, or unable, to share the total particulars of a breach incident. Disaster comms groups could wish to get some info out to prospects as soon as information of an incident surfaces, to protect repute and stop dangerous hypothesis from mounting. However they could not but know the total image.
Info similar to precisely what was compromised and the way could take weeks and even months to ascertain, particularly if it includes massive knowledge volumes. And if there’s an opportunity that broader disclosure may assist different risk actors (by revealing the assault path and defensive weaknesses) or the adversary itself (whether it is nonetheless contained in the community) then it might be withheld.
There are additionally extra financially pushed motives for limiting disclosure. Extreme info-sharing would possibly impression the share worth, repute, and/or aggressive benefit of a corporation.
The reality is that disclosures to regulators will normally characteristic much more element. The victims, in the meantime, are sometimes left greedy at straws.
How do you interpret a breach discover?
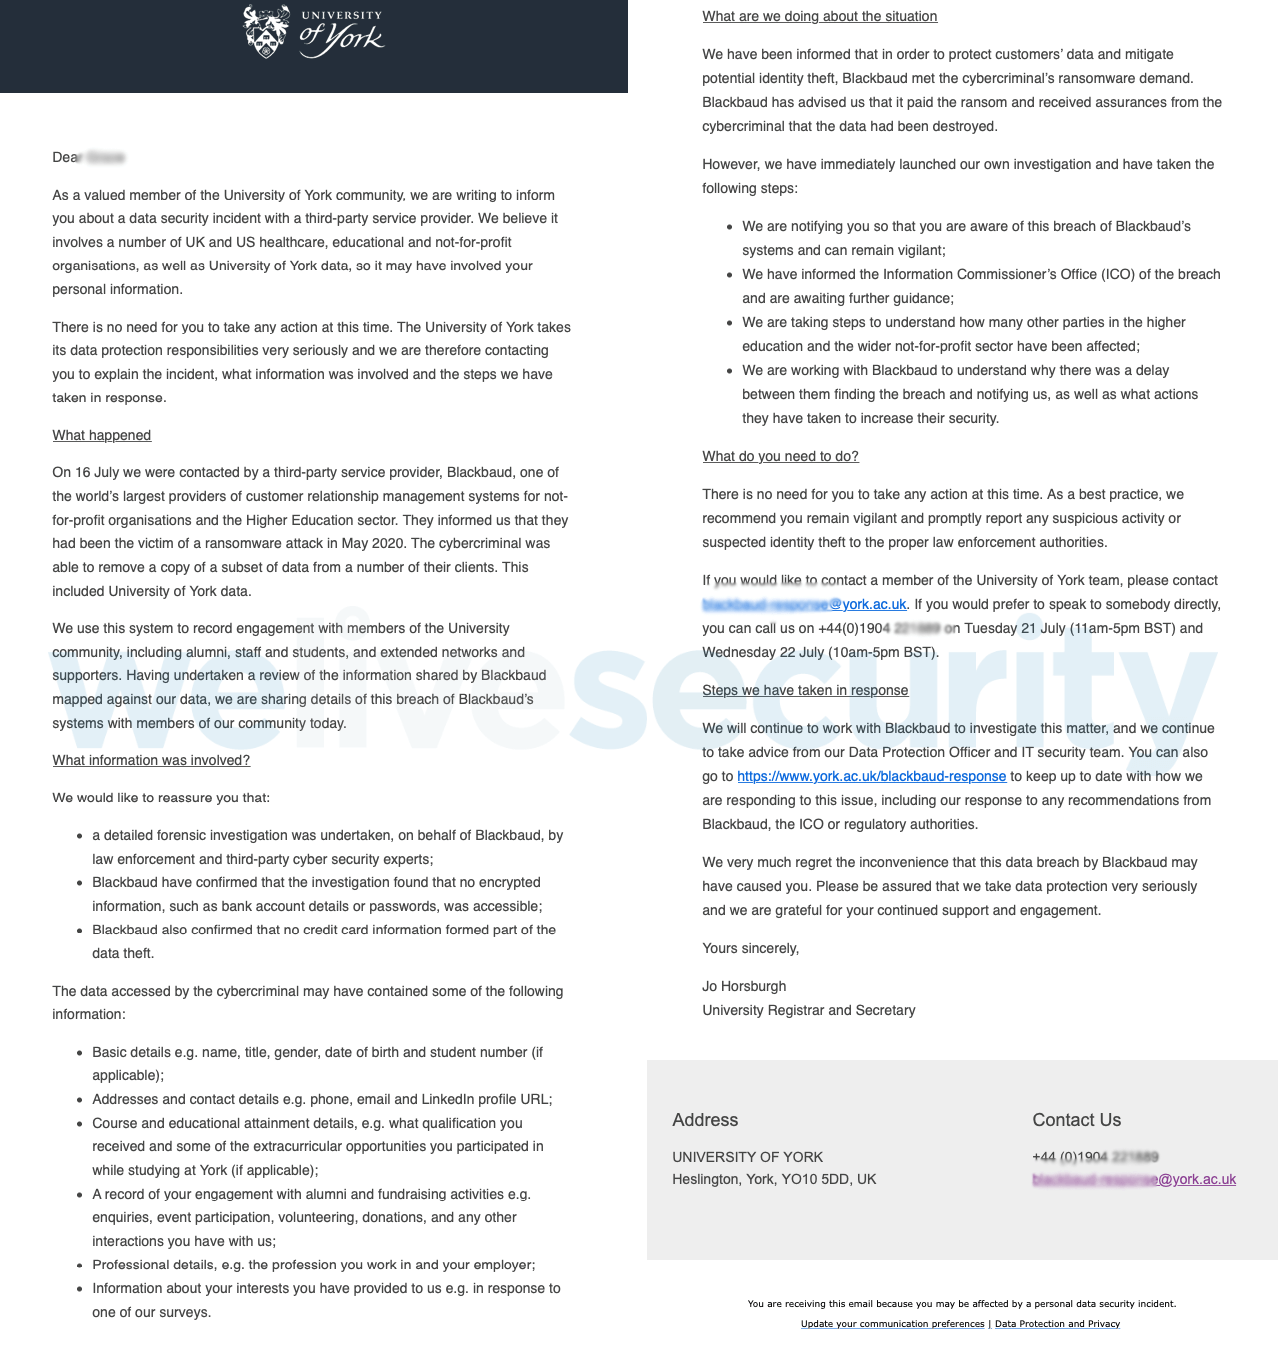
The language utilized in a breach notification will be complicated. If it says your knowledge was “accessed” it doesn’t essentially imply it was truly stolen (i.e., “exfiltrated”). And simply because a breached firm claims they’ve seen “no proof of misuse” there’s completely no assure that that is true. What they see and what’s truly occurring on the cybercrime underground will be two very various things.
Equally, if an organization says you “could have been affected” it doesn’t imply your knowledge was positively within the trove that was compromised – though it’s at all times finest to err on the facet of warning.
As talked about, breach notices could also be cagey about precisely how the hackers received in and stole the info (the assault vector). However for victims, this is likely one of the much less essential items of data. What you actually need to know is:
- Whether or not your knowledge was ‘solely’ accessed or truly taken (though it’s finest to imagine the worst till you hear completely different)
- What knowledge was taken, as it will decide your subsequent steps (e.g., whether or not you could reset passwords, name your financial institution, cancel playing cards and many others)
- When the incident occurred and the way lengthy it lasted, as this can assist you to examine in opposition to suspicious exercise on affected accounts
- What the corporate itself is telling you to do when it comes to particular subsequent steps
Is the notification even reputable?
It’s additionally essential to examine if the discover is real. Scammers have grown smart to the truth that breach notifications are an more and more frequent incidence. And one thing that recipients are prone to take discover of and act on.
For that cause, you need to by no means click on by on any unsolicited breach notification e mail or message. Generally the said incident would possibly by no means have occurred. On different events the unique breach is likely to be actual however the notification message is a rip-off.
In any case, your first port of name needs to be to examine with the breached group. Do that not by replying to the message or utilizing contact particulars listed there, however verifying them elsewhere.
What ought to occur subsequent?
When you’ve confirmed the notification is reputable, ask the group concerned if it may well make clear any extra particulars. Then contemplate the next steps, that are depending on the kind of knowledge that will have been compromised:
- For private particulars like e mail and residential deal with, title and telephone quantity, be looking out for follow-on phishing messages and calls. By no means click on on hyperlinks in these messages or hand out info with out verifying their authenticity individually
- For well being data or buyer account particulars, be careful for extra focused phishing makes an attempt as per the above
- For usernames and passwords, change the credentials instantly for this account and wherever else it was used. Change on two-factor authentication (2FA) for an additional layer of safety
- For financial institution or card particulars, contact your financial institution or card supplier and inform them what occurred. Ask for a alternative card and monitor your accounts for suspicious exercise
- For presidency ID (e.g., passports, driver’s license) comply with the recommendation of the issuer. A alternative could also be wanted
- For monetary and id data, monitor your accounts, contact the related monetary establishment(s), change your logins (if related), and contemplate credit score monitoring and a credit score freeze
Is a credit score freeze or credit score monitoring the most suitable choice?
Many breached organizations supply free credit score monitoring for a 12 months following an incident. Some additionally supply a credit score freeze. However which is healthier? It’s essential to know the distinction.
- Credit score monitoring companies detect when one thing adjustments in your credit score file, probably indicating a fraudster has your particulars and is making an attempt to get a brand new line of credit score out in your title.
- Credit score freeze blocks most entry to your credit score report, so scammers can’t simply open a brand new account utilizing your particulars.
So a credit score freeze is extra helpful, but when both is obtainable, reap the benefits of them. The 2 work finest collectively: place a freeze and settle for any free monitoring you’re supplied. Simply remember that credit score monitoring is barely an alert service. It gained’t truly stop follow-on fraud.
As extra of us broaden the variety of organizations we do enterprise with, and as hackers get higher at compromising those self same corporations, the percentages of receiving a breach notification will proceed to shorten. Nevertheless it doesn’t must be the tip of the world. Keep alert and keep knowledgeable to attenuate the chance of follow-on fraud.
Steadily requested questions (FAQs)
How do I do know if a breach notification is real or a rip-off?
By no means click on by on any unsolicited breach notification e mail or message. Examine first with the breached group, and never by replying to the message or utilizing contact particulars listed there, however verifying independently.
Why have I acquired a breach notification from an organization I’ve by no means heard of?
It could be a provider you’ve by no means handled instantly, similar to a payroll supplier or knowledge processor utilized by an organization you do enterprise with. It could even be a rip-off, or it’s possible you’ll merely not have performed enterprise with them for a very long time and it might be a historic breach. Both approach, learn the data rigorously and call the corporate instantly for extra info if it seems like delicate monetary or private info was uncovered.
What ought to I do if my password was uncovered in a breach?
Change the credentials instantly for this account and wherever else it was used. Change on two-factor authentication (2FA) for an additional layer of safety.
What ought to I do if my monetary particulars and id info had been uncovered in a breach?
That is extra critical. Monitor any related accounts for suspicious exercise and call the related monetary establishment(s). Change your logins (if related) and contemplate credit score monitoring and a credit score freeze.
Ought to I take advantage of credit score monitoring after a breach?
Credit score monitoring companies detect when one thing adjustments in your credit score file, probably indicating a fraudster has your particulars and is making an attempt to get a brand new line of credit score out in your title. It gained’t truly stop follow-on fraud, however it may be a helpful alerting mechanism. If supplied without spending a dime, settle for it. A credit score freeze is price including: it’s free within the US and blocks most entry to your credit score report.